找到 3817 篇与 绿色软件 相关的结果 - 第 32 页
-
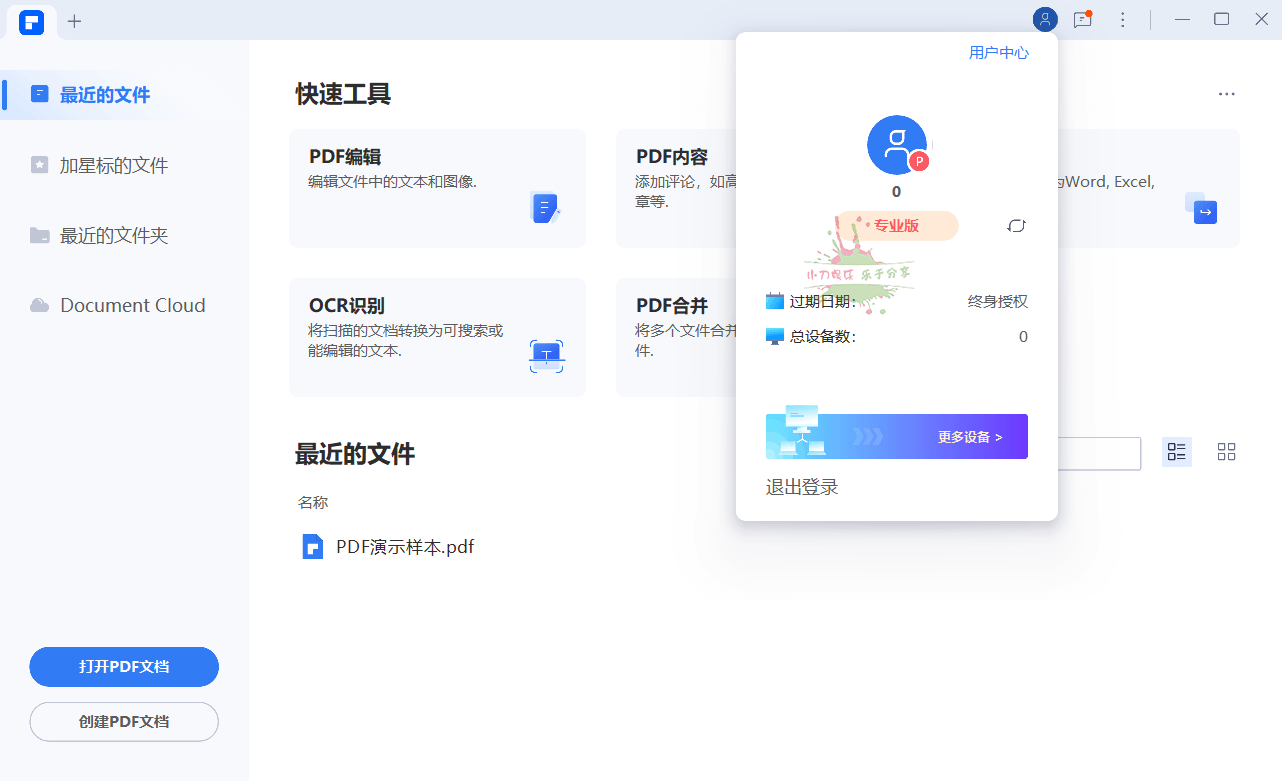
 万兴PDF专业版v13.0.1.4467完整版 软件介绍 万兴PDF专家(Wondershare PDFelement)是一款国产PDF文档全方位解决方案.万兴PDF编辑器软件万兴PDF中文版,专注于PDF的创建,编辑,转换,签名,压缩,合并,比较等功能.万兴PDF专业版PDF编辑软件,以简约风格及强大的功能在国外名声大噪,除了传统功能外,还提供OCR扫描,表格识别,创建笔记,翻译服务,云同步等功能. 软件万兴PDF专业版v13.0.1.4467完整版 图片2万兴PDF专业版v13.0.1.4467完整版 图片6 更新日志 What's New in Wondershare PDFelement for Windows https://pdf.wondershare.com/pdfelement/whats-new.html 版本更新_发版记录 -万兴PDF编辑器(万兴PDF国内中文站) https://pdf.wondershare.cn/whats-new.html 万兴PDF专家 v13.0 更新内容(2026年9月 ) 新增知识空间,整合多源资料,可生成摘要、思维导图等内容 协议助手升级,合同审核、对比、翻译、签署全流程一站式 支持按角色高亮合同条款,跨境协议自动翻译,风险点清晰 AI模型可选多档,批量摘要、校对、翻译处理效率更高 智能自动脱敏,识别敏感信息一键打码,保护文档隐私 优化大文件加载渲染速度,翻页缩放操作流畅不卡顿 图文编辑、书签拖拽体验优化,日常操作更顺手 软件功能 万兴PDF阅读器 + 万兴PDF编辑器 + PDF创建器 + PDF转换器 + PDF扫描器 + OCR识别工具 支持PDF文档或PDF扫描件转换为RTF/Word/Excel/PPT/EPUB/HTML/Text/图片等常用格式 无损转换PDF文档,转换的PDF文件还原程度高,号称能够最大程度的保留原有是布局不改变 表单处理功能:可一键识别表单填写区域,支持数据识别,生成表格文档,批量处理PDF表单 数据提取功能:表单归档和数据录入,自动识别可填写表单域,无需转换格式,即可直接填写 定义表单选项形式,比如:文本字段,复选框,单选按钮,组合框,列表框,按钮或签名域 编辑功能,能让用户直接在PDF中进行文字编辑,跟使用Word一样 注释工具:包括高亮、下划线、删除线、画笔、签章、文本标注等 OCR字符识别技术:扫描件也可以OCR图文转换为可编辑的文档 ⬇️ 下载地址 下载后请先检查文件完整性,如有问题请在评论区反馈

-
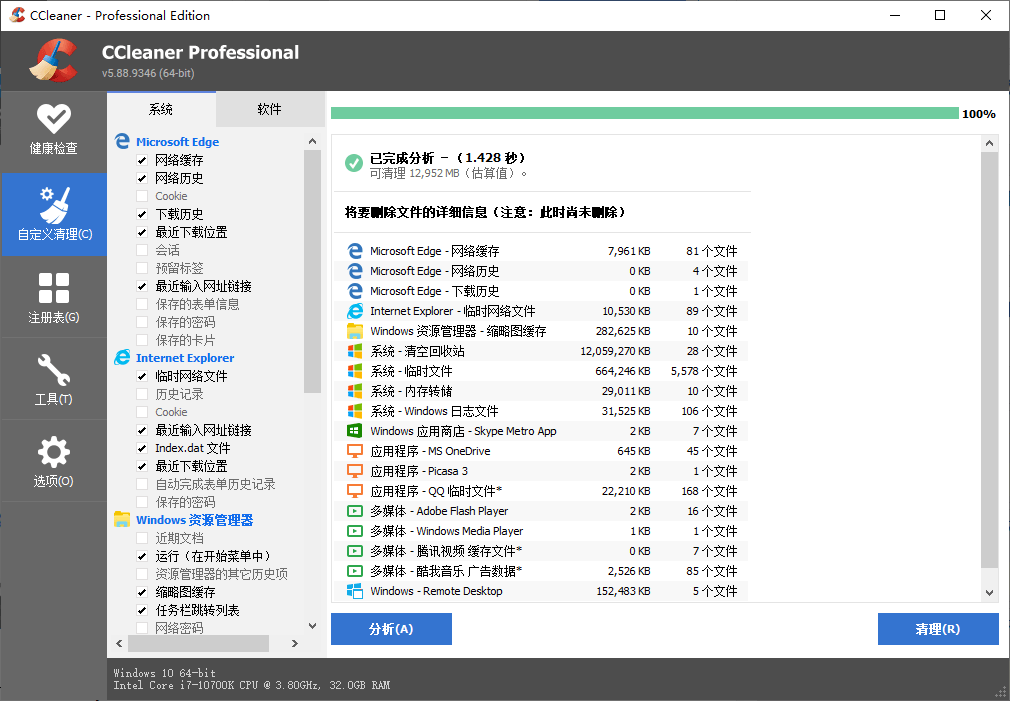
CCleaner v7.11.1509中文专业版 软件介绍 CCleaner是一款免费的系统优化和隐私保护工具,它的体积小、扫描速度非常快,支持自定义清理规则,增强了应用程序清理范围和效果。CCleaner是Piriform(梨子公司)最著名广受好评的系统清理优化及隐私保护软件,也是该公司主打和首发产品,可以有效清除各种系统垃圾文件及应用程序垃圾,同时具备系统优化功能;可以对临时文件夹、历史记录、注册表冗余条目等进行垃圾清理,附带启动项管理、软件卸载功能。 软件CCleaner v7.11.1509中文专业版 图片2 CCleaner v7.11.1509中文专业版 图片4 更新日志 ccleaner.com/ccleaner/version-history 2026.09.03 v7.11.1509 修复部分用户无法完成新手引导流程的问题 CCleaner 7.0 新版特性 全新现代化界面:响应更快,操作更流畅。 多主题支持:提供浅色、深色及自动跟随系统三种主题模式。 扩展硬件支持:新增ARM64架构兼容,完美适配新一代设备。 全新的卸载引擎 → 能一次性卸载多个软件,避免弹窗,还能暂时删除测试性能,想恢复随时可以恢复! 磁盘分析器升级 → 分析大量重复文件,支持预览查看,删除方式更多样,界面全新设计支持深色模式! 云硬盘清理器 → 接管Google Drive和OneDrive,找重复文件、大文件、旧文件,快速查看释放空间! 性能优化功能 → 专利技术让PC提速34%,电池续航延长30%,游戏体验更流畅! 驱动更新功能 → 改善PC视觉效果、声音效果和网络连接,防止软件错误和崩溃! 软件更新功能 → 自动更新所有软件,在安全漏洞被发现前就清除,省时省力! 健康检查功能 → 全面分析PC,推荐快速修复方案,自动调整更新! 6.26 版本开始主界面「注册表」按钮已移至「工具」界面 补丁说明 安装“ccsetup_offline_setup.exe”运行 必须手动激活许可密钥:EGYPT-EGYPT-EGYPT-EGYPT-EGYPT 版本特点 by zdbryan 采用专业版安装版的主程序,集成注册码,将配置便携式保存 反汇编处理,实现INI配置文件便携化后也能使用智能清理功能 官方版开启便携不能使用智能清理功能,选项智能清理是灰色 禁止每次启动临时创建「谷歌检测Api接口模块」,加快启动速度! 禁止后台各种联网请求,提升启动速度,无网络情况下启动不卡顿 后台联网请求包括:发送匿名数据、检测许可密钥、检测升级提示 官方原版每次启动会后台偷偷联网请求avast安全中心上传匿名数据 移除界面右上角按钮:「帮助按钮」/「许可证管理」、底部:「检查更新」 调整并补充未翻译的简体中文字串,将中文语言移到程序内,删除其它多语言模块 预设选项:跳过UAC、关闭获取收集隐私数据和优惠信息、不启用智能清理功能等 取消原版内置规则默认勾选Edge/谷歌/火狐等浏览器Cookies项的钩子避免误清理 集成扫描规则:最新WinApp2规则 + 昔之光规则 (飞扬时空、slzyk | 孤雨 、lrxy) ⬇️ 下载地址 下载后请先检查文件完整性,如有问题请在评论区反馈
-
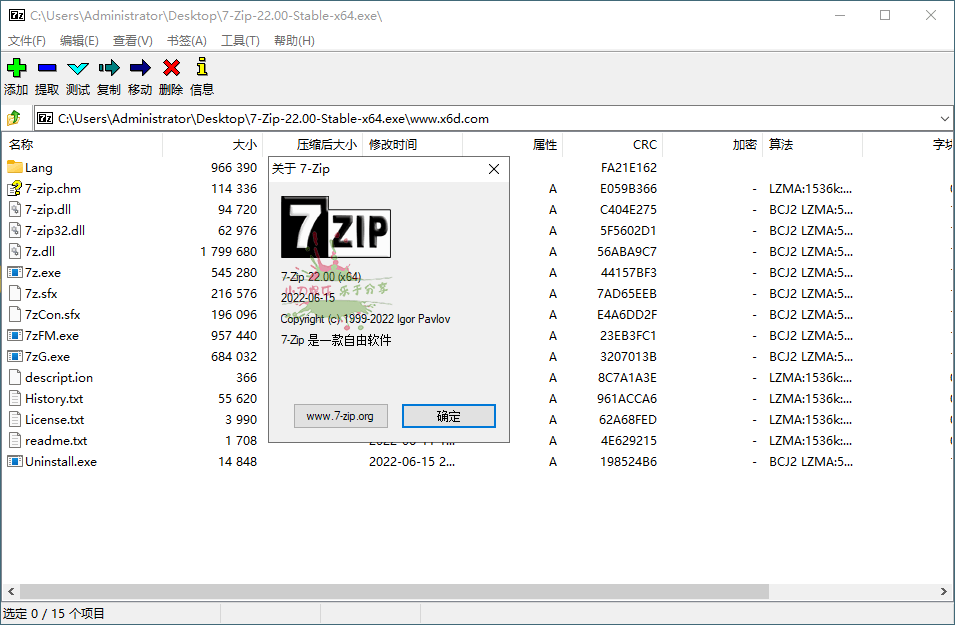
老牌压缩软件7-Zip v26.03修订版 软件介绍 7-Zip – 流行的免费开源压缩软件。7-Zip是一款老牌拥有极高压缩算法的免费开源压缩文件管理器,提供命令行接口和图形界面操作,支持独立的7z格式及近乎所有压缩格式,包括ZIP, RAR, ISO, CAB, GZIP, BZIP2, TAR等。其多线程LZMA压缩比要比普通ZIP文件高达30-50%,它可以把ZIP格式的文件再压缩2-10%。 软件老牌压缩软件7-Zip v26.03修订版 图片2 更新日志 7-zip.org/history.txt 2026.09.03 v26.03 优化Joliet格式ISO镜像及复合压缩包的支持 修复解压恶意构造的压缩包时,源文件网络标记丢失问题 修复多处已知bug及安全漏洞 版本特点 完整汉化所有文件 7zSFX模板 7z.sfx 更新翻译 zh- cn.txt 帮助文档7- zip.chm 自述文档readme.txt 更新日志History.txt 文件描述 descript.ion 卸载程序Uninstall.exe 修改7z.dll的默认7z, zip格式关联图标为WinRar经典主题 优化7- zip压缩文件管理器默认设置包括设置最高压缩比参数 默认仅关联7z, zip文件类型、默认创建压缩文件时最高压缩比 取消折叠右键菜单、右键菜单显示图标、简化右键菜单显示项 无人值守静默安装参数:/ai /gm2(默认C盘程序目录) 静默安装到指定位置:/ai /gm2 /InstallPath="自定义路径" 示例:安装包.exe /ai /gm2 /InstallPath="D:\MyProgram" 最高压缩比参数设置 压缩等级>极限,算法>LZMA2, 字典>128MB, 单词大小->273 固实块大小->固实, CPU线程->2或3, 最下面的参数框->f=BCJ2 ⬇️ 下载地址 下载后请先检查文件完整性,如有问题请在评论区反馈
-
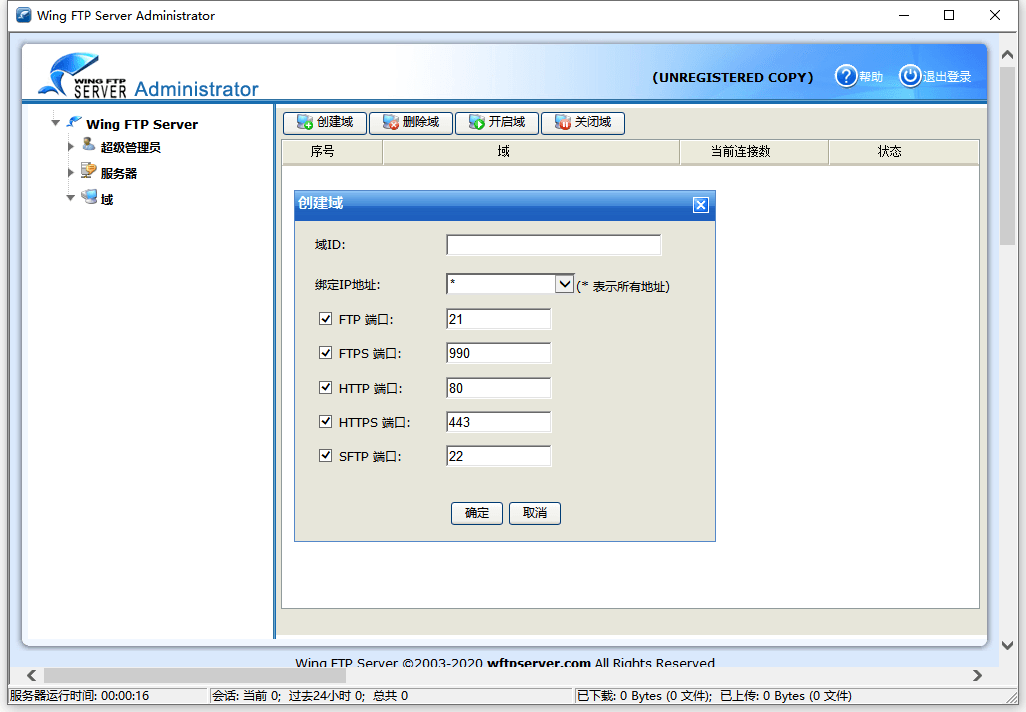
Wing FTP Server (FTP服务器)v8.2.4企业版 软件介绍 Wing FTP Server是一款专业的跨平台FTP服务器软件, 支持可伸缩的处理器架构并采用异步IO处理, 所以在速度和效率方面领先于其他同类产品. 当然他还非常稳定可靠, 在高负载的情况下也能持续地正常运行, 非常适合企业的文件传输. 除了基本功能外, 他还提供一个基于Web的管理端和客户端, 何时何地都能管理你的服务器. 它还支持可编程的事件, 计划任务, Lua脚本扩展, 虚拟文件夹, 上传下载比率分配, 磁盘容量分配, ODBC/Mysql存储账户, 多国语言等特性。 软件Wing FTP Server (FTP服务器)v8.2.4 图片2 新版变化 Wing FTP Server History https://www.wftpserver.com/serverhistory.htm Wing FTP Server各个版本的比较 https://www.wftpserver.com/zh/wftpserver.htm 2026.09.04 v8.2.4 修复升级后连接部分ODBC数据库崩溃的bug 修复Filezilla用SFTP协议打开含上万文件目录失败问题 修复审计报表界面添加「大小」筛选后结果为空的问题 活动界面按ID列排序,改为按数字大小排列 优化SFTP客户端访问海量文件目录的速度 在线演示服务器,快速了解web管理端和web客户端 Web管理端: http://demo.wftpserver.com:5466/ 用户名和密码: demo-admin Web客户端: http://demo.wftpserver.com/ 用户名和密码: demo FTP客户端: demo.wftpserver.com 用户名和密码: demo FTP端口: 21 FTPS端口: 990 SFTP端口: 2222 ⬇️ 下载地址 下载后请先检查文件完整性,如有问题请在评论区反馈
-
白帽黑客工具箱:routersploit 篇 推荐一个实用的开源工具——**routersploit**。项目由threat9开发维护,GitHub上获得了 **13240** 个Star。简单来说,它是一款嵌入式设备的利用框架,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 # Community Join community on [Embedded Exploitation Discord](https://discord.gg/UCXARN2vBx). # Description The RouterSploit Framework is an open-source exploitation framework dedicated to embedded devices.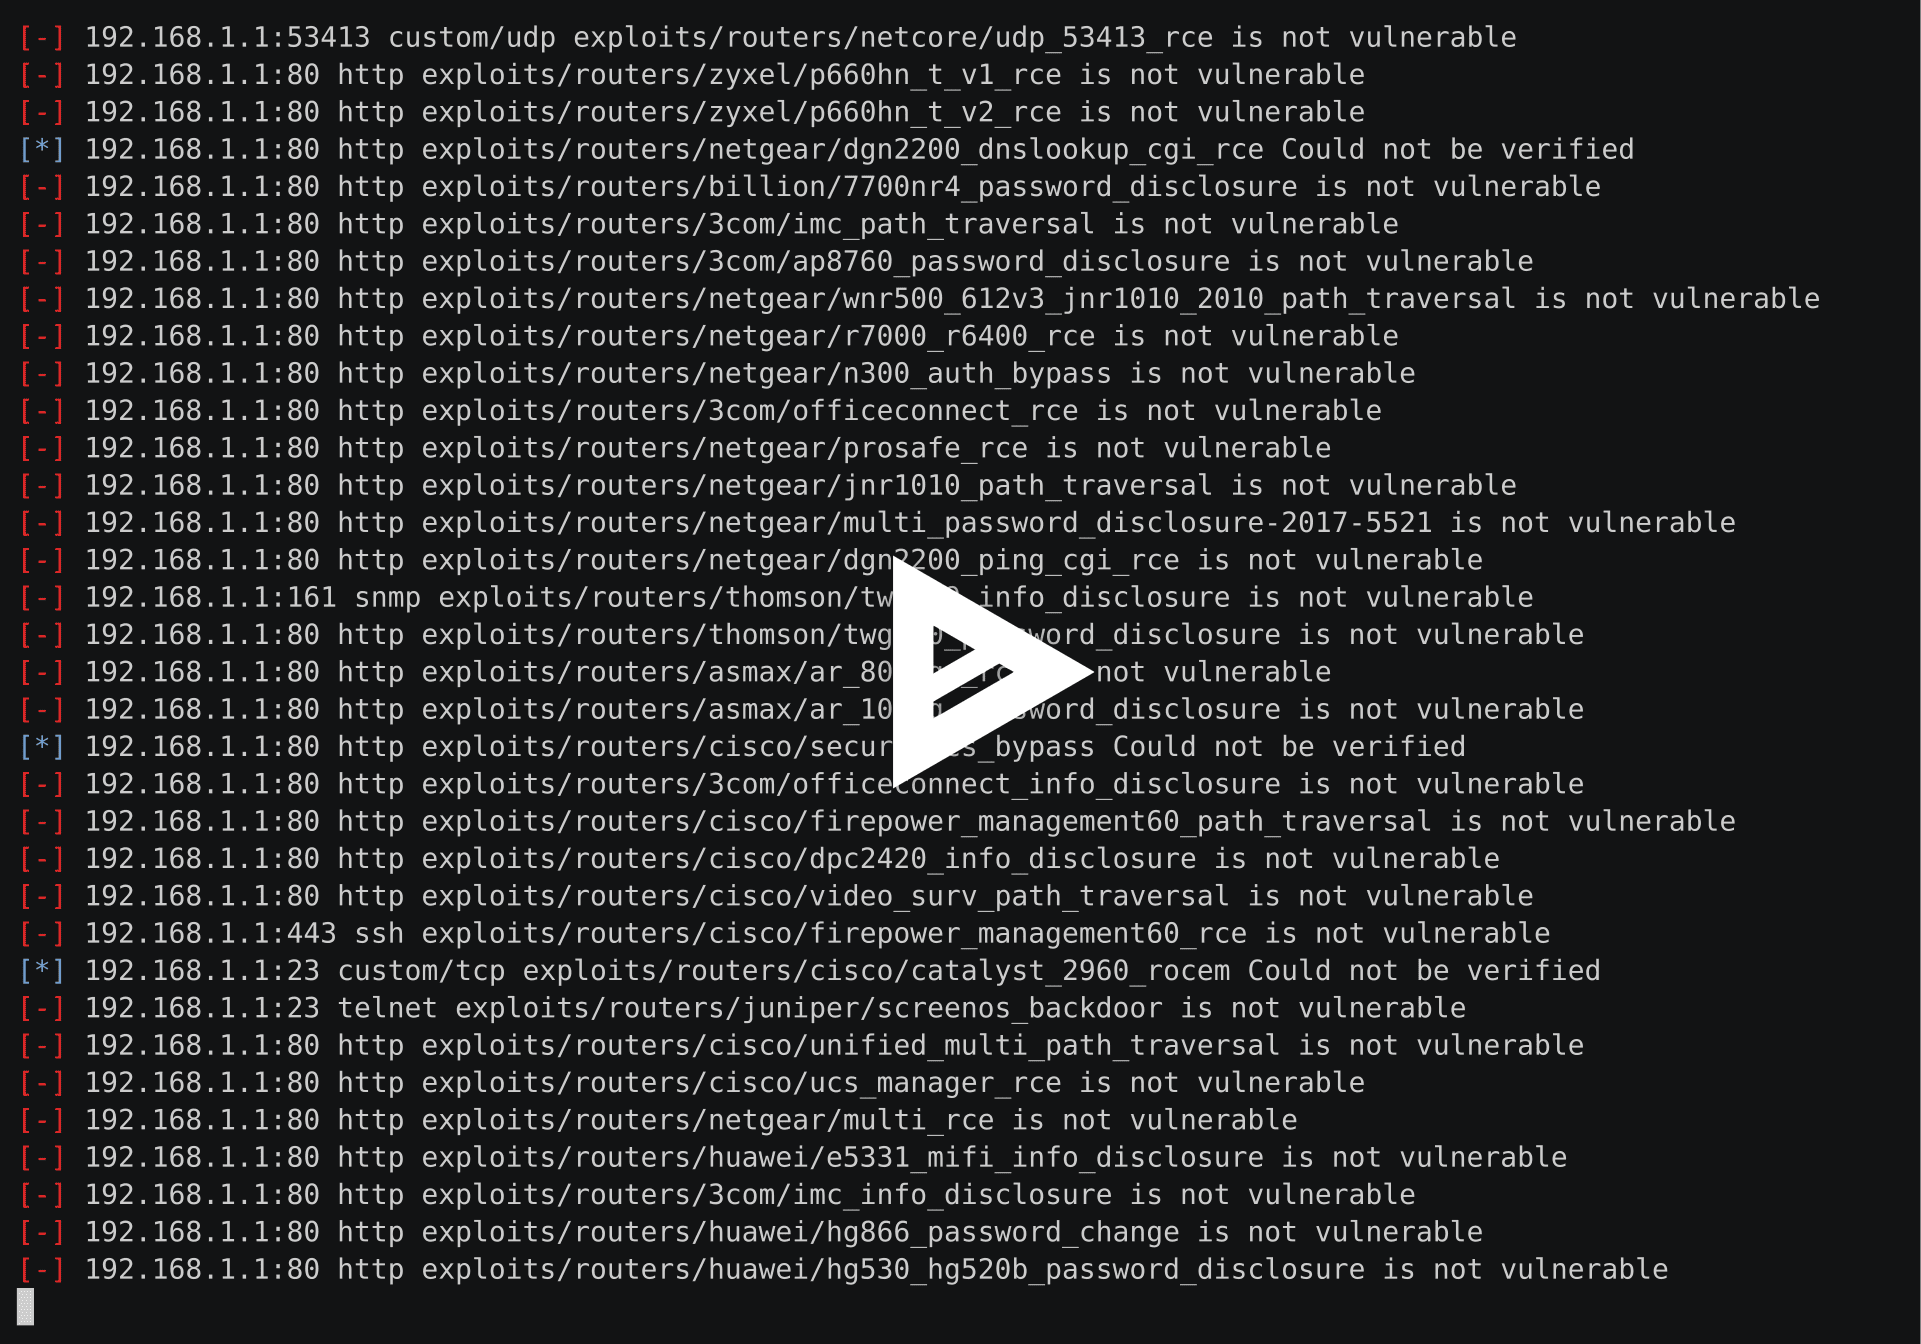It consists of various modules that aid penetration testing operations:* exploits - modules that take advantage of identified vulnerabilities * creds - modules designed to test credentials against network services * scanners - modules that check if a target is vulnerable to any exploit * payloads - modules that are responsible for generating payloads for various architectures and injection points * generic - modules that perform generic attacks# Installation ## Requirements Required: * requests * paramiko * pysnmp * pycryptoOptional: * bluepy - Bluetooth low energy## Installation on Kali Linux apt-get install python3-pip git clone https://www.github.com/threat9/routersploit cd routersploit python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on Ubuntu 20.04 sudo apt-get install git python3-pip git clone https://github.com/threat9/routersploit cd routersploit python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: sudo apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on Ubuntu 18.04 & 17.10 sudo add-apt-repository universe sudo apt-get install git python3-pip git clone https://www.github.com/threat9/routersploit cd routersploit python3 -m pip install setuptools python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on OSX git clone https://www.github.com/threat9/routersploit cd routersploit sudo python3 -m pip install -r requirements.txt python3 rsf.py ## Running on Docker git clone https://www.github.com/threat9/routersploit cd routersploit docker compose up --build -d docker attach routersploit # ## To run again without rebuild docker start routersploit docker attach routersploit # Update Update RouterSploit Framework often. The project is under heavy development and new modules are shipped almost every day. cd routersploit git pull # Build your own To our surprise, people started to fork [routersploit](https://github.com/threat9/routersploit) not because they were interested in the security of embedded devices but simply because they want to leverage our interactive shell logic and build their tools using similar concept. All these years they must have said: _"There must be a better way!"_ and they were completely right, the better way is called [_Riposte_](https://github.com/fwkz/riposte).[_Riposte_](https://github.com/fwkz/riposte) allows you to easily wrap your application inside a tailored interactive shell. Common chores regarding building REPLs was factored out and being taken care of so you can focus on specific domain logic of your application.# License The RouterSploit Framework is under a BSD license. Please see [LICENSE](LICENSE) for more details. # Acknowledgments * [riposte](https://github.com/fwkz/riposte) {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/threat9/routersploit](https://github.com/threat9/routersploit) ⭐ Star数:13240 ? 开发语言:Python ? 项目描述:嵌入式设备的利用框架 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/threat9/routersploit/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/threat9/routersploit"}总的来说,**routersploit**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
Wireshark 是什么?好用的工具软件推荐 推荐一个实用的开源工具——Wireshark。项目由Wireshark开发维护,采用未知开源协议发布。简单来说,它是一个,对于站长和开发者来说是个不错的工具。 工具功能介绍 介绍 {以下是码云平台说明,您可以替换此简介 码云是 OSCHINA 推出的基于 Git 的代码托管平台(同时支持 SVN)。专为开发者提供稳定、高效、安全的云端软件开发协作平台 无论是个人、团队、或是企业,都能够用码云实现代码托管、项目管理、协作开发。企业项目请看 https://gitee.com/enterprises} 软件架构 软件架构说明 安装教程 xxxx xxxx xxxx 使用说明 xxxx xxxx xxxx 参与贡献 Fork 本仓库 新建 Feat_xxx 分支 提交代码 新建 Pull Request 码云特技 使用 Readme\_XXX.md 来支持不同的语言,例如 Readme\_en.md, Readme\_zh.md 码云官方博客 blog.gitee.com 你可以 https://gitee.com/explore 这个地址来了解码云上的优秀开源项目 GVP 全称是码云最有价值开源项目,是码云综合评定出的优秀开源项目 码云官方提供的使用手册 https://gitee.com/help 码云封面人物是一档用来展示码云会员风采的栏目 https://gitee.com/gitee-stars/ 总的来说,Wireshark是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一个的解决方案,不妨下载试试。使用前建议仔细阅读项目文档。 {card-default label="? 工具信息" /} ? 工具名称:Wireshark ? 开发作者:Wireshark ? 工具描述: ? 开发语言:Java ? 开源协议:未知开源协议 ⭐ Star数:0 | ? Fork数:0 ? 更新时间:2020年12月19日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/Wireshark/Wireshark/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/Wireshark/Wireshark.git"}
-
免费开源开源工具推荐:setool-master 下载 今天给大家分享一款实用的开源工具——setool-master。这个工具在Gitee上获得了3个Star,主要功能是SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品,对于需要提高工作效率的朋友来说是个不错的选择。 工具功能介绍 SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品 你看过电影里面的黑客么,手指在键盘上不停的在打字,屏幕上运行的数不清的计算机命令, 没过一会儿,便可以入侵、盗取别人的计算机密码、 没错,Setool Master就是这样一款黑客工具,设计用于红队的社会工程学攻击。比起传统 的漏洞利用,社会工程学攻击会更加的高效和安全,而且对于使用者的门槛会非常低,入门 linux的也能快速掌握。使用python3开发,有更加良好的发展属性和可读性、运行效率 非常的高,设计用于对组织级别的攻击 绝对不要使用Setool Master去攻击一个你不认识的人,或者你可能会遇到许麻烦 你不能将这些源代码用于商业用途 本开源项目内包含第三方工具,在这里说说明:ngrok,seeker-master 本开源项目允许引用,但受到Apache2开源条约限制 作者:LinWinCloud 版本维护 安卓源代码版本 持续维护 v Linux安装包版本 部分维护 v 安卓编译版本 不再维护 X linux编译版本 不再维护 X 源代码 持续维护 V 安装教程 $ git clone https://github.com/LinWin-Cloud/setool-master $ cd setool-master $ pip3 install whois $ pip3 install requests 1.源代码版本、安卓源代码版本 $ cd resources_code_vistion (这个是源代码版本) 或者 cd Android_Resources_code $ python3 setool.py 2.Linux安装包版本 $ 7z x Setool-Master.7z $ cd Setool-Master $ cd Setool-Master $ python3 install_linux.py 软件将安装在/var/Setool-Master,环境请自行配置 3.编译版本、安卓编译版本 $ cd build_vistion(这个是编译版本) 或者 cd Termax_Android_vistion (这个是安卓编译版本) $ chmod +x ./setool $ bash ./setool 使用文档 使用文档(英文版本) 使用文档(中文版本) 注意 本工具集内Web Console密码linwin用户名linwin 更新日志 v1.0.0 2022.1.5 发布Setool Linux轻量个人版本 v2.1.1 2022.3.5 发布Setool Master源代码版本 v2.1.2 2022.3.5 发布Setool Master安装包版本 v2.1.3 2022.3.15 发布Setool Master预编译版本 v2.1.4 2022.4.1 更新配置文件、告示 v2.2.1 2022.5.1 修改部分源代码 v2.3.2 2022.5.4 修改配置文件 v2.4.1 2022.5.7 修改配置文件,更新版本信息 v2.4.2 2022.5.8 修改配置文件和源代码 v2.5.1 2022.5.15 发布安卓Termux编译版本 v2.5.2 2022.5.17 更新安卓Termux编译版本 v2.5.3 2022.5.19 更新部分源代码 v2.5.4 2022.5.28 发布安卓Termux源代码版本 v2.5.5 2022.5.29 更新版本信息、更新源代码 v2.5.6 2022.5.30 修复部分代码错误、更新部分配置文件 v2.5.7 2022.5.31 更新 Setool Master编译版本 版本信息、配置文件 v2.5.8 2022.6.2 更新配置、版本信息 v2.5.9 2022.6.6 更新源代码版本代码 v2.6.0 2022.6.7 创建使用文档文档 v2.6.1 2022.6.10 更新 使用文档(英文版本) v2.6.2 2022.6.11 更新版本信息、配置信息 v2.6.2 2022.6.12 更新配置文件 v2.6.3 2022.6.13 更新 安卓源代码版本 源代码 v2.6.4 2022.6.15 更新使用文档、配置文件 v2.6.5 2022.6.16 更新配置文件 v2.6.6 2022.6.20 更新源代码 v2.6.7 2022.6.21 更新英语文档,创建中文文档 v2.6.8 2022.6.22 更新配置文件 v2.6.9 2022.6.24 更新安卓源代码,更新配置文件 v2.7.0 2022.6.26 修复源代码错误,修复帮助和配置 v2.7.1 2022.6.28 更新版本信息、更新配置文件 v2.7.2 2022.6.30 更新配置文件 v2.7.3 2022.7.3 更新配置文件,修复源码错误 v2.7.4 2022.7.5 更新项目为Setool Master LTS长期支持版本 v2.7.5 2022.7.6 更新源代码、修复IO操作漏洞 v2.7.6 2022.7.13 更新配置文件 v2.7.7 2022.7.22 更新配置文件,说明 v2.7.8 2022.7.23 更新中文帮助、更新配置文件 v2.7.9 2022.8.9 更新配置文件 v2.8.0 2022.8.31 更新配置文件、修复错误 v2.8.1 2022.9.12 修改文档 v2.8.2 2022.9.16 删除了Linux编译版本,不再维护此版本、修改了源代码、修改了说明文件 v2.8.3 2022.10.15 删除了部分无用文件、更新文档 About Setool Master is a open resources social enginnering tools for linux.android(termux). It is free.You do not pay some money for these tools. Setool Master use Python Code language.It is very easy and funny.You can use these resources code to make a new tools and so on.If you want to get Setool-Master,you can goto https://github.com/LinWin-Cloud/setool-master. https://gitee.com/LinWin-CLoud/setool-master Setool Master是一个适用于Linux、Android(termux)的开源的社会工程学 工具。它是免费的。你不需要为这些工具支付费用。Setool Master使用Python 编程语言。非常简单并且有趣,你能用这些源代码去创造一个新的工具等等。如果你 想获取SetoolMaster,你能够访问 https://github.com/LinWin-Cloud/setool-master. https://gitee.com/LinWin-CLoud/setool-master 该项目会持续维护,吸收大家的建议 项目维护真的不容易,开源项目不赚钱,本项目将保证永远也不进行商业收费 真心希望屏幕前面的你能够给开发者一些动力来维护更新这更好的项目 综合来看,setool-master在同类工具中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。 {card-default label="? 工具信息" /} ? 工具名称:setool-master ? 开发作者:LinWin-Cloud ? 工具描述:SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品 ? 开发语言:Python ? 开源协议:未知开源协议 ⭐ Star数:3 | ? Fork数:0 ? 更新时间:2025年06月18日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/LinWin-Cloud/setool-master/repository/archive/main.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/LinWin-Cloud/setool-master.git"}
-
fscan 绿色软件分享 推荐一个实用的开源工具——**fscan**。项目由shadow1ng开发维护,GitHub上获得了 **14514** 个Star。简单来说,它是一款一款内网综合扫描工具方便一键自动化、全方位漏扫扫描。(内网综合扫描工具,实现一键自动化、全方位漏洞扫描),对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 [English](README_EN.md)内网综合扫描工具,一键自动化漏扫。**版本**: 2.2.1 ## 功能特性 ### 扫描能力 - **主机发现** - ICMP/Ping存活探测,支持大网段B/C段存活统计 - **端口扫描** - TCP全连接扫描,内置133个常用端口,支持端口组(web/db/service/all) - **服务识别** - 智能协议识别,支持20+种服务指纹匹配 - **Web探测** - 网站标题、CMS指纹、Web中间件、WAF/CDN识别(40+指纹)### 爆破能力 - **弱密码爆破** - 28种服务爆破(SSH/RDP/SMB/FTP/MySQL/MSSQL/Oracle/Redis等) - **Hash碰撞** - 支持NTLM Hash认证(SMB/WMI) - **SSH密钥登录** - 支持私钥认证方式 - **智能字典** - 内置100+常见弱密码,支持{user /}变量替换### 漏洞检测 - **高危漏洞** - MS17-010(永恒之蓝)、SMBGhost(CVE-2020-0796) - **未授权访问** - Redis/MongoDB/Memcached/Elasticsearch等未授权检测 - **POC扫描** - 集成Web漏洞POC,支持Xray POC格式 - **DNSLog** - 支持DNSLog外带检测### 漏洞利用 - **Redis利用** - 写公钥、写计划任务、写WebShell、主从复制RCE - **MS17-010利用** - ShellCode注入,支持添加用户、执行命令 - **SSH命令执行** - 认证成功后自动执行命令### 本地模块 - **信息收集** - 系统信息、环境变量、域控信息、网卡配置 - **凭据获取** - 内存转储(MiniDump)、键盘记录、注册表导出 - **权限维持** - Systemd服务、Windows服务、计划任务、启动项、LD_PRELOAD - **反弹Shell** - 正向Shell、反向Shell、SOCKS5代理服务 - **杀软检测** - 识别目标主机安装的安全软件 - **痕迹清理** - 日志清理工具### 输入输出 - **目标输入** - IP/CIDR/域名/URL,支持文件批量导入 - **排除规则** - 支持排除特定主机、端口 - **输出格式** - TXT/JSON/CSV多格式输出 - **静默模式** - 无Banner、无进度条、无颜色输出### 网络控制 - **代理支持** - HTTP/SOCKS5代理,支持指定网卡 - **发包控制** - 速率限制、最大发包数量控制 - **超时控制** - 端口超时、Web超时、全局超时独立配置 - **并发控制** - 端口扫描线程、服务扫描线程独立配置### 扩展功能 - **SDK嵌入** - `pkg/fscan`提供Go SDK,可嵌入Agent或安全平台,支持任务控制(Pause/Resume)、实时进度回调、TaskID追溯 - **Web管理界面** - 可视化扫描任务管理(条件编译 -tags web) - **Lab靶场环境** - 内置Docker靶场用于测试学习 - **插件化架构** - 服务插件/Web插件/本地插件分离,易于扩展 - **多语言支持** - 中英文界面切换(-lang zh/en) - **性能统计** - JSON格式性能报告(-perf)## v2.1.0 更新日志> 本次更新包含 **262个提交**,涵盖30项新功能、120项修复、54项重构、14项性能优化、20项测试增强。 ### 架构重构 - **全局变量消除** - 迁移至Config/State对象,提升并发安全和可测试性 - **SMB插件融合** - 整合smb/smb2/smbghost/smbinfo为统一插件,新增smb_protocol.go - **服务探测重构** - 实现Nmap风格fallback机制,优化端口指纹识别策略 - **输出系统重构** - TXT实时刷盘+双写机制,解决结果丢失和乱序问题 - **i18n框架升级** - 迁移至go-i18n,完整覆盖core/plugins/webscan模块 - **HostInfo重构** - Ports字段从string改为int,类型安全 - **函数复杂度优化** - clusterpoc(125→30)、EnhancedPortScan(111→20) - **代码审计** - 修复P0-P2级别问题,清理deadcode - **日志系统优化** - LogDebug调用清理(71→18),精简启动日志输出### 性能优化 - **正则预编译** - 全局正则表达式预编译,避免重复编译开销 - **内存优化** - map[string]bool改为map[string]struct{}节省内存 - **并发指纹匹配** - 多协程并行匹配,提升识别速度 - **连接复用** - SOCKS5全局拨号器复用,避免重复握手 - **滑动窗口调度** - 自适应线程池+流式迭代器,优化端口扫描 - **CEL缓存优化** - POC扫描CEL环境缓存,减少重复初始化 - **包级变量提取** - proxyFailurePatterns/resourceExhaustedPatterns/sslSecondProbes等 - **预分配容量** - 简化转换链、单次字符串替换 - **并发安全优化** - 优化锁粒度和内存分配### 新功能 - **Web管理界面** - 可视化扫描任务管理,响应式布局和进度显示 - **多格式POC适配** - 支持xray和afrog格式POC - **智能扫描模式** - 布隆过滤器去重+代理优化 - **增强指纹库** - 集成FingerprintHub(3139条指纹) - **Favicon指纹识别** - 支持mmh3和MD5双格式hash匹配 - **通用版本提取器** - 自动提取服务版本信息 - **指纹优先级排序** - 智能排序匹配结果 - **智能协议检测** - 自动识别HTTP/HTTPS协议类型 - **网卡指定功能** - 支持VPN场景(-iface参数) - **排除主机文件** - 支持从文件读取排除主机(-ehf参数) - **ICMP令牌桶限速** - 防止高速扫描导致路由器崩溃 - **端口扫描重试** - 失败自动重扫机制 - **RDP真实认证** - 集成grdp库实现系统指纹识别 - **SMB/FTP文件列表** - 匿名访问时自动列出文件 - **302跳转双重识别** - 同时识别原始响应和跳转后响应指纹 - **TXT输出URL汇总** - 末尾添加Web服务URL列表便于批量测试 - **nmap核心集成** - 三大改进:探测策略/匹配引擎/版本解析 - **插件选择性编译** - Build Tags系统,支持服务/本地/Web插件独立编译 - **默认端口扩展** - 从62个扩展到133个常用端口 - **全端口扫描支持** - 扩大端口范围限制 - **HTTP重定向控制** - 可配置的重定向次数限制 - **性能分析支持** - 添加pprof性能分析和benchmark测试 - **TCP包统计** - 服务插件支持TCP包发送统计 - **fscan-lab靶场** - 内网渗透训练平台,覆盖全部漏洞场景(未完成) - **Redis利用增强** - 移植完整Redis利用功能(写公钥/计划任务/WebShell/主从RCE) - **rsync插件重构** - 使用go-rsync库重构认证逻辑### Bug修复(120项,列出关键修复) - **RDP空指针panic** - 修复证书解析导致的崩溃(#551) - **批量扫描漏报** - 修复大规模扫描遗漏问题(#304) - **JSON输出格式** - 修复输出格式错误(#446) - **Redis弱密码检测** - 修复检测遗漏问题(#447) - **结果实时保存** - 修复扫描结果未及时保存(#469) - **Nmap解析溢出** - 修复八进制转义解析bug(#478) - **指纹识别竞态** - 修复webtitle/webpoc竞态问题(#474) - **MySQL连接验证** - 改用information_schema库验证 - **代理端口误判** - 修复代理模式下端口状态判断错误 - **Context超时** - 修复22处插件超时未响应问题 - **ICMP竞态条件** - 修复并发扫描竞争问题 - **IPv6地址格式** - 修复4处地址格式化问题 - **POC高并发卡死** - 修复Context未传播问题 - **Ctrl+C结果丢失** - 添加信号处理确保结果写入 - **SOCKS5全回显** - 添加代理连接验证 - **服务探测泄漏** - 修复连接未正确关闭问题 - **webtitle响应丢弃** - 修复部分响应数据被丢弃导致识别失败 - **TXT漏洞信息缺失** - 修复输出遗漏漏洞详情 - **JSON指纹缺失** - 统一SERVICE结果Target格式 - **扫描耗时显示** - 修复完成耗时显示为0的问题 - **虚假漏洞记录** - 重构TXT输出系统消除误报 - **Redis跨平台路径** - 修复利用功能的路径和超时问题 - **Windows编译警告** - 修复fscan-lite平台兼容性 - **Go 1.20兼容** - 降级依赖保持兼容性### 测试增强(20项) - **单元测试** - 核心模块覆盖率74-100% - **并发安全测试** - State对象、指纹匹配引擎专项测试 - **集成测试** - Web扫描/端口扫描/服务探测/SSH认证/ICMP探测 - **CLI参数测试** - 命令行参数解析验证 - **性能基准测试** - AdaptivePool、服务探测策略benchmark - **ResultBuffer测试** - 去重和完整度评分验证### 工程化改进 - **CI流程优化** - golangci-lint v2升级,简化构建步骤 - **Issue自动化** - GitHub Issue模板优化,Project自动化工作流 - **Lint全量修复** - revive/errcheck/shadow/staticcheck/gosimple全部通过 - **README重写** - 中英文文档全面更新 - **代码格式统一** - gofmt/goimports规范化## 快速开始 bash # 扫描C段 ./fscan -h 192.168.1.1/24 # 指定端口 ./fscan -h 192.168.1.1 -p 22,80,443,3389 # 仅存活探测 ./fscan -h 192.168.1.1/24 -ao # 禁用爆破 ./fscan -h 192.168.1.1/24 -nobr # Web扫描 ./fscan -u http://192.168.1.1 # 本地插件 ./fscan -local systeminfo # Hash碰撞 ./fscan -h 192.168.1.1 -m smb2 -user admin -hash xxxxx # Redis写公钥 ./fscan -h 192.168.1.1 -m redis -rf id_rsa.pub ## 编译 bash # 标准编译 go build -ldflags="-s -w" -trimpath -o fscan . # 带Web管理界面 go build -tags web -ldflags="-s -w" -trimpath -o fscan-web . ## 安装 bash # Arch Linux yay -S fscan-git ## 运行`fscan.exe -h 192.168.x.x` !!`fscan.exe -h 192.168.x.x -rf id_rsa.pub` (Redis写公钥) !`fscan.exe -h 192.168.x.x -m ssh -user root -pwd password` !`fscan.exe -h 192.168.x.x -m ssh -user root -pwda pass1 pass2 pass3` (追加多个密码)`fscan.exe -h 192.168.x.x -p80 -proxy http://127.0.0.1:8080` !`fscan.exe -h 192.168.x.x -socks5 socks5://user:pass@127.0.0.1:1080` (SOCKS5认证代理)`fscan.exe -h 192.168.x.x -p 139 -m netbios` !!`fscan.exe -h 192.0.0.0/8 -m icmp` .png](/live.png)## 路线图 ### 更新计划 - **更新周期** - 每月一次版本发布 - **前两周** - 新功能开发与特性更新 - **后两周** - Bug修复与代码整合 - **欢迎PR** - 期待您的贡献!### SDK & Agent 集成 - 扩展SDK能力,完善端侧Agent嵌入支持 - 断点续扫、带宽级限速、内存水位控制 - 更多Agent场景的集成示例### 插件生态 - 持续扩展服务插件覆盖范围 - 为每个服务插件开发更多漏洞检测和利用能力 - 保持插件API向后兼容,确保旧版本POC持续可用### Fscan-lite - C语言重写的轻量版本 - 更小的体积,更少的依赖 - 支持更多嵌入式/受限环境 - 目录: [fscan-lite](./fscan-lite)### Fscan-lab - 内网渗透测试靶场环境 - 覆盖所有fscan支持的漏洞场景 - 开发测试与功能验证平台 - 新手学习与技能练习环境 - 目录: [fscan-lab](./fscan-lab)##
-
vibe-pentest 是什么?好用的工具软件推荐 今天给大家分享一款实用的开源工具——vibe-pentest。这个工具在Gitee上获得了22个Star,主要功能是Vibe Pentest 是一款基于 AI Agent 架构的自动化渗透测试工具,采用多 Agent 并行执行架构,能够对 Web 应用、API、管理后台等进行全面的黑盒渗透测试(包括业务逻辑漏洞评估),输出稳定可靠的安全报告,提供可落地整改建议。,对于需要提高工作效率的朋友来说是个不错的选择。 工具功能介绍 中文 | English Vibe Pentest 当前版本:v1.0.30Vibe Pentest(AI 渗透测试)是一款基于 AI Agent 架构的自动化渗透测试工具,采用多 Agent 并行执行架构,能够对 Web 应用、API、管理后台等进行全面的黑盒渗透测试(包括业务逻辑漏洞评估),输出稳定可靠的安全报告,并提供可落地的整改建议。 最适合安全服务公司与个人白帽子的 AI 渗透测试工具。内置白帽子职业操守约束,全程遵循最小影响原则:获得有效证据后即停止不必要的重复利用、扩散操作。具备创新独特的“低影响高回报渗透模式”、深入挖掘漏洞的“标准模式”。目录 流程示意图 提示词示例(强烈推荐使用) [三分钟教学vibe-pentest 是什么?好用的工具软件推荐 图片1 三步骤快速安装 环境运行依赖 工作目录与报告输出 HTTP 代理配置(可选) 自定义 POC 与指纹规则(可选) [
-
白帽黑客工具箱:xmrig 篇 推荐一个实用的开源工具——xmrig。项目由xmrig开发维护,GitHub上获得了 10114 个Star。简单来说,它是一款RandomX、KawPow、CryptoNight和GhostRider统一CPU/GPU矿机和RandomX基准测试,对于站长和开发者来说是个不错的工具。 工具功能介绍 XMRig is a high performance, open source, cross platform RandomX, KawPow, CryptoNight and GhostRider unified CPU/GPU miner and RandomX benchmark. Official binaries are available for Windows, Linux, macOS and FreeBSD. Mining backends CPU (x86/x64/ARMv7/ARMv8/RISC-V) OpenCL for AMD GPUs. CUDA for NVIDIA GPUs via external CUDA plugin. Download Binary releases Build from source Usage The preferred way to configure the miner is the JSON config file as it is more flexible and human friendly. The command line interface does not cover all features, such as mining profiles for different algorithms. Important options can be changed during runtime without miner restart by editing the config file or executing API calls.* Wizard helps you create initial configuration for the miner. Workers helps manage your miners via HTTP API. Donations Default donation 1% (1 minute in 100 minutes) can be increased via option donate-level or disabled in source code. XMR: 48edfHu7V9Z84YzzMa6fUueoELZ9ZRXq9VetWzYGzKt52XU5xvqgzYnDK9URnRoJMk1j8nLwEVsaSWJ4fhdUyZijBGUicoD Developers xmrig sech1 Contacts support@xmrig.com reddit twitter {card-default label="? 工具信息" /} ? 项目地址:https://github.com/xmrig/xmrig ⭐ Star数:10114 ? 开发语言:C ? 项目描述:RandomX、KawPow、CryptoNight和GhostRider统一CPU/GPU矿机和RandomX基准测试 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/xmrig/xmrig/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/xmrig/xmrig"} 总的来说,xmrig是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
strix - 一款实用的开源工具 推荐一个实用的开源工具——**strix**。项目由usestrix开发维护,GitHub上获得了 **61007** 个Star。简单来说,它是一款开源人工智能渗透测试工具,用于查找和修复应用程序的漏洞。,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 ### The open-source AI pentesting tool. Autonomous AI hackers that find and fix your app’s vulnerabilities. > [!TIP] > **New!** Strix integrates seamlessly with GitHub Actions and CI/CD pipelines. Automatically scan for vulnerabilities on every pull request and block insecure code before it reaches production - [Get started with no setup required](https://app.strix.ai?utm_source=github&utm_medium=readme&utm_content=tip_ci).---## Strix OverviewStrix are autonomous AI penetration testing agents that act just like real hackers - they run your code dynamically, find vulnerabilities, and validate them through actual proofs-of-concept. Built for developers and security teams who need fast, accurate security testing without the overhead of manual pentesting or the false positives of static analysis tools.**Key Capabilities:**- **Full pentesting toolkit** - reconnaissance, exploitation, and validation out of the box - **Multi-agent orchestration** - teams of AI pentesters that collaborate and scale - **Real exploit validation** - working PoCs, not false positives like legacy vulnerability scanners - **Developer‑first CLI** - actionable findings with remediation guidance - **Auto‑fix & reporting** - generate patches and compliance-ready pentest reports# # Use Cases- **Application Security Testing** - Detect and validate critical vulnerabilities in your applications - **Rapid Penetration Testing** - Get penetration tests done in hours, not weeks, with compliance reports - **Bug Bounty Automation** - Automate bug bounty research and generate PoCs for faster reporting - **CI/CD Integration** - Run tests in CI/CD to block vulnerabilities before reaching production## ? Quick Start**Prerequisites:** - Docker (running) - An LLM API key from any [supported provider](https://docs.strix.ai/llm-providers/overview) (OpenAI, Anthro, Google, etc.)### Installation & First Scan bash # Install Strix curl -sSL https://strix.ai/install | bash # Configure your AI provider export STRIX_LLM="openrouter/z-ai/glm-5.3" export LLM_API_KEY="your-api-key" # Run your first security assessment strix --target ./app-directory > [!NOTE] > First run automatically pulls the sandbox Docker . Results are saved to `strix_runs/`---## Ways to Run Strix- **Open Source** - free, runs locally with Docker and your own LLM key. [Quick Start](https://docs.strix.ai/quickstart) - **Strix Cloud** - no setup, validated findings, one-click autofix, and PR reviews. [Run a pentest →](https://app.strix.ai?intent=pentest&utm_source=github&utm_medium=readme&utm_content=table_cloud) - **Enterprise** - SSO, compliance-ready reports, VPC or self-hosted deployment. [Try Strix Enterprise →](https://strix.ai/demo?utm_source=github&utm_medium=readme&utm_content=table_demo)---## ☁️ Strix CloudTry the Strix full-stack penetration testing platform at **[app.strix.ai](https://app.strix.ai?utm_source=github&utm_medium=readme&utm_content=cloud_heading)** - sign up for free, connect your repos and domains, and launch a pentest in minutes.- **Validated findings with PoCs** - every vulnerability includes a working proof-of-concept exploit and reproduction steps - **One-click autofix** - AI-generated security patches as ready-to-merge pull requests - **Continuous pentesting** - always-on vulnerability scanning that keeps pace with your deployments - **DevSecOps integrations** - GitHub, GitLab, Bitbucket, Slack, Jira, Linear, and CI/CD pipelines - **Continuous learning** - AI that builds on past findings, adapts to your codebase, and reduces false positives over time[**Run a pentest →**](https://app.strix.ai?intent=pentest&utm_source=github&utm_medium=readme&utm_content=cloud_cta)## ? EnterpriseGet the same Strix experience with enterprise-grade controls: SSO (SAML/OIDC), custom compliance-ready penetration testing reports (SOC 2, ISO 27001, PCI DSS), dedicated support and SLA, custom deployment options (VPC or self-hosted), BYOK model support, and tailored AI pentesting agents optimized for your environment.[**Try Strix Enterprise →**](https://strix.ai/demo?utm_source=github&utm_medium=readme&utm_content=enterprise_cta)--- ## ? Use Strix from Your Coding AgentStrix is agent-ready. Give Claude Code, Cursor, Codex, or any [SKILL.md-compatible](https://agentskills.io) agent the ability to run pentests, fix findings, and set up CI scanning: bash npx skills add usestrix/strix This installs nine skills for running pentests, fixing findings, and CI scanning, against code, web apps, APIs, and the OWASP Top 10. Agents can use the local CLI or the managed cloud with the same engine.See [`AGENTS.md`](AGENTS.md) for the quick reference, [docs.strix.ai/llms.txt](https://docs.strix.ai/llms.txt) for the CLI, and [docs.app.strix.ai](https://docs.app.strix.ai) for the API.--- ## ✨ Features ### Agentic Pentesting ToolsStrix agents come equipped with a comprehensive offensive security toolkit - the same tools used by professional penetration testers and ethical hackers:- **HTTP Interception Proxy** - Full request/response manipulation and analysis with Caido - **Browser Exploitation** - Automated browser for testing XSS, CSRF, clickjacking, and auth bypass flows - **Shell & Command Execution** - Interactive terminal for exploit development and post-exploitation - **Custom Exploit Runtime** - Python sandbox for writing and validating proof-of-concept exploits - **Reconnaissance & OSINT** - Automated attack surface mapping, subdomain enumeration, and fingerprinting - **Static & Dynamic Code Analysis** - SAST + DAST capabilities for comprehensive application security testing - **Vulnerability Knowledge Base** - Structured findings with CVSS scoring and OWASP classification### Comprehensive Vulnerability ScannerStrix identifies, validates, and exploits a wide range of security vulnerabilities across the OWASP Top 10 and beyond:- **Broken Access Control** - IDOR, privilege escalation, auth bypass - **Injection Attacks** - SQL injection, NoSQL injection, OS command injection, SSTI - **Server-Side Vulnerabilities** - SSRF, XXE, insecure deserialization, RCE - **Client-Side Attacks** - XSS (stored/reflected/DOM), prototype pollution, CSRF - **Business Logic Flaws** - Race conditions, payment manipulation, workflow bypass - **Authentication & Session** - JWT attacks, session fixation, credential stuffing vectors - **Infrastructure & Cloud** - Misconfigurations, exposed services, cloud security issues - **API Security** - Broken authentication, mass assignment, rate limiting bypass### Graph of Agents (Multi-Agent Pentesting)Advanced multi-agent orchestration for comprehensive automated penetration testing:- **Distributed Pentesting** - Specialized AI agents for recon, exploitation, and post-exploitation - **Scalable Security Testing** - Parallel execution across multiple targets for fast, comprehensive coverage - **Dynamic Coordination** - Agents share discoveries, chain vulnerabilities, and collaborate like a red team---## ?️ Local Web ViewerEvery scan writes its results to disk as it runs. Bring them up in a local dashboard with a single command: bash # Open the most recent run strix view # ...or open a specific run by name strix view my-run-name # Expose the viewer on all IPv4 interfaces at a fixed port strix view --host 0.0.0.0 --port 8080 --no-open The dashboard shows the findings, a live map of the agent team, and past runs. Nothing leaves your machine, and the UI ships prebuilt. `strix view` binds to `127.0.0.1` and prints a tokened link that grants access to the run, so share it carefully.See the [viewer documentation](https://docs.strix.ai/usage/viewer) for the options and for reaching the viewer from another machine.--- ## Usage Examples ### Basic Usage bash # Scan a local codebase strix --target ./app-directory # Security review of a GitHub repository strix --target https://github.com/org/repo # Black-box web application assessment strix --target https://your-app.com ### API Testing (OpenAPI / Swagger / Postman)Point Strix at an API contract and it tests every declared endpoint instead of having to discover them by crawling. Pair the spec with the live base URL so the agent knows where to send traffic: bash # OpenAPI / Swagger file, Postman export, or a live collection by id strix --target ./openapi.yaml --target https://api.your-app.com strix --target postman:// --target https://api.your-app.com ### Advanced Testing Scenarios bash # Grey-box authenticated testing strix --target https://your-app.com --instruction "Perform authenticated testing using credentials: user:pass" # Multi-target testing (source code + deployed app) strix -t https://github.com/org/app -t https://your-app.com # Targets from a file, one target per non-empty, non-comment line strix --target-list ./targets.txt See the [CLI reference](https://docs.strix.ai/usage/cli) for every option, including scan modes, diff scope, instruction files, and budgets. ### Headless ModeRun Strix programmatically without interactive UI using the `-n/--non-interactive` flag - perfect for servers and automated jobs. The CLI prints real-time vulnerability findings and the final report before exiting. Exits with non-zero code when vulnerabilities are found. bash strix -n --target https://your-app.com ### CI/CD (GitHub Actions)Strix can be added to your pipeline to run a security test on pull requests with a lightweight GitHub Actions workflow: yaml name: strix-penetration-teston: pull_request:jobs: security-scan: runs-on: ubuntu-latest steps: - uses: actions/checkout@v6 with: fetch-depth: 0- name: Install Strix run: curl -sSL https://strix.ai/install | bash- name: Run Strix env: STRIX_LLM: ${{ secrets.STRIX_LLM }} LLM_API_KEY: ${{ secrets.LLM_API_KEY }}run: strix -n -t ./ --scan-mode quick > [!TIP] > In CI pull request runs, Strix automatically scopes quick reviews to changed files, which is why the > checkout above fetches full history. See the > [CI/CD documentation](https://docs.strix.ai/integrations/github-actions) for the details.### Configuration bash export STRIX_LLM="openrouter/z-ai/glm-5.3" export LLM_API_KEY="your-api-key" # Optional export LLM_API_BASE="your-api-base-url" # if using a local model, e.g. Ollama, LMStudio > [!NOTE] > Strix automatically saves your configuration to `~/.strix/cli-config.json`, so you don't have to re-enter it on every run. > See the [configuration reference](https://docs.strix.ai/advanced/configuration) for every environment variable.#### Sign in with a ChatGPT subscriptionInstead of a metered API key, you can run Strix on your ChatGPT Plus/Pro subscription: bash strix auth login chatgpt # sign in with your ChatGPT account export STRIX_LLM="chatgpt/gpt-5.4" # chatgpt/ runs on the subscription strix auth status # show the active sign-in, or logout to forget it #### Use the managed platform: `strix cloud`Run scans on [app.strix.ai](https://app.strix.ai) from the terminal, without Docker or an LLM key: bash strix cloud login # browser sign-in, one credential per install strix cloud scans start --source . --yes --wait # scan local code, approving the upload strix cloud scans start --engagement-type live_test --domain-ids --wait strix cloud vulns list --severity critical Every [REST API](https://docs.app.strix.ai) operation has a matching `strix cloud ` command. Run `strix cloud` to list the resources, and add `help` to a resource to list its verbs. Output is JSON when stdout is not a terminal or when you pass `--json`. Binary downloads are the exception: redirect the raw bytes, or combine `--output FILE --json` for download metadata.See the [cloud CLI documentation](https://docs.strix.ai/cloud/cli) for scopes, workspaces, billing, and source-upload options. #### Connect your own MCP serversStrix can connect to Model Context Protocol (MCP) servers you list and expose their tools to the agent during a run. Create `~/.strix/mcp-servers.json` with a JSON list of local `stdio` servers or remote `http` servers: json [ { "name": "github", "transport": "http", "url": "https://api.githubcopilot.com/mcp/", "auth": { "kind": "bearer", "token": "your-token" }, "allowed_tools": ["list_issues"] } ] Each server's tools are namespaced by `name`, for example `github_list_issues`. See the [MCP documentation](https://docs.strix.ai/integrations/mcp) for the full schema, tool filtering, and `stdio` servers.**Recommended models for best results:**- [Z.ai GLM-5.3 on OpenRouter](https://openrouter.ai/z-ai/glm-5.3) - `openrouter/z-ai/glm-5.3` (the default k) - [OpenAI GPT-5.4](https://openai.com/api/) - `openai/gpt-5.4` - [AnthroClaude Sonnet 4.6](https://claude.com/platform/api) - `anthro/claude-sonnet-4-6` - [Google Gemini 3 Pro Preview](https://cloud.google.com/vertex-ai) - `vertex_ai/gemini-3-pro-preview` - [DeepSeek V4 Pro](https://platform.deepseek.com) - `deepseek/deepseek-v4-pro` - [Moonshot Kimi K3](https://platform.kimi.ai) - `moonshot/kimi-k3`See the [LLM Providers documentation](https://docs.strix.ai/llm-providers/overview) for all supported providers including Vertex AI, Bedrock, Azure, and local models.## Documentation Full documentation is available at **[docs.strix.ai](https://docs.strix.ai)** - including detailed guides for usage, CI/CD integrations, skills, and advanced configuration. ## Contributing We welcome contributions of code, docs, and new skills - check out our [Contributing Guide](https://docs.strix.ai/contributing) to get started or open a [pull request](https://github.com/usestrix/strix/pulls)/[issue](https://github.com/usestrix/strix/issues). ## Join Our CommunityHave questions? Found a bug? Want to contribute? **[Join our Discord!](https://discord.gg/strix-ai)** ## Support the Project**Love Strix?** Give us a ⭐ on GitHub! ## Acknowledgements Strix builds on the incredible work of open-source projects like [LiteLLM](https://github.com/BerriAI/litellm), [Caido](https://github.com/caido/caido), [Nuclei](https://github.com/projectdiscovery/nuclei), [Playwright](https://github.com/microsoft/playwright), and [Bubble Tea](https://github.com/charmbracelet/bubbletea). Huge thanks to their maintainers!> [!WARNING] > **Authorized use only.** Strix actively tests the targets you point it at, so only run it against systems you own or have **explicit, written permission** to test, and stay within the agreed scope. Unauthorized testing is illegal in most jurisdictions. > You alone are responsible for obtaining authorization and complying with the law. Strix is provided "as is" with no warranty or liability for misuse.{card-default label="? 工具信息" /} ? 项目地址:[https://github.com/usestrix/strix](https://github.com/usestrix/strix) ⭐ Star数:61007 ? 开发语言:Python ? 项目描述:开源人工智能渗透测试工具,用于查找和修复应用程序的漏洞。 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/usestrix/strix/archive/refs/heads/main.zip"} {cloud type="default" title="网盘下载" url="https://github.com/usestrix/strix"}总的来说,**strix**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
开源安全工具 nuclei 推荐 推荐一个实用的开源工具——**nuclei**。项目由projectdiscovery开发维护,GitHub上获得了 **31053** 个Star。简单来说,它是一款Nuclei是一款快速、可定制的漏洞扫描器,由全球安全社区提供支持,构建在一个简单的基于YAML的DSL之上,使协作能够解决互联网上的流行漏洞。它可帮助您查找应用程序、API、网络、DNS和云配置中的漏洞。,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍  **Nuclei is a modern, high-performance vulnerability scanner that leverages simple YAML-based templates. It empowers you to design custom vulnerability detection scenarios that mimic real-world conditions, leading to zero false positives.**- Simple YAML format for creating and customizing vulnerability templates.- Contributed by thousands of security professionals to tackle trending vulnerabilities. - Reduce false positives by simulating real-world steps to verify a vulnerability. - Ultra-fast parallel scan processing and request clustering. - Integrate into CI/CD pipelines for vulnerability detection and regression testing. - Supports multiple protocols like TCP, DNS, HTTP, SSL, WHOIS, JavaScript, Code and more. - Integrate with Jira, Splunk, GitHub, Elastic, GitLab. - [**`Get Started`**](#get-started) - [_`1. Nuclei CLI`_](#1-nuclei-cli) - [_`2. Pro and Enterprise Editions`_](#2-pro-and-enterprise-editions) - [**`Documentation`**](#documentation) - [_`Command Line Flags`_](#command-line-flags) - [_`Single target scan`_](#single-target-scan) - [_`Scanning multiple targets`_](#scanning-multiple-targets) - [_`Network scan`_](#network-scan) - [_`Scanning with your custom template`_](#scanning-with-your-custom-template) - [_`Connect Nuclei to ProjectDiscovery_`_](#connect-nuclei-to-projectdiscovery) - [**`Nuclei Templates, Community and Rewards`**](#nuclei-templates-community-and-rewards-) ? - [**`Our Mission`**](#our-mission) - [**`Contributors`**](#contributors-heart) ❤ - [**`License`**](#license) # # Get Started ### **1. Nuclei CLI**_Install Nuclei on your machine. Get started by following the installation guide [**`here`**](https://docs.projectdiscovery.io/tools/nuclei/install?utm_source=github&utm_medium=web&utm_campaign=nuclei_readme). Additionally, we provide [**`a free cloud tier`**](https://cloud.projectdiscovery.io/sign-up) that comes with generous monthly free limits:_- Store and visualize your vulnerability findings - Write and manage your Nuclei templates - Access the latest Nuclei templates - Discover and store your targets> [!Important] > |**This project is in active development**. Expect breaking changes with releases. Review the release changelog before updating.| > |:--------------------------------| > | This project is primarily built to be used as a standalone CLI tool. **Running nuclei as a service may pose security risks.** It's recommended to use with caution and additional security measures. |### **2. Pro and Enterprise Editions**_For security teams and enterprises, we provide a cloud-hosted service built on top of Nuclei OSS, fine-tuned to help you continuously run vulnerability scans at scale with your team and existing workflows:_- 50x faster scans - Large scale scanning with high accuracy - Integrations with cloud services (AWS, GCP, Azure, Cloudflare, Fastly, Terraform, Kubernetes) - Jira, Slack, Linear, APIs and Webhooks - Executive and compliance reporting - Plus: Real-time scanning, SAML SSO, SOC 2 compliant platform (with EU and US hosting options), shared team workspaces, and more - We're constantly [**`adding new features`**](https://feedback.projectdiscovery.io/changelog)! - **Ideal for:** Pentesters, security teams, and enterprises[**`Sign up to Pro`**](https://projectdiscovery.io/pricing?utm_source=github&utm_medium=web&utm_campaign=nuclei_readme) or [**`Talk to our team`**](https://projectdiscovery.io/request-demo?utm_source=github&utm_medium=web&utm_campaign=nuclei_readme) if you have a large organization and complex requirements. # # Documentation Browse the full Nuclei [**`documentation here`**](https://docs.projectdiscovery.io/tools/nuclei/running). If you’re new to Nuclei, check out our [**`foundational YouTube series`**](https://www.youtube.com/playlist?list=PLZRbR9aMzTTpItEdeNSulo8bYsvil80Rl). ### Installation`nuclei` requires **go >= 1.24.2** to install successfully. Run the following command to get the repo: sh go install -v github.com/projectdiscovery/nuclei/v3/cmd/nuclei@latest To learn more about installing nuclei, see `https://docs.projectdiscovery.io/tools/nuclei/install`. ### Command Line FlagsTo display all the flags for the tool: sh nuclei -h Expand full help flags ``` yaml Nuclei is a fast, template based vulnerability scanner focusing on extensive configurability, massive extensibility and ease of use.Usage: ./nuclei [flags]Flags: TARGET: -u, -target string[] target URLs/hosts to scan -l, -list string path to file containing a list of target URLs/hosts to scan (one per line) -targets-inline string inline multiline target list (for use in template profiles) -eh, -exclude-hosts string[] hosts to exclude to scan from the input list (ip, cidr, hostname) -resume string resume scan from and save to specified file (clustering will be disabled) -sa, -scan-all-ips scan all the IP's associated with dns record -iv, -ip-version string[] IP version to scan of hostname (4,6) - (default 4)TARGET-FORMAT: -im, -input-mode string mode of input file (list, burp, jsonl, yaml, openapi, swagger, http) (default "list") -ro, -required-only use only required fields in input format when generating requests -sfv, -skip-format-validation skip format validation (like missing vars) when parsing input file -vtt, -vars-text-templating enable text templating for vars in input file (only for yaml input mode) -vfp, -var-file-paths string[] list of yaml file contained vars to inject into yaml inputTEMPLATES: -nt, -new-templates run only new templates added in latest nuclei-templates release -ntv, -new-templates-version string[] run new templates added in specific version -as, -automatic-scan automatic web scan using wappalyzer technology detection to tags mapping -t, -templates string[] list of template or template directory to run (comma-separated, file) -turl, -template-url string[] template url or list containing template urls to run (comma-separated, file) -ai, -prompt string generate and run template using ai prompt -w, -workflows string[] list of workflow or workflow directory to run (comma-separated, file) -wurl, -workflow-url string[] workflow url or list containing workflow urls to run (comma-separated, file) -validate validate the passed templates to nuclei -nss, -no-strict-syntax disable strict syntax check on templates -td, -template-display displays the templates content -tl list all templates matching current filters -tgl list all available tags -sign signs the templates with the private key defined in NUCLEI_SIGNATURE_PRIVATE_KEY env variable -code enable loading code protocol-based templates -dut, -disable-unsigned-templates disable running unsigned templates or templates with mismatched signature -esc, -enable-self-contained enable loading self-contained templates -egm, -enable-global-matchers enable loading global matchers templates -file enable loading file templatesFILTERING: -a, -author string[] templates to run based on authors (comma-separated, file) -tags string[] templates to run based on tags (comma-separated, file) -etags, -exclude-tags string[] templates to exclude based on tags (comma-separated, file) -itags, -include-tags string[] tags to be executed even if they are excluded either by default or configuration -id, -template-id string[] templates to run based on template ids (comma-separated, file, allow-wildcard) -eid, -exclude-id string[] templates to exclude based on template ids (comma-separated, file) -it, -include-templates string[] path to template file or directory to be executed even if they are excluded either by default or configuration -et, -exclude-templates string[] path to template file or directory to exclude (comma-separated, file) -em, -exclude-matchers string[] template matchers to exclude in result -s, -severity value[] templates to run based on severity. Possible values: info, low, medium, high, critical, unknown -es, -exclude-severity value[] templates to exclude based on severity. Possible values: info, low, medium, high, critical, unknown -pt, -type value[] templates to run based on protocol type. Possible values: dns, file, http, headless, tcp, workflow, ssl, websocket, whois, code, javascript -ept, -exclude-type value[] templates to exclude based on protocol type. Possible values: dns, file, http, headless, tcp, workflow, ssl, websocket, whois, code, javascript -tc, -template-condition string[] templates to run based on expression conditionOUTPUT: -o, -output string output file to write found issues/vulnerabilities -sresp, -store-resp store all request/response passed through nuclei to output directory -srd, -store-resp-dir string store all request/response passed through nuclei to custom directory (default "output") -silent display findings only -nc, -no-color disable output content coloring (ANSI escape codes) -j, -jsonl write output in JSONL(ines) format -irr, -include-rr -omit-raw include request/response pairs in the JSON, JSONL, and Markdown outputs (for findings only) [DEPRECATED use -omit-raw] (default true) -or, -omit-raw omit request/response pairs in the JSON, JSONL, and Markdown outputs (for findings only) -ot, -omit-template omit encoded template in the JSON, JSONL output -nm, -no-meta disable printing result metadata in cli output -ts, -timestamp enables printing timestamp in cli output -rdb, -report-db string nuclei reporting database (always use this to persist report data) -ms, -matcher-status display match failure status -me, -markdown-export string directory to export results in markdown format -se, -sarif-export string file to export results in SARIF format -je, -json-export string file to export results in JSON format -jle, -jsonl-export string file to export results in JSONL(ine) format -pe, -pdf-export string file to export results in PDF format -rd, -redact string[] redact given list of keys from query parameter, request header and bodyCONFIGURATIONS: -config string path to the nuclei configuration file -tp, -profile string template profile config file to run -tpl, -profile-list list community template profiles -fr, -follow-redirects enable following redirects for http templates -fhr, -follow-host-redirects follow redirects on the same host -mr, -max-redirects int max number of redirects to follow for http templates (default 10) -dr, -disable-redirects disable redirects for http templates -rc, -report-config string nuclei reporting module configuration file -H, -header string[] custom header/cookie to include in all http request in header:value format (cli, file) -V, -var value custom vars in key=value format -r, -resolvers string file containing resolver list for nuclei -sr, -system-resolvers use system DNS resolving as error fallback -dc, -disable-clustering disable clustering of requests -passive enable passive HTTP response processing mode -fh2, -force-http2 force http2 connection on requests -ev, -env-vars enable environment variables to be used in template -cc, -client-cert string client certificate file (PEM-encoded) used for authenticating against scanned hosts -ck, -client-key string client key file (PEM-encoded) used for authenticating against scanned hosts -ca, -client-ca string client certificate authority file (PEM-encoded) used for authenticating against scanned hosts -sml, -show-match-line show match lines for file templates, works with extractors only -ztls use ztls library with autofallback to standard one for tls13 [Deprecated] autofallback to ztls is enabled by default -sni string tls sni hostname to use (default: input domain name) -dka, -dialer-keep-alive value keep-alive duration for network requests. -lfa, -allow-local-file-access allows file (payload) access anywhere on the system -lna, -restrict-local-network-access blocks connections to the local / private network -i, -interface string network interface to use for network scan -at, -attack-type string type of payload combinations to perform (batteringram,pitchfork,clusterbomb) -sip, -source-ip string source ip address to use for network scan -rsr, -response-size-read int max response size to read in bytes -rss, -response-size-save int max response size to read in bytes (default 1048576) -reset reset removes all nuclei configuration and data files (including nuclei-templates) -tlsi, -tls-impersonate enable experimental client hello (ja3) tls randomization -hae, -http-api-endpoint string experimental http api endpointINTERACTSH: -iserver, -interactsh-server string interactsh server url for self-hosted instance (default: oast.pro,oast.live,oast.site,oast.online,oast.fun,oast.me) -itoken, -interactsh-token string authentication token for self-hosted interactsh server -interactions-cache-size int number of requests to keep in the interactions cache (default 5000) -interactions-eviction int number of seconds to wait before evicting requests from cache (default 60) -interactions-poll-duration int number of seconds to wait before each interaction poll request (default 5) -interactions-cooldown-period int extra time for interaction polling before exiting (default 5) -ni, -no-interactsh disable interactsh server for OAST testing, exclude OAST based templatesFUZZING: -ft, -fuzzing-type string overrides fuzzing type set in template (replace, prefix, postfix, infix) -fm, -fuzzing-mode string overrides fuzzing mode set in template (multiple, single) -fuzz enable loading fuzzing templates (Deprecated: use -dast instead) -dast enable / run dast (fuzz) nuclei templates -dts, -dast-server enable dast server mode (live fuzzing) -dtr, -dast...{card-default label="? 工具信息" /} ? 项目地址:[https://github.com/projectdiscovery/nuclei](https://github.com/projectdiscovery/nuclei) ⭐ Star数:31053 ? 开发语言:Go ? 项目描述:Nuclei是一款快速、可定制的漏洞扫描器,由全球安全社区提供支持,构建在一个简单的基于YAML的DSL之上,使协作能够解决互联网上的流行漏洞。它可帮助您查找应用程序、API、网络、DNS和云配置中的漏洞。 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/projectdiscovery/nuclei/archive/refs/heads/dev.zip"} {cloud type="default" title="网盘下载" url="https://github.com/projectdiscovery/nuclei"}总的来说,**nuclei**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
vuls - 提升工作效率的好帮手 推荐一个实用的开源工具——vuls。项目由future-architect开发维护,GitHub上获得了 12253 个Star。简单来说,它是一款适用于Linux、FreeBSD、Container、WordPress、编程语言库、网络设备的无代理漏洞扫描程序,对于站长和开发者来说是个不错的工具。 工具功能介绍 Vuls-logoVulnerability scanner for Linux/FreeBSD, agent-less, written in Go. Twitter: @vuls_enVuls-AbstractVulsrepoVuls-slack---- Abstract For a system administrator, having to perform security vulnerability analysis and software update on a daily basis can be a burden. To avoid downtime in a production environment, it is common for a system administrator to choose not to use the automatic update option provided by the package manager and to perform update manually. This leads to the following problems.- The system administrator will have to constantly watch out for any new vulnerabilities in NVD (National Vulnerability Database) or similar databases. It might be impossible for the system administrator to monitor all the software if there are a large number of software packages installed in the server. It is expensive to perform analysis to determine the servers affected by new vulnerabilities. The possibility of overlooking a server or two during analysis is there.Vuls is a tool created to solve the problems listed above. It has the following characteristics.- Informs users of the vulnerabilities that are related to the system. Informs users of the servers that are affected. Vulnerability detection is done automatically to prevent any oversight. A report is generated on a regular basis using CRON or other methods. to manage vulnerability.Vuls-Motivation---- Main Features Scan for any vulnerabilities in Linux/FreeBSD/Windows/macOSSupports major Linux/FreeBSD/Windows/macOS- Alpine, Amazon Linux, CentOS, AlmaLinux, Rocky Linux, Debian, Oracle Linux, Raspbian, RHEL, openSUSE, openSUSE Leap, SUSE Enterprise Linux, Fedora, and Ubuntu FreeBSD Windows macOS Cloud, on-premise, Running Docker Container High-quality scan- Vulnerability Database NVD JVN(Japanese)- OVAL Red Hat Debian Ubuntu SUSE Oracle Linux- Security Advisory Alpine-secdb Red Hat Security Advisories Debian Security Bug Tracker Ubuntu CVE Tracker Microsoft CVRF- Commands(yum, zypper, pkg-audit) RHSA / ALAS / ELSA / FreeBSD-SA Changelog- PoC, Exploit Exploit Database Metasploit-Framework modules qazbnm456/awesome-cve-poc nomi-sec/PoC-in-GitHub gmatuz/inthewilddb projectdiscovery/nuclei-templates- CERT US-CERT JPCERT- KEV CISA(Cybersecurity & Infrastructure Security Agency): Known Exploited Vulnerabilities Catalog VulnCheck: VulnCheck KEV- Cyber Threat Intelligence(MITRE ATT&CK and CAPEC) mitre/cti- Libraries aquasecurity/vuln-list- WordPress wpscan Scan modeFast Scan- Scan without root privilege, no dependencies Almost no load on the scan target server Offline mode scan with no internet access. (CentOS, Alma Linux, Rocky Linux, Debian, Oracle Linux, Red Hat, Fedora, and Ubuntu)Fast Root Scan- Scan with root privilege Almost no load on the scan target server Detect processes affected by update using yum-ps (Amazon Linux, CentOS, Alma Linux, Rocky Linux, Oracle Linux, Fedora, and RedHat) Detect processes which updated before but not restarting yet using checkrestart of debian-goodies (Debian and Ubuntu) Offline mode scan with no internet access. (CentOS, Alma Linux, Rocky Linux, Debian, Oracle Linux, Red Hat, Fedora, and Ubuntu) Remote, Local scan mode, Server modeRemote scan mode- User is required to only set up one machine that is connected to other target servers via SSHLocal scan mode- If you don't want the central Vuls server to connect to each server by SSH, you can use Vuls in the Local Scan mode.Server mode- First, start Vuls in server mode and listen as an HTTP server. Next, issue a command on the scan target server to collect software information. Then send the result to Vuls Server via HTTP. You receive the scan results as JSON format. No SSH needed, No Scanner needed. Only issuing Linux commands directory on the scan target server. Dynamic Analysis- It is possible to acquire the state of the server by connecting via SSH and executing the command. Vuls warns when the scan target server was updated the kernel etc. but not restarting it. Scan vulnerabilities of non-OS-packages- Libraries of programming language Self-compiled software Network DevicesVuls has some options to detect the vulnerabilities- Lockfile based Scan GitHub Integration Common Platform Enumeration (CPE) based Scan OWASP Dependency Check Integration Scan WordPress core, themes, plugins- Scan WordPress MISC- Nondestructive testing Pre-authorization is NOT necessary before scanning on AWS Vuls works well with Continuous Integration since tests can be run every day. This allows you to find vulnerabilities very quickly. Auto-generation of configuration file template Auto-detection of servers set using CIDR, generate configuration file template Email and Slack notification is possible (supports Japanese language) Scan result is viewable on accessory software, TUI Viewer in a terminal or Web UI (VulsRepo).---- What Vuls Doesn't Do- Vuls doesn't update the vulnerable packages.---- Document For more information such as Installation, Tutorial, Usage, visit vuls.io 日本語翻訳ドキュメント---- Authorskotakanbe (@kotakanbe) created vuls and these fine people have contributed. Contributesee vulsdoc---- Sponsors| | | Tines is no-code automation for security teams. Build powerful, reliable workflows without a development team. SAKURA internet Inc. is an Internet company founded in 1996. We provide cloud computing services such as "Sakura's Shared Server", "Sakura's VPS", and "Sakura's Cloud" to meet the needs of a wide range of customers, from individuals and corporations to the education and public sectors, using its own data centers in Japan. Based on the philosophy of "changing what you want to do into what you can do," we offer DX solutions for all fields.----License Please see LICENSE. {card-default label="? 工具信息" /} ? 项目地址:https://github.com/future-architect/vuls ⭐ Star数:12253 ? 开发语言:Go ? 项目描述:适用于Linux、FreeBSD、Container、WordPress、编程语言库、网络设备的无代理漏洞扫描程序 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/future-architect/vuls/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/future-architect/vuls"} 总的来说,vuls是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
站长必备!hackingtool 效率神器分享 推荐一个实用的开源工具——**hackingtool**。项目由Z4nzu开发维护,GitHub上获得了 **79344** 个Star。简单来说,它是一款面向黑客的一体化黑客工具,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 **215 curated tools across 21 categories** — recon, OSINT, web, wireless, phishing, forensics, post-exploitation and more — with an **AI layer that turns plain English into the right tool and the exact command**.**Built for** penetration testers · red teamers · blue-team/SOC and DFIR analysts · OSINT researchers · bug-bounty hunters · CTF players · security researchers and students — all working **legally, on systems they own or are authorised to test**. ! ! ! ! ! ---## Contents- [Why hackingtool](#why-hackingtool) - [Tool Categories](#tool-categories) - [Installation](#installation) - [From source with pipx (recommended)](#from-source-with-pipx-recommended) - [For development](#for-development) - [Docker](#docker) - [Optional runtimes](#optional-runtimes) - [Quick Commands](#quick-commands) - [Command reference](#command-reference) - [Features](#features) - [? `/find` — a tool for a need you don't have yet](#-find--a-tool-for-a-need-you-dont-have-yet) - [? `/goal` — plan an objective, run it one step at a time](#-goal--plan-an-objective-run-it-one-step-at-a-time) - [? Recommendations — say what you want in plain English](#-recommendations--say-what-you-want-in-plain-english) - [? Tags and search](#-tags-and-search) - [▶ Background panes (tmux)](#-background-panes-tmux) - [⚙ Settings and the AI layer](#-settings-and-the-ai-layer) - [? Headless engagements](#-headless-engagements) - [Documentation](#documentation) - [Contributing](#contributing) - [Support & Sponsor](#support--sponsor) - [Social](#social)---## Why hackingtool- **? AI-guided workflow** — describe what you want ("find subdomains of example.com") and it maps your intent to the right tools, hands you the exact documented command, plans an objective step by step, then summarizes findings and drafts an engagement report. Bring your own key or run a local model — nothing auto-executes and nothing is fabricated. - **? 215 curated tools, one console** — install and run across 21 categories without hunting down Git repos; a fixed tag taxonomy (63 tags in use) makes every tool discoverable. - **? It knows what it doesn't have** — `/find` searches your catalog first, then the GitHub API, and shows real maintained projects with the reason each was ranked. - **? Safe by default** — standard installs, **no `curl | bash`**, downloads pinned + SHA-256 verified, list-form `subprocess`, no forced `sudo`, and [signed releases with an SBOM](SECURITY.md#verifying-a-release). - **? For the whole spectrum** — red team, blue team, OSINT, bug bounty, CTF/THM, forensics/IR — all on **authorized targets only**.The console on launch — live system readout, and / opens the command palette. ---## Tool Categories**215 tools across 21 categories** — the full list, with links and tags, is in **[docs/TOOLS.md](docs/TOOLS.md)**.| # | Category | Tools | | # | Category | Tools | |:---:|---|:---:|---|:---:|---|:---:| | 1 | ? [Anonymously Hiding Tools](docs/TOOLS.md#-anonymously-hiding-tools) | 5 | | 12 | ? [Reverse engineering tools](docs/TOOLS.md#-reverse-engineering-tools) | 10 | | 2 | ? [Information gathering tools](docs/TOOLS.md#-information-gathering-tools) | 26 | | 13 | ⚡ [DDOS Attack Tools](docs/TOOLS.md#-ddos-attack-tools) | 7 | | 3 | ? [Wordlist Generator](docs/TOOLS.md#-wordlist-generator) | 8 | | 14 | ? [Remote Administrator Tools (RAT)](docs/TOOLS.md#-remote-administrator-tools-rat) | 4 | | 4 | ? [Wireless attack tools](docs/TOOLS.md#-wireless-attack-tools) | 17 | | 15 | ? [XSS Attack Tools](docs/TOOLS.md#-xss-attack-tools) | 6 | | 5 | ? [SQL Injection Tools](docs/TOOLS.md#-sql-injection-tools) | 7 | | 16 | ? [Steganography Tools](docs/TOOLS.md#-steganography-tools) | 10 | | 6 | ? [Phishing attack tools](docs/TOOLS.md#-phishing-attack-tools) | 13 | | 17 | ? [Active Directory Tools](docs/TOOLS.md#-active-directory-tools) | 10 | | 7 | ? [Web Attack tools](docs/TOOLS.md#-web-attack-tools) | 23 | | 18 | ☁ [Cloud Security Tools](docs/TOOLS.md#-cloud-security-tools) | 7 | | 8 | ? [Post exploitation tools](docs/TOOLS.md#-post-exploitation-tools) | 15 | | 19 | ? [Mobile Security Tools](docs/TOOLS.md#-mobile-security-tools) | 6 | | 9 | ? [Forensic tools](docs/TOOLS.md#-forensic-tools) | 12 | | 20 | ✨ [Other tools](docs/TOOLS.md#-other-tools) | 10 | | 10 | ? [Payload creation tools](docs/TOOLS.md#-payload-creation-tools) | 6 | | 21 | ? [Password / Hash Cracking](docs/TOOLS.md#-password--hash-cracking) | 7 | | 11 | ? [Exploit framework](docs/TOOLS.md#-exploit-framework) | 6 | | | | |59 further entries are archived (unmaintained or dead upstream) and hidden unless you set `show_archived true` via `/config`. The in-app header counts 22 categories / 217 tools because it also counts the built-in Update / Uninstall menu.---## Installation Requires **Python 3.10+** on **Linux or macOS** (Kali, Parrot, Debian/Ubuntu, Arch, …). Windows is not supported — the app tells you so and exits. No `curl | bash`: every path below is a standard, verifiable install.### From source with pipx (recommended)[pipx](https://pipx.pypa.io) installs hackingtool into its own isolated environment and puts the `hackingtool` command on your PATH, so you can launch it from any directory. bash # 1 — get the code git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool # 2 — install it onto your PATH (isolated venv, no system Python touched) pipx install . # 3 — run it from anywhere hackingtool No pipx yet? bash # macOS brew install pipx && pipx ensurepath # Debian / Ubuntu / Kali sudo apt install pipx && pipx ensurepath Open a new shell after `pipx ensurepath` so the PATH change takes effect. To update later: `git pull && pipx install . --force`. To remove it: `pipx uninstall hackingtool`. Alternative: uv tool install . (same result, uses uv instead of pipx) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv tool install . # installs the `hackingtool` executable on your PATH hackingtool Alternative: plain venv + pip (no PATH changes) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool python3 -m venv .venv && . .venv/bin/activate pip install . # or: pip install -e . for an editable dev install hackingtool The command is only on your PATH while that venv is activated. ### For development[uv](https://docs.astral.sh/uv/) creates the virtualenv and installs everything from `pyproject.toml` / `uv.lock` in one step: bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv sync uv run hackingtool No uv yet? `pipx install uv` (or see the [uv install docs](https://docs.astral.sh/uv/getting-started/installation/)).**Contributing?** `make setup` wires the pre-push hook and `make check` runs the full gate (lint + tests + catalog validation). See [CONTRIBUTING.md](CONTRIBUTING.md).### Docker Pull and run the published : bash docker run -it --rm hardikzinzu/hackingtool:latest Or build it locally from a checkout: bash git clone https://github.com/Z4nzu/hackingtool.git && cd hackingtool docker build -t hackingtool . docker run -it --rm hackingtool ### Optional runtimesSome individual tools need a language runtime to install/run; the core app doesn't.| Dependency | Version | Needed for | |---|---|---| | Go | 1.21+ | nuclei, ffuf, amass, httpx, katana, dalfox, gobuster, subfinder | | Ruby | any | haiti, evil-winrm | | tmux | any | background panes (`/run … &`, `/panes`, `/attach`) | | Docker | any | Mythic, MobSF (optional) |---## Quick CommandsLaunch `hackingtool` and type. There are only three kinds of input:| You type | It means | Example | |---|---|---| | `/…` | a command you run | `/search subdomain` | | `@…` | a thing you name | `@nmap`, `@tag:osint` | | anything else | plain English "what I want to do" | `crack a wifi handshake` |@ completes tool names — @tag: completes tags, / completes commands. ### Command reference| Command | Aliases | What it does | |---|---|---| | `/run [args] [&]` | `/open` | open a tool's menu; with a trailing `&` it runs in a background tmux pane instead (that's where `args` are used) | | `/search ` | | search tools by name, description or tag | | `/tags` | | list every tag with its tool count | | `/ai ` | `/recommend`, `/r` | recommend tools for a goal | | `/goal ` | | AI-plan an objective and run it step by step, with per-step confirmation | | `/find ` | `/discover` | find tools for a need — your catalog first, then GitHub (suggest-only) | | `/panes` | `/jobs` | list background panes | | `/attach` | | attach to the background session (`Ctrl-b` `d` to return) | | `/kill ` | | kill one background pane, or all of them | | `/config [key value]` | | view/change settings; `/config test` checks the AI connection, `/config github` checks the GitHub token | | `/skill` | | show the operator playbook | | `/update` · `/uninstall` | `/remove` | update system packages or hackingtool · remove hackingtool and its tools | | `/clear` | `/cls` | clear the screen | | `/back` | `/b` | leave the current tool and go back | | `/help` | `/?`, `/h` | quick reference card | | `/quit` | `/q`, `/exit` | exit (also `q`, `Ctrl-C`, `Ctrl-D`) | | `@` | | open a tool (case-insensitive, fuzzy fallback) | | `@tag:` | | list and k from the tools carrying that tag |Inside a category: `1–N` k a tool · `97` install everything not yet installed · `98` archived tools · `99` back. Inside a tool: `1` install · `2` run · `c` ask for the exact command for your goal · `98` project page · `99` back./help — the same card, in the app. On a non-interactive terminal (or without `prompt_toolkit`) hackingtool falls back to the classic numbered menu, where `/` or `s` searches, `t` filters by tag, `r` or `a` recommends, `?` helps and `q` quits. Force it with `hackingtool --classic`.> **New here?** [docs/HOW-TO-USE.md](docs/HOW-TO-USE.md) walks through each of these > start to finish with numbered steps.---## Features ### ? `/find` — a tool for a need you don't have yetSearches the 215 curated tools first, then the GitHub search API, and ranks the results explainably. **Suggest-only** — it never clones, installs or runs anything — and it makes **zero model calls**./find crack a wpa handshakeIn your toolbox (vetted) • aircrack-ng (WiFi security suite) • Kismet (wireless detector / WIDS) • Reaver (WPS PIN attack) • WiGLE (wardriving map & API) • hashcat example hashes (WPA mode 22000)Found on GitHub — NOT vetted by uswifiphisher/wifiphisher 14713★ GPL-3.0 The Rogue Access Point Framework 14713★ · trusted author (ships in our catalog) · active · matches: security, wifi git clone https://github.com/wifiphisher/wifiphisher … Press `a` to keep a result: it is saved to `~/.hackingtool/found.yaml` as a "Discovered tools" entry — title, tags, description, link, and **no install or run command**, so a discovered entry can never execute anything. It shows up in your menu and in `/search` next launch.Out-of-scope asks (jamming, DoS, mass-targeting, malware) are refused **before any network call**, with an authorized alternative where one exists. Defensive/DFIR phrasing is never refused.Works anonymously at 10 GitHub searches/minute; a **no-scope, no-permission** token raises that to 30 — see [`/config github`](docs/HOW-TO-USE.md#7-add-a-github-token-for-find-config-github).### ? `/goal` — plan an objective, run it one step at a time /goal find live subdomains of example.com hackingtool drafts a short plan of real commands (with the reason for each step and an install hint for tools you don't have), asks you to confirm you are **authorized** to test the target, then walks the steps: `[y]` run · `[s]` skip · `[e]` edit · `[q]` abort. Every step runs list-form — never through a shell — and each goal gets a timestamped workspace under `~/.hackingtool/goals/` holding `plan.json`, a UTC-stamped `run.log`, and the raw output of each step.The model is called **once**, for planning; tool output is never fed back to it. With no model configured, `/goal` degrades to tool recommendations for the same objective.### ? Recommendations — say what you want in plain EnglishBare text (or `/ai`) maps intent to tools. The model may only return tags from the fixed taxonomy, and the catalog resolves tags → tools, so a tool can never be invented; with no model reachable a stdlib keyword matcher answers instead./ai — k one of the common tasks, or type the job in your own words. ### ? Tags and search`/tags` prints every tag in use with its live tool count; `@tag:` opens the tools carrying it; `/search ` matches names, descriptions and tags. /tags — 63 tags in use, with the number of tools behind each. ### ▶ Background panes (tmux)Long scans shouldn't block your console. With tmux installed, `/run … &` opens a labeled window in one detached `hackingtool` session: /run nmap -sV -oA scan 10.0.0.5 & ▶ started 'nmap' in background — /attach to view ` /panes` lists them, `/attach` watches one (`Ctrl-b` `d` to come back), `/kill ` or `/kill all` stops them, and the status line under the prompt shows `▶ N running`. No tmux? It says so and opens the tool inline instead; disable it entirely with `/config background_runner off`.### ⚙ Settings and the AI layer`/config` opens a full-screen settings editor (`↑↓` move, `←→` change, `Enter` edit, `t` test the connection, `Esc` close); `/config ` sets one key from the prompt. Settings live in `~/.hackingtool/config.json`.The AI layer is **opt-in and bring-your-own-key**: an OpenAI-compatible endpoint when `ai_base_url` + an API key are set, else a local [Ollama](https://ollama.com), else nothing — every feature degrades to a deterministic offline behaviour instead of guessing. Your API key is written only to `~/.hackingtool/.env` (mode 600), never to `config.json`, and never printed back. `/config test` reports the real failure if a probe fails.### ? Headless engagementsThe same catalog drives a non-interactive orchestrator that normalizes tool output into one `findings.json`: bash hackingtool --engagement acme --targets example.com --pipeline recon hackingtool --engagement acme --report # deterministic Markdown report hackingtool --engagement acme --ai-summary # opt-in triage of the REAL findings hackingtool --engagement acme --ai-report # opt-in narrative draft (report.draft.md) Out-of-scope targets are flagged and logged before anything runs, and the AI passes only ever summarize findings that exist.---## Documentation... {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/Z4nzu/hackingtool](https://github.com/Z4nzu/hackingtool) ⭐ Star数:79344 ? 开发语言:Python ? 项目描述:面向黑客的一体化黑客工具 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool"}总的来说,**hackingtool**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
分享一个不错的绿色软件:antSword 在寻找好用的工具软件时,发现了antSword这个项目。它的定位是mirror https://github.com/AntSwordProject/antSword,目前在Gitee上已经积累了14个Star,更新也比较活跃,最后更新时间是2024年04月17日。下面来详细了解一下这个工具的功能特点。 工具功能介绍 AntSword in your hands, no worries in your mind!AntSword is an open source, cross-platform website administration tool, being designed to meet the needs of penetration testers together with security researchers with permissions and/or authorizations as well as webmasters. Anyone shall not use it for illegal purposes and profitability. Besides that, publishing unauthorized modified version is also prohibited, or otherwise bear legal responsibilities. This software, of which the development thought is modularization, is intended to provide easy-to-understand codes and modification guidelines for users of different levels. Therefore, any contribution making by everyone to this project is encouraged, whether large or small. By doing so, this tool can be more convenient and consequently become your most powerful kit! 中文说明 / Document / Changelog Development stack Electron ES6 dhtmlx Nodejs And other libraries called in the project. Screenshots [url-mainui] More Screenshots [url-filemanager] [url-terminal] [url-database] [url-pluginstore] Quick Start See document: Quick Start Contribute See document: Make contributions to AntSword Thanks Thanks to anyone who made any contributions.Other 404StarLink 2.0 - Galaxy ! antSword has joined 404Team 404StarLink 2.0 - Galaxy LICENSE LICENSE 总的来说,antSword是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一个mirror https://github.com/AntSwordProject/antSword的解决方案,不妨下载试试。使用前建议仔细阅读项目文档。 {card-default label="? 工具信息" /} ? 工具名称:antSword ? 开发作者:medicean ? 工具描述:mirror https://github.com/AntSwordProject/antSword ? 开发语言:未知 ? 开源协议:未知开源协议 ⭐ Star数:14 | ? Fork数:14 ? 更新时间:2024年04月17日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/AntSwordProject/antSword/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/AntSwordProject/antSword.git"}
-
OneForAll 是什么?好用的工具软件推荐 今天给大家分享一款实用的开源工具——**OneForAll**。这个工具在Gitee上获得了158个Star,主要功能是OneForAll是一款功能强大的子域收集工具,对于需要提高工作效率的朋友来说是个不错的选择。 # # 工具功能介绍 [](https://travis-ci.org/shmilylty/OneForAll) ?**OneForAll是一款功能强大的子域收集工具** ?[English Document](https://github.com/shmilylty/OneForAll/tree/master/docs/en-us/README.md)  # # ?上手指南 ? 请务必花一点时间阅读此文档,有助于你快速熟悉OneForAll! ?安装要求 OneForAll基于[Python 3.6.0]( https://www.python.org/downloads/release/python-360/ )开发和测试,OneForAll需要高于Python 3.6.0的版本才能运行。 安装Python环境可以参考[Python 3 安装指南](https://pythonguidecn.readthedocs.io/zh/latest/starting/installation.html#python-3)。运行以下命令检查Python和pip3版本: bash python -V pip3 -V 如果你看到类似以下的输出便说明Python环境没有问题: bash Python 3.6.0 pip 19.2.2 from C:\Users\shmilylty\AppData\Roaming\Python\Python36\site-packages\pip (python 3.6) ✔安装步骤(git 版) 1. **下载** 由于该项目**处于开发中**,会不断进行更新迭代,下载时请使用`git clone`**克隆**最新代码仓库,也方便后续的更新,不推荐从Releases下载,因为Releases里版本更新缓慢,也不方便更新, 本项目已经在[码云](https://gitee.com/shmilylty/OneForAll.git)(Gitee)镜像了一份,国内推荐使用码云进行克隆比较快: bash git clone https://gitee.com/shmilylty/OneForAll.git 或者: bash git clone https://github.com/shmilylty/OneForAll.git 2. **安装** 你可以通过pip3安装OneForAll的依赖,以下为**Windows系统**下使用**pip3**安装依赖的示例:注意:如果你的Python3安装在系统Program Files目录下,如:`C:\Program Files\Python36`,那么请以管理员身份运行命令提示符cmd执行以下命令! bash cd OneForAll/ python3 -m pip install -U pip setuptools wheel -i https://mirrors.aliyun.com/pypi/simple/ pip3 install -r requirements.txt -i https://mirrors.aliyun.com/pypi/simple/ python3 oneforall.py --help 其他系统平台的请参考[依赖安装](https://github.com/shmilylty/OneForAll/tree/master/docs/installation_dependency.md),如果在安装依赖过程中发现编译某个依赖库失败时可以参考[常见问题与回答.md](https://github.com/shmilylty/OneForAll/tree/master/docs/troubleshooting.md)文档中解决方法,如果依然不能解决欢迎加群反馈问题。 3. **更新** 执行以下命令**更新**项目(可保存对`/config/setting.py`和`/config/api.py`的修改): bash git stash # 暂存本地的修改 git fetch --all # 拉取项目更新 git pull # 下载覆盖 git stash pop # 释放本地修改 ✔安装步骤(docker 版) 首先下载并编辑配置文件,添加自己的`api`和个性化设置,并保留原始文件结构 config ├── api.py ├── log.py └── setting.py 拉取镜像并执行,其中`~/.config`替换为你自己配置文件所在文件夹的路径 shell docker pull shmilylty/oneforall docker run -it --rm -v ~/results:/OneForAll/results -v ~/.config:/OneForAll/config shmilylty/oneforall --target example.com run 参数直接加在指令末尾,结果会输出在本地目录`~/results`,如需保存到其他位置,可以自行修改 ✨使用演示 如果你是通过pip3安装的依赖则使用以下命令运行示例: bash python3 oneforall.py --target example.com run python3 oneforall.py --targets ./example.txt run ?结果说明 我们以`python3 oneforall.py --target example.com run`命令为例,OneForAll在默认参数正常执行完毕会在results目录生成相应结果:  `example.com.csv`是每个主域下的子域收集结果。 `all_subdomain_result_1583034493.csv`是每次运行OneForAll收集到子域的汇总结果,包含`example.com.csv`,方便在批量收集场景中获取全部结果。 `result.sqlite3`是存放每次运行OneForAll收集到子域的SQLite3结果数据库,其数据库结构如下图:  其中类似`example_com_origin_result`表存放每个模块最初子域收集结果。 其中类似`example_com_resolve_result`表存放对子域进行解析后的结果。 其中类似`example_com_last_result`表存放上一次子域收集结果(需要收集两次以上才会生成)。 其中类似`example_com_now_result`表存放现在子域收集结果,一般情况关注这张表就可以了。 更多信息请参阅[字段解释说明](./docs/field.md)。 ?使用帮助 命令行参数只提供了一些常用参数,更多详细的参数配置请见[setting.py](https://github.com/shmilylty/OneForAll/tree/master/config/setting.py),如果你认为有些参数是命令界面经常使用到的或缺少了什么参数等问题非常欢迎反馈。由于众所周知的原因,如果要使用一些被墙的收集接口请先到[setting.py](https://github.com/shmilylty/OneForAll/tree/master/config/setting.py)配置代理,有些收集模块需要提供API(大多都是可以注册账号免费获取),如果需要使用请到[api.py](https://github.com/shmilylty/OneForAll/tree/master/config/api.py)配置API信息,如果不使用请忽略有关报错提示。(详细模块请阅读[收集模块说明](https://github.com/shmilylty/OneForAll/tree/master/docs/collection_modules.md)) OneForAll命令行界面基于[Fire](https://github.com/google/python-fire/)实现,有关Fire更高级使用方法请参阅[使用Fire CLI](https://github.com/google/python-fire/blob/master/docs/using-cli.md)。 [oneforall.py](https://github.com/shmilylty/OneForAll/tree/master/oneforall.py)是主程序入口,oneforall.py可以调用[brute.py](https://github.com/shmilylty/OneForAll/tree/master/brute.py),[takerover.py](https://github.com/shmilylty/OneForAll/tree/master/takerover.py)及[dbexport.py](https://github.com/shmilylty/OneForAll/tree/master/dbexport.py)等模块,为了方便进行子域爆破独立出了brute.py,为了方便进行子域接管风险检查独立出了takerover.py,为了方便数据库导出独立出了dbexport.py,这些模块都可以单独运行,并且所接受参数要更丰富一点,如果要单独使用这些模块请参考[使用帮助](https://github.com/shmilylty/OneForAll/tree/master/docs/usage_help.md) ❗注意:当你在使用过程中遇到一些问题或者疑惑时,请先到[Issues](https://github.com/shmilylty/OneForAll/issues)里使用搜索找找答案,还可以参阅[常见问题与回答](https://github.com/shmilylty/OneForAll/tree/master/docs/troubleshooting.md)。 **oneforall.py使用帮助** 以下帮助信息可能不是最新的,你可以使用`python oneforall.py --help`获取最新的帮助信息。 bash python oneforall.py --help bash NAME oneforall.py - OneForAll帮助信息 SYNOPSIS oneforall.py COMMAND | --target=TARGET DESCRIPTION OneForAll是一款功能强大的子域收集工具 Example: python3 oneforall.py version python3 oneforall.py --target example.com run python3 oneforall.py --targets ./domains.txt run python3 oneforall.py --target example.com --valid None run python3 oneforall.py --target example.com --brute True run python3 oneforall.py --target example.com --port small run python3 oneforall.py --target example.com --fmt csv run python3 oneforall.py --target example.com --dns False run python3 oneforall.py --target example.com --req False run python3 oneforall.py --target example.com --takeover False run python3 oneforall.py --target example.com --show True run Note: 参数alive可选值True,False分别表示导出存活,全部子域结果 参数port可选值有'default', 'small', 'large', 详见config.py配置 参数fmt可选格式有 'csv','json' 参数path默认None使用OneForAll结果目录生成路径 ARGUMENTS TARGET 单个域名(二选一必需参数) TARGETS 每行一个域名的文件路径(二选一必需参数) FLAGS --brute=BRUTE s --dns=DNS DNS解析子域(默认True) --req=REQ HTTP请求子域(默认True) --port=PORT 请求验证子域的端口范围(默认只探测80端口) --valid=VALID 只导出存活的子域结果(默认False) --fmt=FMT 结果保存格式(默认csv) --path=PATH 结果保存路径(默认None) --takeover=TAKEOVER 检查子域接管(默认False) # # ?项目简介 项目地址:[https://github.com/shmilylty/OneForAll](https://github.com/shmilylty/OneForAll) 在渗透测试中信息收集的重要性不言而喻,子域收集是信息收集中必不可少且非常重要的一环,目前网上也开源了许多子域收集的工具,但是总是存在以下部分问题: * **不够强大**,子域收集的接口不够多,不能做到对批量子域自动收集,没有自动子域解析,验证,FUZZ以及信息拓展等功能。 * **不够友好**,固然命令行模块比较方便,但是当可选的参数很多,要实现的操作复杂,用命令行模式就有点不够友好,如果有交互良好,高可操作的前端那么使用体验就会好很多。 * **缺少维护**,很多工具几年没有更新过一次,issues和PR是啥,不存在的。 * **效率问题**,没有利用多进程,多线程以及异步协程技术,速度较慢。为了解决以上痛点,此项目应用而生,正如其名,我希望OneForAll是一款集百家之长,功能强大的全面快速子域收集终极神器?。 目前OneForAll还在开发中,肯定有不少问题和需要改进的地方,欢迎大佬们提交[Issues](https://github.com/shmilylty/OneForAll/issues)和[PR](https://github.com/shmilylty/OneForAll/pulls),用着还行给个小星星✨吧,目前有一个专门用于OneForAll交流和反馈 # # ?功能特性 * **收集能力强大**,详细模块请阅读[收集模块说明](https://github.com/shmilylty/OneForAll/tree/master/docs/collection_modules.md)。 1. 利用证书透明度收集子域(目前有6个模块:`censys_api`,`certspotter`,`crtsh`,`entrust`,`google`,`spyse_api`) 2. 常规检查收集子域(目前有4个模块:域传送漏洞利用`axfr`,检查跨域策略文件`cdx`,检查HTTPS证书`cert`,检查内容安全策略`csp`,检查robots文件`robots`,检查sitemap文件`sitemap`,利用NSEC记录遍历DNS域`dnssec`,后续会添加NSEC3记录等模块) 3. 利用网上爬虫档案收集子域(目前有2个模块:`archivecrawl`,`commoncrawl`,此模块还在调试,该模块还有待添加和完善) 4. 利用DNS数据集收集子域(目前有24个模块:`bevigil_api`, `binaryedge_api`, `bufferover`, `cebaidu`, `chinaz`, `chinaz_api`, `circl_api`, `cloudflare`, `dnsdb_api`, `dnsdumpster`, `hackertarget`, `ip138`, `ipv4info_api`, `netcraft`, `passivedns_api`, `ptrarchive`, `qianxun`, `rapiddns`, `riddler`, `robtex`, `securitytrails_api`, `sitedossier`, `threatcrowd`, `wzpc`, `ximcx`) 5. 利用DNS查询收集子域(目前有5个模块:通过枚举常见的SRV记录并做查询来收集子域`srv`,以及通过查询域名的DNS记录中的MX,NS,SOA,TXT记录来收集子域) 6. 利用威胁情报平台数据收集子域(目前有6个模块:`alienvault`, `riskiq_api`,`threatbook_api`,`threatminer`,`virustotal`,`virustotal_api`该模块还有待添加和完善) 7. 利用搜索引擎发现子域(目前有18个模块:`ask`, `baidu`, `bing`, `bing_api`, `duckduckgo`, `exalead`, `fofa_api`, `gitee`, `github`, `github_api`, `google`, `google_api`, `shodan_api`, `so`, `sogou`, `yahoo`, `yandex`, `zoomeye_api`),在搜索模块中除特殊搜索引擎,通用的搜索引擎都支持自动排除搜索,全量搜索,递归搜索。 * **支持子域爆破**,该模块有常规的字典爆破,也有自定义的fuzz模式,支持批量爆破和递归爆破,自动判断泛解析并处理。 * **支持子域验证**,默认开启子域验证,自动解析子域DNS,自动请求子域获取title和banner,并综合判断子域存活情况。 * **支持子域爬取**,根据已有的子域,请求子域响应体以及响应体里的JS,从中再次发现新的子域。 * **支持子域置换**,根据已有的子域,使用子域替换技术再次发现新的子域。 * **支持子域接管**,默认开启子域接管风险检查,支持子域自动接管(目前只有Github,有待完善),支持批量检查。 * **处理功能强大**,发现的子域结果支持自动去除,自动DNS解析,HTTP请求探测,自动筛选出有效子域,拓展子域的Banner信息,最终支持的导出格式有`txt`, `csv`, `json`。 * **速度极快**,[收集模块](https://github.com/shmilylty/OneForAll/tree/master/collect.py)使用多线程调用,[爆破模块](https://github.com/shmilylty/OneForAll/tree/master/brute.py)使用[massdns](https://github.com/blechschmidt/massdns),DNS解析速度每秒可解析350000以上个域名,子域验证中DNS解析和HTTP请求使用异步多协程,多线程检查[子域接管](https://github.com/shmilylty/OneForAll/tree/master/takeover.py)风险。 * **体验良好**,各模块都有进度条,异步保存各模块结果。如果你有其他很棒的想法请务必告诉我!? # # ?目录结构 更多信息请参阅[目录结构说明](https://github.com/shmilylty/OneForAll/tree/master/docs/directory_structure.md)。 本项目[docs](https://github.com/shmilylty/OneForAll/tree/master/docs/)目录下还提供了一些帮助与说明,如[子域字典来源说明](https://github.com/shmilylty/OneForAll/tree/master/docs/dictionary_source.md)、[泛解析判断流程](https://img.65gw.com/img/999797bebe8603078eedd7a6.png)。 # # ?用到框架 * [aiohttp](https://github.com/aio-libs/aiohttp) - 异步http客户端/服务器框架 * [beautifulsoup4](https://pypi.org/project/beautifulsoup4/) - 可以轻松从HTML或XML文件中提取数据的Python库 * [fire](https://github.com/google/python-fire) - Python Fire是一个纯粹根据任何Python对象自动生成命令行界面(CLI)的库 * [loguru](https://github.com/Delgan/loguru) - 旨在带来愉快的日志记录Python库 * [massdns](https://github.com/blechschmidt/massdns) - 高性能的DNS解析器 * [records](https://github.com/kennethreitz/records) - Records是一个非常简单但功能强大的库,用于对大多数关系数据库进行最原始SQL查询。 * [requests](https://github.com/psf/requests) - Requests 唯一的一个非转基因的 Python HTTP 库,人类可以安全享用。 * [tqdm](https://github.com/tqdm/tqdm) - 适用于Python和CLI的快速,可扩展的进度条库感谢这些伟大优秀的Python库! # # ?版本控制 该项目使用[SemVer](https://semver.org/)语言化版本格式进行版本管理,你可以参阅[变更记录说明](https://github.com/shmilylty/OneForAll/tree/master/docs/changes.md)了解历史变更情况。 # # ⌛后续计划 - [ ] 各模块持续优化和完善 - [ ] 操作强大交互人性的前端界面实现更多信息请参阅[后续开发计划](https://github.com/shmilylty/OneForAll/tree/master/docs/todo.md)。 # # ?贡献 非常热烈欢迎各位大佬一起完善本项目! # # ??贡献者 * **[Jing Ling](https://github.com/shmilylty)** * 核心开发你可以在[贡献者文档](https://github.com/shmilylty/OneForAll/tree/master/docs/contributors.md)中查看所有贡献者以及他们所做出的贡献,感谢他们让OneForAll变得更强大好用。 # # ☕赞赏 如果你觉得这个项目帮助到了你,你可以 ## ?版权 该项目签署了GPL-3.0授权许可,详情请参阅[LICENSE](https://github.com/shmilylty/OneForAll/blob/master/LICENSE)。 # # ?鸣谢 感谢网上开源的各个子域收集项目! 感谢[A-Team](https://github.com/QAX-A-Team)大哥们热情无私的问题解答! # # ?
-
sectoolset 工具软件 功能特点与使用体验 今天给大家分享一款实用的开源工具——sectoolset。这个工具在Gitee上获得了33个Star,主要功能是安全项目工具集合 ,对于需要提高工作效率的朋友来说是个不错的选择。 工具功能介绍 sectoolset -- Github安全相关工具集合 主要内容: 0x00 漏洞利用实战练习&CTF安全竞赛 0x01 安全扫描器 0x02 安全防守 0x03 渗透测试 0x04 漏洞库及利用工具(POC,EXP) 0x05 二进制及代码分析工具 0x06 威胁情报&蜜罐 0x07 安全文档资料 0x10 AI&大模型安全 0x11 所有内容 乌云镜像 乌云镜像,已挂 乌云镜像,已挂 近期安全热点 金刚狼(Kimwolf)僵尸网络正通过机顶盒攻克你的内网 CVE-2025-48384: Git子模块回车符CR解析注入可致RCE GitHub MCP漏洞:劫持MCP服务访问私有仓库数据 glibc iconv()中的缓冲区溢出导致PHP RCE攻击CNEXT(CVE-2024-2961) 论文:红队中AI生成式模型使用调查 关于xz后门详解 ZenHammer:Rowhammer适用于AMD Zen的平台攻击 五眼联盟国家网络安全技术指导书 2018 Blackhat 工具集 Meltdown & Spectre License Licensed under Apache License 2.0. 综合来看,sectoolset在同类工具中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。 {card-default label="? 工具信息" /} ? 工具名称:sectoolset ? 开发作者:ijz ? 工具描述:安全项目工具集合 ? 开发语言:Perl ? 开源协议:未知开源协议 ⭐ Star数:33 | ? Fork数:19 ? 更新时间:2026年04月16日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/ijz/sectoolset/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/ijz/sectoolset.git"}
-
Osintgram 使用教程与功能详解 推荐一个实用的开源工具——**Osintgram**。项目由Datalux开发维护,GitHub上获得了 **14305** 个Star。简单来说,它是一款Osintgram是Instagram上的OSINT工具。它提供了一个交互式外壳,可以通过其昵称对任何用户的Instagram帐户进行分析,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 Osintgram is an **OSINT** tool on Instagram to collect, analyze, and run reconnaissance. Disclaimer: **FOR EDUCATIONAL PURPOSE ONLY! The contributors do not assume any responsibility for the use of this tool.**$${\color{red /}Warning:}$$ It is advisable to **not** use your own/primary account when using this tool.$${\color{red /}Warning:}$$ If you fork the project and add your instagram credentials to you home repository do not upload them to github. You can disable uploading a certain file by adding it to ignore list.## Tools and Commands ?Osintgram offers an interactive shell to perform analysis on Instagram account of any users by its nickname. You can get: text - addrs Get all registered addressed by target photos - captions Get user's photos captions - comments Get total comments of target's posts - followers Get target followers - followings Get users followed by target - fwersemail Get email of target followers - fwingsemail Get email of users followed by target - fwersnumber Get phone number of target followers - fwingsnumber Get phone number of users followed by target - hashtags Get hashtags used by target - info Get target info - likes Get total likes of target's posts - mediatype Get user's posts type (photo or video) - photodes Get description of target's photos - photos Download user's photos in output folder - proDownload user's profile ture - stories Download user's stories - tagged Get list of users tagged by target - wcommented Get a list of user who commented target's photos - wtagged Get a list of user who tagged target You can find detailed commands usage [here](doc/COMMANDS.md).[**Latest version**](https://github.com/Datalux/Osintgram/releases/tag/1.3) | [Commands](doc/COMMANDS.md) | [CHANGELOG](doc/CHANGELOG.md)## FAQ 1. **Can I access the contents of a private profile?** No, you cannot get information on private profiles. You can only get information from a public profile or a profile you follow. The tools that claim to be successful are scams! 2. **What is and how I can bypass the `challenge_required` error?** The `challenge_required` error means that Instagram notice a susious behavior on your profile, so needs to check if you are a real person or a bot. To avoid this you should follow the suggested link and complete the required operation (insert a code, confirm email, etc)## Installation ⚙️1. Fork/Clone/Download this repo`git clone https://github.com/Datalux/Osintgram.git`2. Navigate to the directory`cd Osintgram`3. Create a virtual environment for this project`python3 -m venv venv`4. Load the virtual environment - On Windows Powershell: `.\venv\Scripts\activate.ps1` - On Linux and Git Bash: `source venv/bin/activate` 5. Run `pip install -r requirements.txt`6. Open the `credentials.ini` file in the `config` folder and write your Instagram account username and password in the corresponding fields. Or use `hikerapi_token` from https://hikerapi.com/tokens (first 100 requests are free after registration and confirmation of your tg)Alternatively, you can run the `make setup` command to populate this file for you.7. Run the main.py script in one of three ways* As an interactive prompt `python3 main.py ` * Or execute your command straight away `python3 main.py --command ` * Or execute using HikerAPI token via env `HIKERAPI_TOKEN= python3 main.py -c ` ### Use Osintgram v2 (beta) You can use Osintgram2 beta just switching to `v2` [branch](https://github.com/Datalux/Osintgram/tree/v2). The v2 has some improvements and is faster with a new command execution interface. Try it just running `git checkout v2`.## Docker Quick Start ?This section will explain how you can quickly use this with `Docker` or `Docker-compose`. ### Prerequisites Before you can use either `Docker` or `Docker-compose`, please ensure you do have the following prerequisites met.1. **Docker** installed - [link](https://docs.docker.com/get-docker/) 2. **Docker-composed** installed (if using Docker-compose) - [link](https://docs.docker.com/compose/install/) 3. **Credentials** configured - This can be done manually or by running the `make setup` command from the root of this repo**Important**: Your container will fail if you do not do step #3 and configure your credentials### Docker If docker is installed you can build an and run this as a container.Build: bash docker build -t osintgram . Run: bash docker run --rm -it -v "$PWD/output:/home/osintgram/output" osintgram - The `` is the Instagram account you wish to use as your target for recon. - The required `-i` flag enables an interactive terminal to use commands within the container. [docs](https://docs.docker.com/engine/reference/commandline/run/#assign-name-and-allocate-pseudo-tty---name--it) - The required `-v` flag mounts a volume between your local filesystem and the container to save to the `./output/` folder. [docs](https://docs.docker.com/engine/reference/commandline/run/#mount-volume--v---read-only) - The optional `--rm` flag removes the container filesystem on completion to prevent cruft build-up. [docs](https://docs.docker.com/engine/reference/run/#clean-up---rm) - The optional `-t` flag allocates a pseudo-TTY which allows colored output. [docs](https://docs.docker.com/engine/reference/run/#foreground)### Using `docker-compose`You can use the `docker-compose.yml` file this single command: bash docker-compose run osintgram Where `target` is the Instagram target for recon.Alternatively, you may run `docker-compose` with the `Makefile`:`make run` - Builds and Runs with compose. Prompts for a `target` before running. ### Makefile (easy mode)For ease of use with Docker-compose, a `Makefile` has been provided.Here is a sample work flow to spin up a container and run `osintgram` with just two commands!1. `make setup` - Sets up your Instagram credentials 2. `make run` - Builds and Runs a osintgram container and prompts for a targetSample workflow for development:1. `make setup` - Sets up your Instagram credentials 2. `make build-run-testing` - Builds an Runs a container without invoking the `main.py` script. Useful for an `it` Docker session for development 3. `make cleanup-testing` - Cleans up the testing container created from `build-run-testing`## Development version ?To use the development version with the latest feature and fixes just switch to `development` branch using Git:`git checkout development`and update to last version using:`git pull origin development` ## Updating ⬇️To update Osintgram with the stable release just pull the latest commit using Git.1. Make sure you are in the master branch running: `git checkout master` 2. Download the latest version: `git pull origin master` ## Contributing ?You can propose a feature request opening an issue or a pull request.Here is a list of Osintgram's contributors: # # External library ?[Instagram API](https://github.com/ping/instagram_private_api) {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/Datalux/Osintgram](https://github.com/Datalux/Osintgram) ⭐ Star数:14305 ? 开发语言:Python ? 项目描述:Osintgram是Instagram上的OSINT工具。它提供了一个交互式外壳,可以通过其昵称对任何用户的Instagram帐户进行分析 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/Datalux/Osintgram/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/Datalux/Osintgram"}总的来说,**Osintgram**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
深度评测:web-check 这款工具到底怎么样 推荐一个实用的开源工具——web-check。项目由lissy93开发维护,GitHub上获得了 34690 个Star。简单来说,它是一款用于分析任何网站的一?️♂️体化OSINT工具,对于站长和开发者来说是个不错的工具。 工具功能介绍 Web-Check Comprehensive, on-demand open source intelligence for any website ? web-check.xyz---Kindly supported by: NinjaPear API to get a full B2B profiles from any URL Terminal Trove The $HOME of all things in the terminal Warp Built for coding with multiple AI agents About Screenshot Live Demo Mirror Features Usage Deployment Option#1: Netlify Option#2: Vercel Option#3: Docker Option#4: Render Option#5: Source Configuration Options Developer Setup Community Contributing Bugs Support License--- About Get an insight into the inner-workings of a given website: uncover potential attack vectors, analyse server architecture, view security configurations, and learn what technologies a site is using.Currently the dashboard will show: IP info, SSL chain, DNS records, cookies, headers, domain info, search crawl rules, page map, server location, redirect ledger, open ports, traceroute, DNS security extensions, site performance, trackers, associated hostnames, carbon footprint. Stay tuned, as I'll add more soon!The aim is to help you easily understand, optimize and secure your website. Screenshot Expand ScreenshotScreenshotScreenshot Live DemoA hosted version can be accessed at: web-check.as93.net Mirror The source for this repo is mirrored to CodeBerg, available at: codeberg.org/alicia/web-check Status Build & Deploys: Repo Management & Miscellaneous: Features Click to expand / collapse sectionNote _this list needs updating, many more jobs have been added since..._The following section outlines the core features, and briefly explains why this data might be useful for you to know, as well as linking to further resources for learning more. IP Info Description An IP address (Internet Protocol address) is a numerical label assigned to each device connected to a network / the internet. The IP associated with a given domain can be found by querying the Domain Name System (DNS) for the domain's A (address) record. Use CasesFinding the IP of a given server is the first step to conducting further investigations, as it allows us to probe the server for additional info. Including creating a detailed map of a target's network infrastructure, pinpointing the physical location of a server, identifying the hosting service, and even discovering other domains that are hosted on the same IP address. Useful Links- Understanding IP Addresses IP Addresses - Wiki RFC-791 Internet Protocol whatismyipaddress.com SSL Chain DescriptionSSL certificates are digital certificates that authenticate the identity of a website or server, enable secure encrypted communication (HTTPS), and establish trust between clients and servers. A valid SSL certificate is required for a website to be able to use the HTTPS protocol, and encrypt user + site data in transit. SSL certificates are issued by Certificate Authorities (CAs), which are trusted third parties that verify the identity and legitimacy of the certificate holder. Use CasesSSL certificates not only provide the assurance that data transmission to and from the website is secure, but they also provide valuable OSINT data. Information from an SSL certificate can include the issuing authority, the domain name, its validity period, and sometimes even organization details. This can be useful for verifying the authenticity of a website, understanding its security setup, or even for discovering associated subdomains or other services. Useful Links- TLS - Wiki What is SSL (via Cloudflare learning) RFC-8446 - TLS SSL Checker DNS Records Description This task involves looking up the DNS records associated with a specific domain. DNS is a system that translates human-readable domain names into IP addresses that computers use to communicate. Various types of DNS records exist, including A (address), MX (mail exchange), NS (name server), CNAME (canonical name), and TXT (text), among others. Use CasesExtracting DNS records can provide a wealth of information in an OSINT investigation. For example, A and AAAA records can disclose IP addresses associated with a domain, potentially revealing the location of servers. MX records can give clues about a domain's email provider. TXT records are often used for various administrative purposes and can sometimes inadvertently leak internal information. Understanding a domain's DNS setup can also be useful in understanding how its online infrastructure is built and managed. Useful Links- What are DNS records? (via Cloudflare learning) DNS Record Types RFC-1035 - DNS DNS Lookup (via MxToolbox) Cookies Description The Cookies task involves examining the HTTP cookies set by the target website. Cookies are small pieces of data stored on the user's computer by the web browser while browsing a website. They hold a modest amount of data specific to a particular client and website, such as site preferences, the state of the user's session, or tracking information. Use CasesCookies can disclose information about how the website tracks and interacts with its users. For instance, session cookies can reveal how user sessions are managed, and tracking cookies can hint at what kind of tracking or analytics frameworks are being used. Additionally, examining cookie policies and practices can offer insights into the site's security settings and compliance with privacy regulations. Useful Links- HTTP Cookie Docs (Mozilla) What are Cookies (via Cloudflare Learning) Testing for Cookie Attributes (OWASP) RFC-6265 - Cookies Crawl Rules Description Robots.txt is a file found (usually) at the root of a domain, and is used to implement the Robots Exclusion Protocol (REP) to indicate which pages should be ignored by which crawlers and bots. It's good practice to avoid search engine crawlers from over-loading your site, but should not be used to keep pages out of search results (use the noindex meta tag or header instead). Use CasesIt's often useful to check the robots.txt file during an investigation, as it can sometimes disclose the directories and pages that the site owner doesn't want to be indexed, potentially because they contain sensitive information, or reveal the existence of otherwise hidden or unlinked directories. Additionally, understanding crawl rules may offer insights into a website's SEO strategies. Useful Links- Google Search Docs - Robots.txt Learn about robots.txt (via Moz.com) RFC-9309 - Robots Exclusion Protocol Robots.txt - wiki Headers Description The Headers task involves extracting and interpreting the HTTP headers sent by the target website during the request-response cycle. HTTP headers are key-value pairs sent at the start of an HTTP response, or before the actual data. Headers contain important directives for how to handle the data being transferred, including cache policies, content types, encoding, server information, security policies, and more. Use CasesAnalyzing HTTP headers can provide significant insights in an OSINT investigation. Headers can reveal specific server configurations, chosen technologies, caching directives, and various security settings. This information can help to determine a website's underlying technology stack, server-side security measures, potential vulnerabilities, and general operational practices. Useful Links- HTTP Headers - Docs RFC-7231 Section 7 - Headers List of header response fields OWASP Secure Headers Project Quality Metrics Description Using Lighthouse, the Quality Metrics task measures the performance, accessibility, best practices, and SEO of the target website. This returns a simple checklist of 100 core metrics, along with a score for each category, to gauge the overall quality of a given site. Use CasesUseful for assessing a site's technical health, SEO issues, identify vulnerabilities, and ensure compliance with standards. Useful Links- Lighthouse Docs Google Page Speed Tools W3 Accessibility Tools Google Search Console SEO Checker PWA Builder Server Location Description The Server Location task determines the physical location of the server hosting a given website based on its IP address. This is done by looking up the IP in a location database, which maps the IP to a lat + long of known data centers and ISPs. From the latitude and longitude, it's then possible to show additional contextual info, like a pin on the map, along with address, flag, time zone, currency, etc. Use CasesKnowing the server location is a good first step in better understanding a website. For site owners this aids in optimizing content delivery, ensuring compliance with data residency requirements, and identifying potential latency issues that may impact user experience in specific geographical regions. And for security researchers, it helps assess the risk posed by specific regions or jurisdictions regarding cyber threats and regulations. Useful Links- IP Locator Internet Geolocation - Wiki Associated Hosts Description This task involves identifying and listing all domains and subdomains (hostnames) that are associated with the website's primary domain. This process often involves DNS enumeration to discover any linked domains and hostnames, as well as looking at known DNS records. Use CasesDuring an investigation, understanding the full scope of a target's web presence is critical. Associated domains could lead to uncovering related projects, backup sites, development/test sites, or services linked to the main site. These can sometimes provide additional information or potential security vulnerabilities. A comprehensive list of associated domains and hostnames can also give an overview of the organization's structure and online footprint. Useful Links- DNS Enumeration - Wiki OWASP - Enumerate Applications on Webserver DNS Enumeration - DNS Dumpster Subdomain Finder Redirect Chain Description This task traces the sequence of HTTP redirects that occur from the original URL to the final destination URL. An HTTP redirect is a response with a status code that advises the client to go to another URL. Redirects can occur for several reasons, such as URL normalization (directing to the www version of the site), enforcing HTTPS, URL shorteners, or forwarding users to a new site location. Use CasesUnderstanding the redirect chain can be useful for several reasons. From a security perspective, long or complicated redirect chains can be a sign of potential security risks, such as unencrypted redirects in the chain. Additionally, redirects can impact website performance and SEO, as each redirect introduces additional round-trip-time (RTT). For OSINT, understanding the redirect chain can help identify relationships between different domains or reveal the use of certain technologies or hosting providers. Useful Links- HTTP Redirects - MDN URL Redirection - Wiki 301 Redirects explained TXT Records DescriptionTXT records are a type of DNS record that provides text information to sources outside your domain. They can be used for a variety of purposes, such as verifying domain ownership, ensuring email security, and even preventing unauthorized changes to your website. Use CasesThe TXT records often reveal which external services and technologies are being used with a given domain. They may reveal details about the domain's email configuration, the use of specific services like Google Workspace or Microsoft 365, or security measures in place such as SPF and DKIM. Understanding these details can give an insight into the technologies used by the organization, their email security practices, and potential vulnerabilities. Useful Links- TXT Records (via Cloudflare Learning) TXT Records - Wiki RFC-1464 - TXT Records TXT Record Lookup (via MxToolbox) Server Status Description Checks if a server is online and responding to requests... {card-default label="? 工具信息" /} ? 项目地址:https://github.com/lissy93/web-check ⭐ Star数:34690 ? 开发语言:TypeScript ? 项目描述:用于分析任何网站的一?️♂️体化OSINT工具 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/lissy93/web-check/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/lissy93/web-check"} 总的来说,web-check是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
安全圈热门工具 sqlmap 体验分享 推荐一个实用的开源工具——sqlmap。项目由sqlmapproject开发维护,GitHub上获得了 38375 个Star。简单来说,它是一款自动SQL注入和数据库接管工具,对于站长和开发者来说是个不错的工具。 工具功能介绍 sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester, and a broad range of switches including database fingerprinting, over data fetching from the database, accessing the underlying file system, and executing commands on the operating system via out-of-band connections.Screenshots ----ScreenshotYou can visit the collection of screenshots demonstrating some of the features on the wiki.Installation ----You can download the latest tarball by clicking here or latest zipball by clicking here.Preferably, you can download sqlmap by cloning the Git repository:git clone --depth 1 https://github.com/sqlmapproject/sqlmap.git sqlmap-devsqlmap works out of the box with Python version 2.7 and 3.x on any platform.Usage ----To get a list of basic options and switches use:python sqlmap.py -hTo get a list of all options and switches use:python sqlmap.py -hhYou can find a sample run here. To get an overview of sqlmap capabilities, a list of supported features, and a description of all options and switches, along with examples, you are advised to consult the user's manual.Links ----* Homepage: https://sqlmap.org Download: .tar.gz or .zip Commits RSS feed: https://github.com/sqlmapproject/sqlmap/commits/master.atom Issue tracker: https://github.com/sqlmapproject/sqlmap/issues User's manual: https://github.com/sqlmapproject/sqlmap/wiki Frequently Asked Questions (FAQ): https://github.com/sqlmapproject/sqlmap/wiki/FAQ X: @sqlmap Demos: https://www.youtube.com/user/inquisb/videos Playground: https://sekumart.sekuripy.hr Research: https://www.sekuripy.hr/labs/sqlmap/#research Screenshots: https://github.com/sqlmapproject/sqlmap/wiki/ScreenshotsTranslations ----* Arabic Bengali Bulgarian Chinese Croatian Dutch French Georgian German Greek Hindi Indonesian Italian Japanese Korean Kurdish (Central) Persian Polish Portuguese Russian Serbian Slovak Spanish Turkish Ukrainian Vietnamese {card-default label="? 工具信息" /} ? 项目地址:https://github.com/sqlmapproject/sqlmap ⭐ Star数:38375 ? 开发语言:Python ? 项目描述:自动SQL注入和数据库接管工具 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/sqlmapproject/sqlmap/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/sqlmapproject/sqlmap"} 总的来说,sqlmap是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。