找到
3
篇与
白帽
相关的结果
-
 白帽SEO实战建站+算法+布局 2.png 课程介绍 目前课程共25课,建站+算法+外链+布局+误区讲解,全程没有多余的废话、只讲实用性技术,在这里,绝对没有一个知识点讲1小时的课程,每节课基本10-15分钟。 适合人群 1、网络公司或接单个人、网络公司没技术、只能代理、缺点就是代理死、网络公司也难活、逆冬这里可以直接给大家对接最真实、有效的资源。 2、传统行业老板、自己做项目、往往要的是精准的流量。如何降低成本、又能获取更多流量、这往往是项目负责人关心的事、面对许多网络公司忽悠、不作为、包括随便做一些垃圾词,企业老板应该具备识别能力! 3、在公司上班的打工族、现在SEO可谓是身兼多职、有时候要会PS、会写文章、还要参与新媒体运营、纠其原因、是因为本身能力有限、无法将关键词排名到首页、从而导致此种情况、提高自己、做某一专业、才是正道! 学习地址 百度:https://pan.baidu.com/s/1mqSc6-_u52F1mRC0PtV9fg 天翼:https://cloud.189.cn/t/QFnuAnRrmI7f(访问码:5vpv) 阿里:https://www.aliyundrive.com/s/k6c4x1zuthr 下载后请先检查文件完整性,如有问题请在评论区反馈

-
白帽黑客工具箱:routersploit 篇 推荐一个实用的开源工具——**routersploit**。项目由threat9开发维护,GitHub上获得了 **13240** 个Star。简单来说,它是一款嵌入式设备的利用框架,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 # Community Join community on [Embedded Exploitation Discord](https://discord.gg/UCXARN2vBx). # Description The RouterSploit Framework is an open-source exploitation framework dedicated to embedded devices.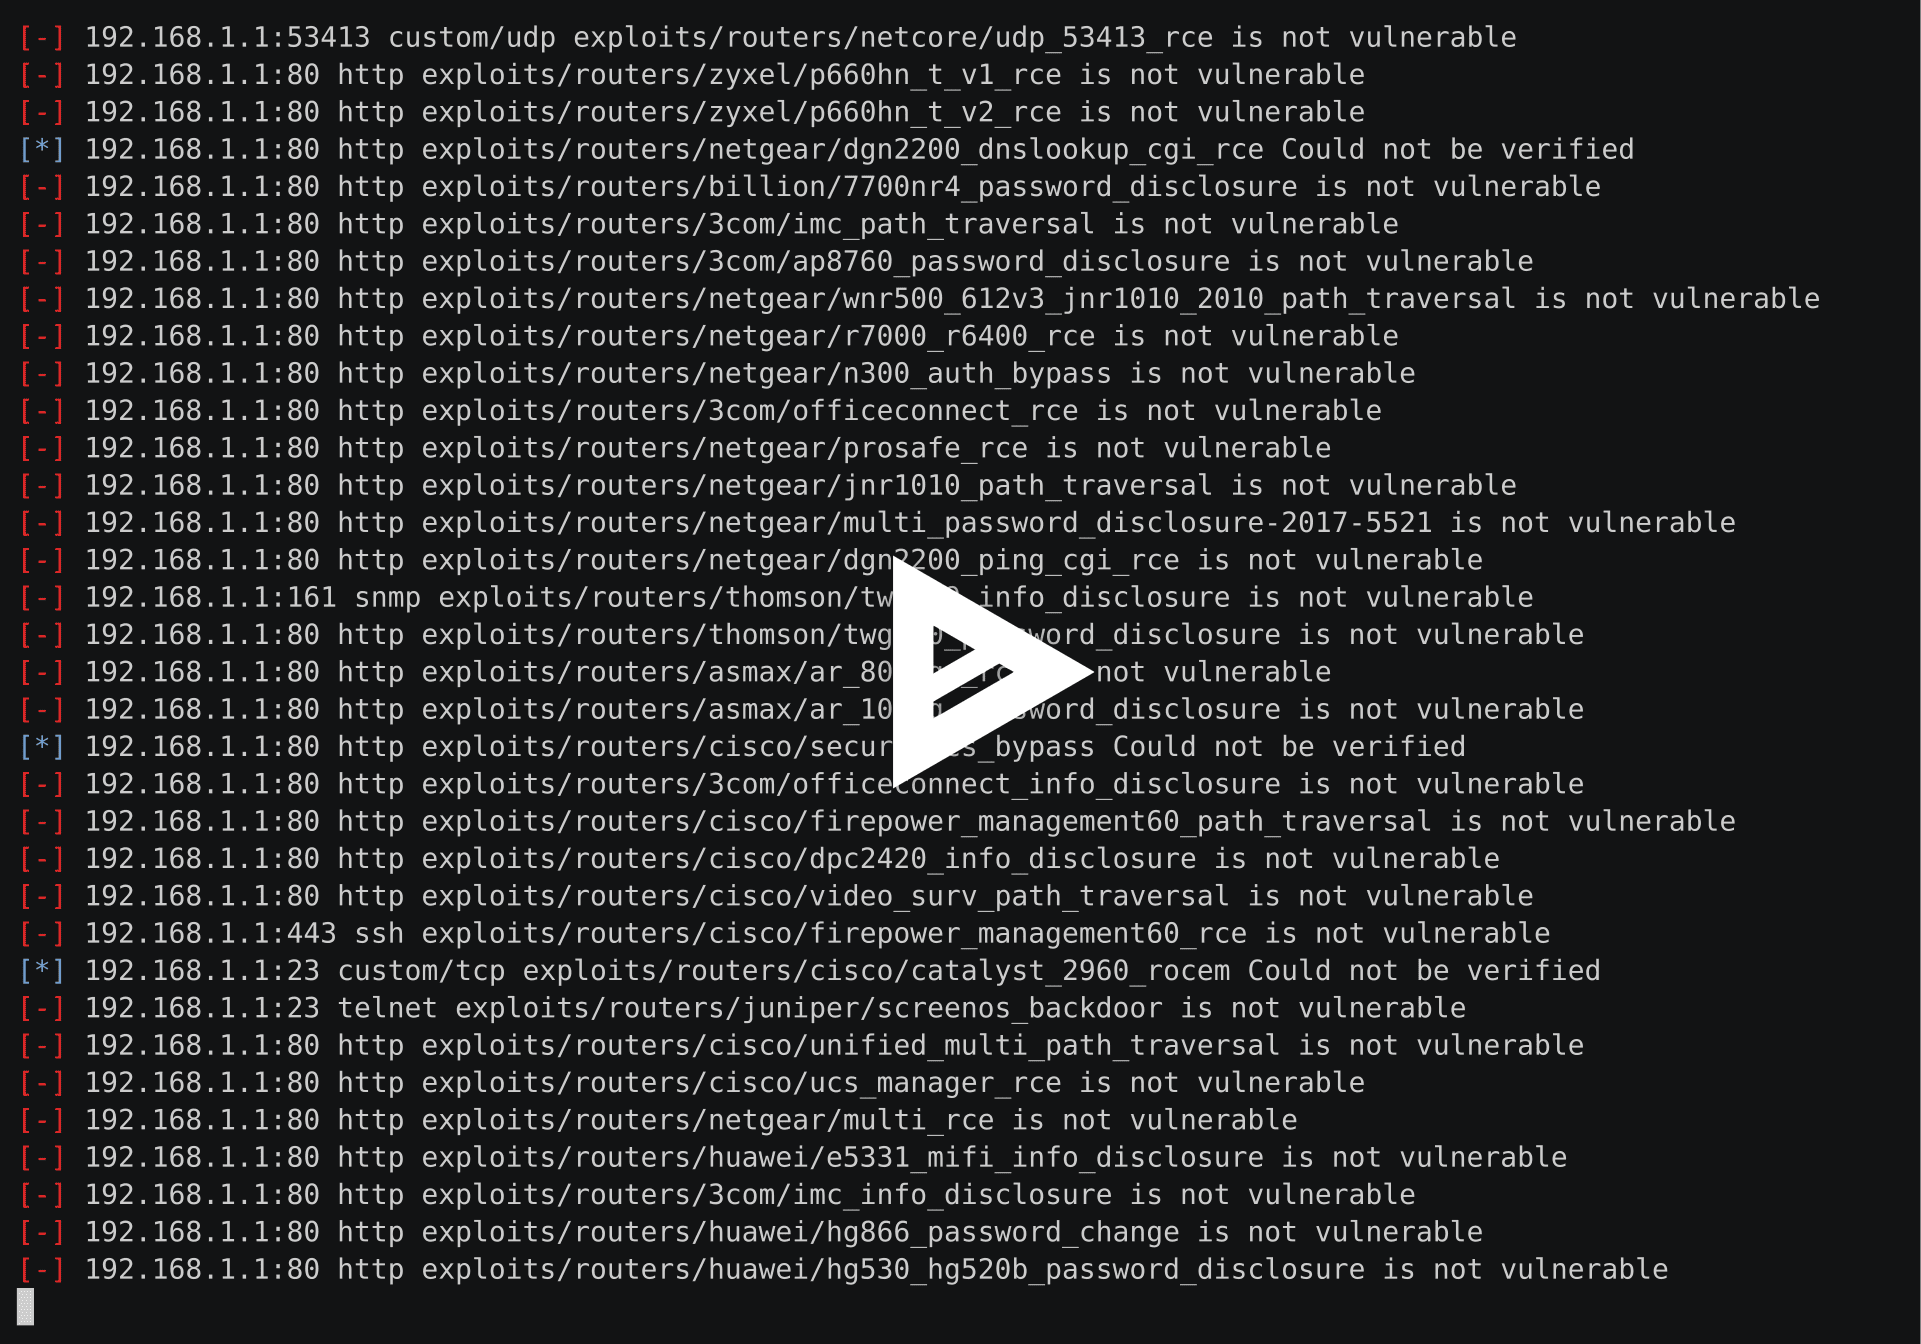It consists of various modules that aid penetration testing operations:* exploits - modules that take advantage of identified vulnerabilities * creds - modules designed to test credentials against network services * scanners - modules that check if a target is vulnerable to any exploit * payloads - modules that are responsible for generating payloads for various architectures and injection points * generic - modules that perform generic attacks# Installation ## Requirements Required: * requests * paramiko * pysnmp * pycryptoOptional: * bluepy - Bluetooth low energy## Installation on Kali Linux apt-get install python3-pip git clone https://www.github.com/threat9/routersploit cd routersploit python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on Ubuntu 20.04 sudo apt-get install git python3-pip git clone https://github.com/threat9/routersploit cd routersploit python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: sudo apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on Ubuntu 18.04 & 17.10 sudo add-apt-repository universe sudo apt-get install git python3-pip git clone https://www.github.com/threat9/routersploit cd routersploit python3 -m pip install setuptools python3 -m pip install -r requirements.txt python3 rsf.py Bluetooth Low Energy support: apt-get install libglib2.0-dev python3 -m pip install bluepy python3 rsf.py ## Installation on OSX git clone https://www.github.com/threat9/routersploit cd routersploit sudo python3 -m pip install -r requirements.txt python3 rsf.py ## Running on Docker git clone https://www.github.com/threat9/routersploit cd routersploit docker compose up --build -d docker attach routersploit # ## To run again without rebuild docker start routersploit docker attach routersploit # Update Update RouterSploit Framework often. The project is under heavy development and new modules are shipped almost every day. cd routersploit git pull # Build your own To our surprise, people started to fork [routersploit](https://github.com/threat9/routersploit) not because they were interested in the security of embedded devices but simply because they want to leverage our interactive shell logic and build their tools using similar concept. All these years they must have said: _"There must be a better way!"_ and they were completely right, the better way is called [_Riposte_](https://github.com/fwkz/riposte).[_Riposte_](https://github.com/fwkz/riposte) allows you to easily wrap your application inside a tailored interactive shell. Common chores regarding building REPLs was factored out and being taken care of so you can focus on specific domain logic of your application.# License The RouterSploit Framework is under a BSD license. Please see [LICENSE](LICENSE) for more details. # Acknowledgments * [riposte](https://github.com/fwkz/riposte) {card-default label="📦 工具信息" /} 🔗 项目地址:[https://github.com/threat9/routersploit](https://github.com/threat9/routersploit) ⭐ Star数:13240 💻 开发语言:Python 📝 项目描述:嵌入式设备的利用框架 {/card-default} 总的来说,**routersploit**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
白帽黑客工具箱:xmrig 篇 推荐一个实用的开源工具——xmrig。项目由xmrig开发维护,GitHub上获得了 10114 个Star。简单来说,它是一款RandomX、KawPow、CryptoNight和GhostRider统一CPU/GPU矿机和RandomX基准测试,对于站长和开发者来说是个不错的工具。 工具功能介绍 XMRig is a high performance, open source, cross platform RandomX, KawPow, CryptoNight and GhostRider unified CPU/GPU miner and RandomX benchmark. Official binaries are available for Windows, Linux, macOS and FreeBSD. Mining backends CPU (x86/x64/ARMv7/ARMv8/RISC-V) OpenCL for AMD GPUs. CUDA for NVIDIA GPUs via external CUDA plugin. Download Binary releases Build from source Usage The preferred way to configure the miner is the JSON config file as it is more flexible and human friendly. The command line interface does not cover all features, such as mining profiles for different algorithms. Important options can be changed during runtime without miner restart by editing the config file or executing API calls.* Wizard helps you create initial configuration for the miner. Workers helps manage your miners via HTTP API. Donations Default donation 1% (1 minute in 100 minutes) can be increased via option donate-level or disabled in source code. XMR: 48edfHu7V9Z84YzzMa6fUueoELZ9ZRXq9VetWzYGzKt52XU5xvqgzYnDK9URnRoJMk1j8nLwEVsaSWJ4fhdUyZijBGUicoD Developers xmrig sech1 Contacts support@xmrig.com reddit twitter {card-default label="📦 工具信息" /} 🔗 项目地址:https://github.com/xmrig/xmrig ⭐ Star数:10114 💻 开发语言:C 📝 项目描述:RandomX、KawPow、CryptoNight和GhostRider统一CPU/GPU矿机和RandomX基准测试 {/card-default} 总的来说,xmrig是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。