找到 723 篇与 csd 相关的结果 - 第 34 页
-
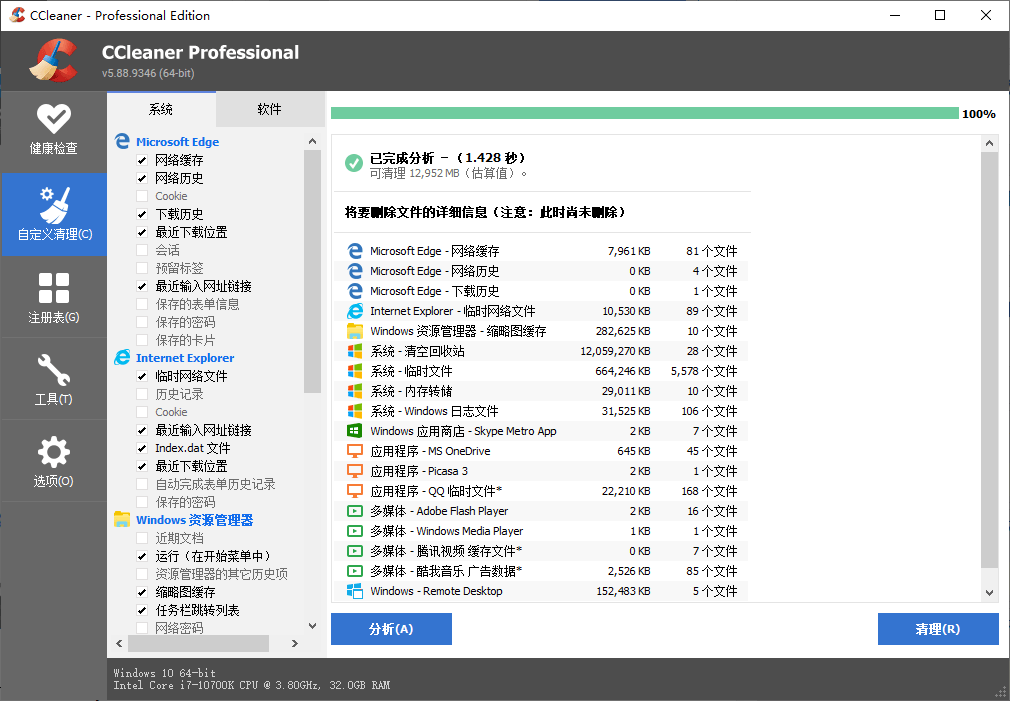
 CCleaner v7.11.1509中文专业版 软件介绍 CCleaner是一款免费的系统优化和隐私保护工具,它的体积小、扫描速度非常快,支持自定义清理规则,增强了应用程序清理范围和效果。CCleaner是Piriform(梨子公司)最著名广受好评的系统清理优化及隐私保护软件,也是该公司主打和首发产品,可以有效清除各种系统垃圾文件及应用程序垃圾,同时具备系统优化功能;可以对临时文件夹、历史记录、注册表冗余条目等进行垃圾清理,附带启动项管理、软件卸载功能。 软件CCleaner v7.11.1509中文专业版 图片2 CCleaner v7.11.1509中文专业版 图片4 更新日志 ccleaner.com/ccleaner/version-history 2026.09.03 v7.11.1509 修复部分用户无法完成新手引导流程的问题 CCleaner 7.0 新版特性 全新现代化界面:响应更快,操作更流畅。 多主题支持:提供浅色、深色及自动跟随系统三种主题模式。 扩展硬件支持:新增ARM64架构兼容,完美适配新一代设备。 全新的卸载引擎 → 能一次性卸载多个软件,避免弹窗,还能暂时删除测试性能,想恢复随时可以恢复! 磁盘分析器升级 → 分析大量重复文件,支持预览查看,删除方式更多样,界面全新设计支持深色模式! 云硬盘清理器 → 接管Google Drive和OneDrive,找重复文件、大文件、旧文件,快速查看释放空间! 性能优化功能 → 专利技术让PC提速34%,电池续航延长30%,游戏体验更流畅! 驱动更新功能 → 改善PC视觉效果、声音效果和网络连接,防止软件错误和崩溃! 软件更新功能 → 自动更新所有软件,在安全漏洞被发现前就清除,省时省力! 健康检查功能 → 全面分析PC,推荐快速修复方案,自动调整更新! 6.26 版本开始主界面「注册表」按钮已移至「工具」界面 补丁说明 安装“ccsetup_offline_setup.exe”运行 必须手动激活许可密钥:EGYPT-EGYPT-EGYPT-EGYPT-EGYPT 版本特点 by zdbryan 采用专业版安装版的主程序,集成注册码,将配置便携式保存 反汇编处理,实现INI配置文件便携化后也能使用智能清理功能 官方版开启便携不能使用智能清理功能,选项智能清理是灰色 禁止每次启动临时创建「谷歌检测Api接口模块」,加快启动速度! 禁止后台各种联网请求,提升启动速度,无网络情况下启动不卡顿 后台联网请求包括:发送匿名数据、检测许可密钥、检测升级提示 官方原版每次启动会后台偷偷联网请求avast安全中心上传匿名数据 移除界面右上角按钮:「帮助按钮」/「许可证管理」、底部:「检查更新」 调整并补充未翻译的简体中文字串,将中文语言移到程序内,删除其它多语言模块 预设选项:跳过UAC、关闭获取收集隐私数据和优惠信息、不启用智能清理功能等 取消原版内置规则默认勾选Edge/谷歌/火狐等浏览器Cookies项的钩子避免误清理 集成扫描规则:最新WinApp2规则 + 昔之光规则 (飞扬时空、slzyk | 孤雨 、lrxy) ⬇️ 下载地址 下载后请先检查文件完整性,如有问题请在评论区反馈

-
Wireshark 是什么?好用的工具软件推荐 推荐一个实用的开源工具——Wireshark。项目由Wireshark开发维护,采用未知开源协议发布。简单来说,它是一个,对于站长和开发者来说是个不错的工具。 工具功能介绍 介绍 {以下是码云平台说明,您可以替换此简介 码云是 OSCHINA 推出的基于 Git 的代码托管平台(同时支持 SVN)。专为开发者提供稳定、高效、安全的云端软件开发协作平台 无论是个人、团队、或是企业,都能够用码云实现代码托管、项目管理、协作开发。企业项目请看 https://gitee.com/enterprises} 软件架构 软件架构说明 安装教程 xxxx xxxx xxxx 使用说明 xxxx xxxx xxxx 参与贡献 Fork 本仓库 新建 Feat_xxx 分支 提交代码 新建 Pull Request 码云特技 使用 Readme\_XXX.md 来支持不同的语言,例如 Readme\_en.md, Readme\_zh.md 码云官方博客 blog.gitee.com 你可以 https://gitee.com/explore 这个地址来了解码云上的优秀开源项目 GVP 全称是码云最有价值开源项目,是码云综合评定出的优秀开源项目 码云官方提供的使用手册 https://gitee.com/help 码云封面人物是一档用来展示码云会员风采的栏目 https://gitee.com/gitee-stars/ 总的来说,Wireshark是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一个的解决方案,不妨下载试试。使用前建议仔细阅读项目文档。 {card-default label="? 工具信息" /} ? 工具名称:Wireshark ? 开发作者:Wireshark ? 工具描述: ? 开发语言:Java ? 开源协议:未知开源协议 ⭐ Star数:0 | ? Fork数:0 ? 更新时间:2020年12月19日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/Wireshark/Wireshark/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/Wireshark/Wireshark.git"}
-
免费开源开源工具推荐:setool-master 下载 今天给大家分享一款实用的开源工具——setool-master。这个工具在Gitee上获得了3个Star,主要功能是SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品,对于需要提高工作效率的朋友来说是个不错的选择。 工具功能介绍 SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品 你看过电影里面的黑客么,手指在键盘上不停的在打字,屏幕上运行的数不清的计算机命令, 没过一会儿,便可以入侵、盗取别人的计算机密码、 没错,Setool Master就是这样一款黑客工具,设计用于红队的社会工程学攻击。比起传统 的漏洞利用,社会工程学攻击会更加的高效和安全,而且对于使用者的门槛会非常低,入门 linux的也能快速掌握。使用python3开发,有更加良好的发展属性和可读性、运行效率 非常的高,设计用于对组织级别的攻击 绝对不要使用Setool Master去攻击一个你不认识的人,或者你可能会遇到许麻烦 你不能将这些源代码用于商业用途 本开源项目内包含第三方工具,在这里说说明:ngrok,seeker-master 本开源项目允许引用,但受到Apache2开源条约限制 作者:LinWinCloud 版本维护 安卓源代码版本 持续维护 v Linux安装包版本 部分维护 v 安卓编译版本 不再维护 X linux编译版本 不再维护 X 源代码 持续维护 V 安装教程 $ git clone https://github.com/LinWin-Cloud/setool-master $ cd setool-master $ pip3 install whois $ pip3 install requests 1.源代码版本、安卓源代码版本 $ cd resources_code_vistion (这个是源代码版本) 或者 cd Android_Resources_code $ python3 setool.py 2.Linux安装包版本 $ 7z x Setool-Master.7z $ cd Setool-Master $ cd Setool-Master $ python3 install_linux.py 软件将安装在/var/Setool-Master,环境请自行配置 3.编译版本、安卓编译版本 $ cd build_vistion(这个是编译版本) 或者 cd Termax_Android_vistion (这个是安卓编译版本) $ chmod +x ./setool $ bash ./setool 使用文档 使用文档(英文版本) 使用文档(中文版本) 注意 本工具集内Web Console密码linwin用户名linwin 更新日志 v1.0.0 2022.1.5 发布Setool Linux轻量个人版本 v2.1.1 2022.3.5 发布Setool Master源代码版本 v2.1.2 2022.3.5 发布Setool Master安装包版本 v2.1.3 2022.3.15 发布Setool Master预编译版本 v2.1.4 2022.4.1 更新配置文件、告示 v2.2.1 2022.5.1 修改部分源代码 v2.3.2 2022.5.4 修改配置文件 v2.4.1 2022.5.7 修改配置文件,更新版本信息 v2.4.2 2022.5.8 修改配置文件和源代码 v2.5.1 2022.5.15 发布安卓Termux编译版本 v2.5.2 2022.5.17 更新安卓Termux编译版本 v2.5.3 2022.5.19 更新部分源代码 v2.5.4 2022.5.28 发布安卓Termux源代码版本 v2.5.5 2022.5.29 更新版本信息、更新源代码 v2.5.6 2022.5.30 修复部分代码错误、更新部分配置文件 v2.5.7 2022.5.31 更新 Setool Master编译版本 版本信息、配置文件 v2.5.8 2022.6.2 更新配置、版本信息 v2.5.9 2022.6.6 更新源代码版本代码 v2.6.0 2022.6.7 创建使用文档文档 v2.6.1 2022.6.10 更新 使用文档(英文版本) v2.6.2 2022.6.11 更新版本信息、配置信息 v2.6.2 2022.6.12 更新配置文件 v2.6.3 2022.6.13 更新 安卓源代码版本 源代码 v2.6.4 2022.6.15 更新使用文档、配置文件 v2.6.5 2022.6.16 更新配置文件 v2.6.6 2022.6.20 更新源代码 v2.6.7 2022.6.21 更新英语文档,创建中文文档 v2.6.8 2022.6.22 更新配置文件 v2.6.9 2022.6.24 更新安卓源代码,更新配置文件 v2.7.0 2022.6.26 修复源代码错误,修复帮助和配置 v2.7.1 2022.6.28 更新版本信息、更新配置文件 v2.7.2 2022.6.30 更新配置文件 v2.7.3 2022.7.3 更新配置文件,修复源码错误 v2.7.4 2022.7.5 更新项目为Setool Master LTS长期支持版本 v2.7.5 2022.7.6 更新源代码、修复IO操作漏洞 v2.7.6 2022.7.13 更新配置文件 v2.7.7 2022.7.22 更新配置文件,说明 v2.7.8 2022.7.23 更新中文帮助、更新配置文件 v2.7.9 2022.8.9 更新配置文件 v2.8.0 2022.8.31 更新配置文件、修复错误 v2.8.1 2022.9.12 修改文档 v2.8.2 2022.9.16 删除了Linux编译版本,不再维护此版本、修改了源代码、修改了说明文件 v2.8.3 2022.10.15 删除了部分无用文件、更新文档 About Setool Master is a open resources social enginnering tools for linux.android(termux). It is free.You do not pay some money for these tools. Setool Master use Python Code language.It is very easy and funny.You can use these resources code to make a new tools and so on.If you want to get Setool-Master,you can goto https://github.com/LinWin-Cloud/setool-master. https://gitee.com/LinWin-CLoud/setool-master Setool Master是一个适用于Linux、Android(termux)的开源的社会工程学 工具。它是免费的。你不需要为这些工具支付费用。Setool Master使用Python 编程语言。非常简单并且有趣,你能用这些源代码去创造一个新的工具等等。如果你 想获取SetoolMaster,你能够访问 https://github.com/LinWin-Cloud/setool-master. https://gitee.com/LinWin-CLoud/setool-master 该项目会持续维护,吸收大家的建议 项目维护真的不容易,开源项目不赚钱,本项目将保证永远也不进行商业收费 真心希望屏幕前面的你能够给开发者一些动力来维护更新这更好的项目 综合来看,setool-master在同类工具中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。 {card-default label="? 工具信息" /} ? 工具名称:setool-master ? 开发作者:LinWin-Cloud ? 工具描述:SetoolMaster是一款让你入门即入狱的python3开发的进阶型社会工程学工具。包括了全球定位、Ngrok内网穿透、Seeker高精度定位、网页钓鱼、病毒攻击、恐吓勒索信、爬虫、网站克隆、物联网设备搜索等,同时拥有中文支持,内置大量钓鱼模板,设计用于组织级别红队渗透测试,用于团队组织设备型协同,经过非常多的实战演练,效果出众,远超同行产品 ? 开发语言:Python ? 开源协议:未知开源协议 ⭐ Star数:3 | ? Fork数:0 ? 更新时间:2025年06月18日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/LinWin-Cloud/setool-master/repository/archive/main.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/LinWin-Cloud/setool-master.git"}
-
strix - 一款实用的开源工具 推荐一个实用的开源工具——**strix**。项目由usestrix开发维护,GitHub上获得了 **61007** 个Star。简单来说,它是一款开源人工智能渗透测试工具,用于查找和修复应用程序的漏洞。,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 ### The open-source AI pentesting tool. Autonomous AI hackers that find and fix your app’s vulnerabilities. > [!TIP] > **New!** Strix integrates seamlessly with GitHub Actions and CI/CD pipelines. Automatically scan for vulnerabilities on every pull request and block insecure code before it reaches production - [Get started with no setup required](https://app.strix.ai?utm_source=github&utm_medium=readme&utm_content=tip_ci).---## Strix OverviewStrix are autonomous AI penetration testing agents that act just like real hackers - they run your code dynamically, find vulnerabilities, and validate them through actual proofs-of-concept. Built for developers and security teams who need fast, accurate security testing without the overhead of manual pentesting or the false positives of static analysis tools.**Key Capabilities:**- **Full pentesting toolkit** - reconnaissance, exploitation, and validation out of the box - **Multi-agent orchestration** - teams of AI pentesters that collaborate and scale - **Real exploit validation** - working PoCs, not false positives like legacy vulnerability scanners - **Developer‑first CLI** - actionable findings with remediation guidance - **Auto‑fix & reporting** - generate patches and compliance-ready pentest reports# # Use Cases- **Application Security Testing** - Detect and validate critical vulnerabilities in your applications - **Rapid Penetration Testing** - Get penetration tests done in hours, not weeks, with compliance reports - **Bug Bounty Automation** - Automate bug bounty research and generate PoCs for faster reporting - **CI/CD Integration** - Run tests in CI/CD to block vulnerabilities before reaching production## ? Quick Start**Prerequisites:** - Docker (running) - An LLM API key from any [supported provider](https://docs.strix.ai/llm-providers/overview) (OpenAI, Anthro, Google, etc.)### Installation & First Scan bash # Install Strix curl -sSL https://strix.ai/install | bash # Configure your AI provider export STRIX_LLM="openrouter/z-ai/glm-5.3" export LLM_API_KEY="your-api-key" # Run your first security assessment strix --target ./app-directory > [!NOTE] > First run automatically pulls the sandbox Docker . Results are saved to `strix_runs/`---## Ways to Run Strix- **Open Source** - free, runs locally with Docker and your own LLM key. [Quick Start](https://docs.strix.ai/quickstart) - **Strix Cloud** - no setup, validated findings, one-click autofix, and PR reviews. [Run a pentest →](https://app.strix.ai?intent=pentest&utm_source=github&utm_medium=readme&utm_content=table_cloud) - **Enterprise** - SSO, compliance-ready reports, VPC or self-hosted deployment. [Try Strix Enterprise →](https://strix.ai/demo?utm_source=github&utm_medium=readme&utm_content=table_demo)---## ☁️ Strix CloudTry the Strix full-stack penetration testing platform at **[app.strix.ai](https://app.strix.ai?utm_source=github&utm_medium=readme&utm_content=cloud_heading)** - sign up for free, connect your repos and domains, and launch a pentest in minutes.- **Validated findings with PoCs** - every vulnerability includes a working proof-of-concept exploit and reproduction steps - **One-click autofix** - AI-generated security patches as ready-to-merge pull requests - **Continuous pentesting** - always-on vulnerability scanning that keeps pace with your deployments - **DevSecOps integrations** - GitHub, GitLab, Bitbucket, Slack, Jira, Linear, and CI/CD pipelines - **Continuous learning** - AI that builds on past findings, adapts to your codebase, and reduces false positives over time[**Run a pentest →**](https://app.strix.ai?intent=pentest&utm_source=github&utm_medium=readme&utm_content=cloud_cta)## ? EnterpriseGet the same Strix experience with enterprise-grade controls: SSO (SAML/OIDC), custom compliance-ready penetration testing reports (SOC 2, ISO 27001, PCI DSS), dedicated support and SLA, custom deployment options (VPC or self-hosted), BYOK model support, and tailored AI pentesting agents optimized for your environment.[**Try Strix Enterprise →**](https://strix.ai/demo?utm_source=github&utm_medium=readme&utm_content=enterprise_cta)--- ## ? Use Strix from Your Coding AgentStrix is agent-ready. Give Claude Code, Cursor, Codex, or any [SKILL.md-compatible](https://agentskills.io) agent the ability to run pentests, fix findings, and set up CI scanning: bash npx skills add usestrix/strix This installs nine skills for running pentests, fixing findings, and CI scanning, against code, web apps, APIs, and the OWASP Top 10. Agents can use the local CLI or the managed cloud with the same engine.See [`AGENTS.md`](AGENTS.md) for the quick reference, [docs.strix.ai/llms.txt](https://docs.strix.ai/llms.txt) for the CLI, and [docs.app.strix.ai](https://docs.app.strix.ai) for the API.--- ## ✨ Features ### Agentic Pentesting ToolsStrix agents come equipped with a comprehensive offensive security toolkit - the same tools used by professional penetration testers and ethical hackers:- **HTTP Interception Proxy** - Full request/response manipulation and analysis with Caido - **Browser Exploitation** - Automated browser for testing XSS, CSRF, clickjacking, and auth bypass flows - **Shell & Command Execution** - Interactive terminal for exploit development and post-exploitation - **Custom Exploit Runtime** - Python sandbox for writing and validating proof-of-concept exploits - **Reconnaissance & OSINT** - Automated attack surface mapping, subdomain enumeration, and fingerprinting - **Static & Dynamic Code Analysis** - SAST + DAST capabilities for comprehensive application security testing - **Vulnerability Knowledge Base** - Structured findings with CVSS scoring and OWASP classification### Comprehensive Vulnerability ScannerStrix identifies, validates, and exploits a wide range of security vulnerabilities across the OWASP Top 10 and beyond:- **Broken Access Control** - IDOR, privilege escalation, auth bypass - **Injection Attacks** - SQL injection, NoSQL injection, OS command injection, SSTI - **Server-Side Vulnerabilities** - SSRF, XXE, insecure deserialization, RCE - **Client-Side Attacks** - XSS (stored/reflected/DOM), prototype pollution, CSRF - **Business Logic Flaws** - Race conditions, payment manipulation, workflow bypass - **Authentication & Session** - JWT attacks, session fixation, credential stuffing vectors - **Infrastructure & Cloud** - Misconfigurations, exposed services, cloud security issues - **API Security** - Broken authentication, mass assignment, rate limiting bypass### Graph of Agents (Multi-Agent Pentesting)Advanced multi-agent orchestration for comprehensive automated penetration testing:- **Distributed Pentesting** - Specialized AI agents for recon, exploitation, and post-exploitation - **Scalable Security Testing** - Parallel execution across multiple targets for fast, comprehensive coverage - **Dynamic Coordination** - Agents share discoveries, chain vulnerabilities, and collaborate like a red team---## ?️ Local Web ViewerEvery scan writes its results to disk as it runs. Bring them up in a local dashboard with a single command: bash # Open the most recent run strix view # ...or open a specific run by name strix view my-run-name # Expose the viewer on all IPv4 interfaces at a fixed port strix view --host 0.0.0.0 --port 8080 --no-open The dashboard shows the findings, a live map of the agent team, and past runs. Nothing leaves your machine, and the UI ships prebuilt. `strix view` binds to `127.0.0.1` and prints a tokened link that grants access to the run, so share it carefully.See the [viewer documentation](https://docs.strix.ai/usage/viewer) for the options and for reaching the viewer from another machine.--- ## Usage Examples ### Basic Usage bash # Scan a local codebase strix --target ./app-directory # Security review of a GitHub repository strix --target https://github.com/org/repo # Black-box web application assessment strix --target https://your-app.com ### API Testing (OpenAPI / Swagger / Postman)Point Strix at an API contract and it tests every declared endpoint instead of having to discover them by crawling. Pair the spec with the live base URL so the agent knows where to send traffic: bash # OpenAPI / Swagger file, Postman export, or a live collection by id strix --target ./openapi.yaml --target https://api.your-app.com strix --target postman:// --target https://api.your-app.com ### Advanced Testing Scenarios bash # Grey-box authenticated testing strix --target https://your-app.com --instruction "Perform authenticated testing using credentials: user:pass" # Multi-target testing (source code + deployed app) strix -t https://github.com/org/app -t https://your-app.com # Targets from a file, one target per non-empty, non-comment line strix --target-list ./targets.txt See the [CLI reference](https://docs.strix.ai/usage/cli) for every option, including scan modes, diff scope, instruction files, and budgets. ### Headless ModeRun Strix programmatically without interactive UI using the `-n/--non-interactive` flag - perfect for servers and automated jobs. The CLI prints real-time vulnerability findings and the final report before exiting. Exits with non-zero code when vulnerabilities are found. bash strix -n --target https://your-app.com ### CI/CD (GitHub Actions)Strix can be added to your pipeline to run a security test on pull requests with a lightweight GitHub Actions workflow: yaml name: strix-penetration-teston: pull_request:jobs: security-scan: runs-on: ubuntu-latest steps: - uses: actions/checkout@v6 with: fetch-depth: 0- name: Install Strix run: curl -sSL https://strix.ai/install | bash- name: Run Strix env: STRIX_LLM: ${{ secrets.STRIX_LLM }} LLM_API_KEY: ${{ secrets.LLM_API_KEY }}run: strix -n -t ./ --scan-mode quick > [!TIP] > In CI pull request runs, Strix automatically scopes quick reviews to changed files, which is why the > checkout above fetches full history. See the > [CI/CD documentation](https://docs.strix.ai/integrations/github-actions) for the details.### Configuration bash export STRIX_LLM="openrouter/z-ai/glm-5.3" export LLM_API_KEY="your-api-key" # Optional export LLM_API_BASE="your-api-base-url" # if using a local model, e.g. Ollama, LMStudio > [!NOTE] > Strix automatically saves your configuration to `~/.strix/cli-config.json`, so you don't have to re-enter it on every run. > See the [configuration reference](https://docs.strix.ai/advanced/configuration) for every environment variable.#### Sign in with a ChatGPT subscriptionInstead of a metered API key, you can run Strix on your ChatGPT Plus/Pro subscription: bash strix auth login chatgpt # sign in with your ChatGPT account export STRIX_LLM="chatgpt/gpt-5.4" # chatgpt/ runs on the subscription strix auth status # show the active sign-in, or logout to forget it #### Use the managed platform: `strix cloud`Run scans on [app.strix.ai](https://app.strix.ai) from the terminal, without Docker or an LLM key: bash strix cloud login # browser sign-in, one credential per install strix cloud scans start --source . --yes --wait # scan local code, approving the upload strix cloud scans start --engagement-type live_test --domain-ids --wait strix cloud vulns list --severity critical Every [REST API](https://docs.app.strix.ai) operation has a matching `strix cloud ` command. Run `strix cloud` to list the resources, and add `help` to a resource to list its verbs. Output is JSON when stdout is not a terminal or when you pass `--json`. Binary downloads are the exception: redirect the raw bytes, or combine `--output FILE --json` for download metadata.See the [cloud CLI documentation](https://docs.strix.ai/cloud/cli) for scopes, workspaces, billing, and source-upload options. #### Connect your own MCP serversStrix can connect to Model Context Protocol (MCP) servers you list and expose their tools to the agent during a run. Create `~/.strix/mcp-servers.json` with a JSON list of local `stdio` servers or remote `http` servers: json [ { "name": "github", "transport": "http", "url": "https://api.githubcopilot.com/mcp/", "auth": { "kind": "bearer", "token": "your-token" }, "allowed_tools": ["list_issues"] } ] Each server's tools are namespaced by `name`, for example `github_list_issues`. See the [MCP documentation](https://docs.strix.ai/integrations/mcp) for the full schema, tool filtering, and `stdio` servers.**Recommended models for best results:**- [Z.ai GLM-5.3 on OpenRouter](https://openrouter.ai/z-ai/glm-5.3) - `openrouter/z-ai/glm-5.3` (the default k) - [OpenAI GPT-5.4](https://openai.com/api/) - `openai/gpt-5.4` - [AnthroClaude Sonnet 4.6](https://claude.com/platform/api) - `anthro/claude-sonnet-4-6` - [Google Gemini 3 Pro Preview](https://cloud.google.com/vertex-ai) - `vertex_ai/gemini-3-pro-preview` - [DeepSeek V4 Pro](https://platform.deepseek.com) - `deepseek/deepseek-v4-pro` - [Moonshot Kimi K3](https://platform.kimi.ai) - `moonshot/kimi-k3`See the [LLM Providers documentation](https://docs.strix.ai/llm-providers/overview) for all supported providers including Vertex AI, Bedrock, Azure, and local models.## Documentation Full documentation is available at **[docs.strix.ai](https://docs.strix.ai)** - including detailed guides for usage, CI/CD integrations, skills, and advanced configuration. ## Contributing We welcome contributions of code, docs, and new skills - check out our [Contributing Guide](https://docs.strix.ai/contributing) to get started or open a [pull request](https://github.com/usestrix/strix/pulls)/[issue](https://github.com/usestrix/strix/issues). ## Join Our CommunityHave questions? Found a bug? Want to contribute? **[Join our Discord!](https://discord.gg/strix-ai)** ## Support the Project**Love Strix?** Give us a ⭐ on GitHub! ## Acknowledgements Strix builds on the incredible work of open-source projects like [LiteLLM](https://github.com/BerriAI/litellm), [Caido](https://github.com/caido/caido), [Nuclei](https://github.com/projectdiscovery/nuclei), [Playwright](https://github.com/microsoft/playwright), and [Bubble Tea](https://github.com/charmbracelet/bubbletea). Huge thanks to their maintainers!> [!WARNING] > **Authorized use only.** Strix actively tests the targets you point it at, so only run it against systems you own or have **explicit, written permission** to test, and stay within the agreed scope. Unauthorized testing is illegal in most jurisdictions. > You alone are responsible for obtaining authorization and complying with the law. Strix is provided "as is" with no warranty or liability for misuse.{card-default label="? 工具信息" /} ? 项目地址:[https://github.com/usestrix/strix](https://github.com/usestrix/strix) ⭐ Star数:61007 ? 开发语言:Python ? 项目描述:开源人工智能渗透测试工具,用于查找和修复应用程序的漏洞。 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/usestrix/strix/archive/refs/heads/main.zip"} {cloud type="default" title="网盘下载" url="https://github.com/usestrix/strix"}总的来说,**strix**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
DiscuzQ 开源项目下载 - 基于PHP的开源网站系统 DiscuzQ 今天给大家分享一款基于PHP开发的开源项目——DiscuzQ。这个项目在Gitee上获得了431个Star,240次Fork,说明还是有不少开发者在使用和关注的。项目主要特点是【React版 后台】Discuz! Q是一套跨端全域的社区工具,是平行于Discuz! X系列的另一条产品线,Discuz! Q的目标是帮助流量大V、网红、知识付费、,适合需要快速搭建网站的开发者和站长使用。 项目功能介绍 关于 Discuz! Q Discuz Q 社区 安装方法 服务器环境需求为: PHP 7.2.5+ 和 MySQL 5.7+。 第一步:下载 Discuz! Q 首先注册腾讯云帐号 并 实名认证, 然后在 API密钥管理 处新建一个密钥 Discuz!Q 源码归类 【后台管理下载】https://gitee.com/Discuz/Discuz-Q 【PC端+H5+小程序 前端下载】https://gitee.com/Discuz/discuz-fe 感谢 背景故事 Discuz! Q项目由于是从 0 到 1,介于我们的目标,如果从第一行代码开始编写,是极为庞大的工程。想想Discuz!X,代码量依赖 10 多年的时间的积累,才完善出各种工具类、自己的框架及插件机制等。 在此背景下,我们必须借助开源的力量,才得以快速构建出Discuz! Q。以下是整个Discuz! Q中所用到的技术栈,在此特别感谢他们: Discuz! Q 是更轻的,更易变现的,更移动端的,更开放的和更易于二次开发的社区产品。 Discuz! Q 是一套跨端全域的社区工具,内置六大能力:用户能力、内容能力、支付能力、运营能力、通知能力、连接能力;可以设置公开、付费模式,发布包括图文、短、附件、话题、评论等内容形式;并支持知识变现,可以内容 以上就是关于DiscuzQ的简单介绍。这个项目的代码结构清晰,文档也比较完善,对于PHP初学者来说也是一个不错的学习资源。有兴趣的朋友可以通过下方链接下载源码体验一下。 {card-default label="? 项目信息" /} ? 项目名称:DiscuzQ ? 开发作者:Discuzx ? 项目描述:【React版 后台】Discuz! Q是一套跨端全域的社区工具,是平行于Discuz! X系列的另一条产品线,Discuz! Q的目标是帮助流量大V、网红、知识付费、 ? 开发语言:PHP ? 开源协议:未知开源协议 ⭐ Star数:431 | ? Fork数:240 ? 更新时间:2026年07月23日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/Discuz/Discuz-Q/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/Discuz/Discuz-Q.git"}
-
站长必备!hackingtool 效率神器分享 推荐一个实用的开源工具——**hackingtool**。项目由Z4nzu开发维护,GitHub上获得了 **79344** 个Star。简单来说,它是一款面向黑客的一体化黑客工具,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 **215 curated tools across 21 categories** — recon, OSINT, web, wireless, phishing, forensics, post-exploitation and more — with an **AI layer that turns plain English into the right tool and the exact command**.**Built for** penetration testers · red teamers · blue-team/SOC and DFIR analysts · OSINT researchers · bug-bounty hunters · CTF players · security researchers and students — all working **legally, on systems they own or are authorised to test**. ! ! ! ! ! ---## Contents- [Why hackingtool](#why-hackingtool) - [Tool Categories](#tool-categories) - [Installation](#installation) - [From source with pipx (recommended)](#from-source-with-pipx-recommended) - [For development](#for-development) - [Docker](#docker) - [Optional runtimes](#optional-runtimes) - [Quick Commands](#quick-commands) - [Command reference](#command-reference) - [Features](#features) - [? `/find` — a tool for a need you don't have yet](#-find--a-tool-for-a-need-you-dont-have-yet) - [? `/goal` — plan an objective, run it one step at a time](#-goal--plan-an-objective-run-it-one-step-at-a-time) - [? Recommendations — say what you want in plain English](#-recommendations--say-what-you-want-in-plain-english) - [? Tags and search](#-tags-and-search) - [▶ Background panes (tmux)](#-background-panes-tmux) - [⚙ Settings and the AI layer](#-settings-and-the-ai-layer) - [? Headless engagements](#-headless-engagements) - [Documentation](#documentation) - [Contributing](#contributing) - [Support & Sponsor](#support--sponsor) - [Social](#social)---## Why hackingtool- **? AI-guided workflow** — describe what you want ("find subdomains of example.com") and it maps your intent to the right tools, hands you the exact documented command, plans an objective step by step, then summarizes findings and drafts an engagement report. Bring your own key or run a local model — nothing auto-executes and nothing is fabricated. - **? 215 curated tools, one console** — install and run across 21 categories without hunting down Git repos; a fixed tag taxonomy (63 tags in use) makes every tool discoverable. - **? It knows what it doesn't have** — `/find` searches your catalog first, then the GitHub API, and shows real maintained projects with the reason each was ranked. - **? Safe by default** — standard installs, **no `curl | bash`**, downloads pinned + SHA-256 verified, list-form `subprocess`, no forced `sudo`, and [signed releases with an SBOM](SECURITY.md#verifying-a-release). - **? For the whole spectrum** — red team, blue team, OSINT, bug bounty, CTF/THM, forensics/IR — all on **authorized targets only**.The console on launch — live system readout, and / opens the command palette. ---## Tool Categories**215 tools across 21 categories** — the full list, with links and tags, is in **[docs/TOOLS.md](docs/TOOLS.md)**.| # | Category | Tools | | # | Category | Tools | |:---:|---|:---:|---|:---:|---|:---:| | 1 | ? [Anonymously Hiding Tools](docs/TOOLS.md#-anonymously-hiding-tools) | 5 | | 12 | ? [Reverse engineering tools](docs/TOOLS.md#-reverse-engineering-tools) | 10 | | 2 | ? [Information gathering tools](docs/TOOLS.md#-information-gathering-tools) | 26 | | 13 | ⚡ [DDOS Attack Tools](docs/TOOLS.md#-ddos-attack-tools) | 7 | | 3 | ? [Wordlist Generator](docs/TOOLS.md#-wordlist-generator) | 8 | | 14 | ? [Remote Administrator Tools (RAT)](docs/TOOLS.md#-remote-administrator-tools-rat) | 4 | | 4 | ? [Wireless attack tools](docs/TOOLS.md#-wireless-attack-tools) | 17 | | 15 | ? [XSS Attack Tools](docs/TOOLS.md#-xss-attack-tools) | 6 | | 5 | ? [SQL Injection Tools](docs/TOOLS.md#-sql-injection-tools) | 7 | | 16 | ? [Steganography Tools](docs/TOOLS.md#-steganography-tools) | 10 | | 6 | ? [Phishing attack tools](docs/TOOLS.md#-phishing-attack-tools) | 13 | | 17 | ? [Active Directory Tools](docs/TOOLS.md#-active-directory-tools) | 10 | | 7 | ? [Web Attack tools](docs/TOOLS.md#-web-attack-tools) | 23 | | 18 | ☁ [Cloud Security Tools](docs/TOOLS.md#-cloud-security-tools) | 7 | | 8 | ? [Post exploitation tools](docs/TOOLS.md#-post-exploitation-tools) | 15 | | 19 | ? [Mobile Security Tools](docs/TOOLS.md#-mobile-security-tools) | 6 | | 9 | ? [Forensic tools](docs/TOOLS.md#-forensic-tools) | 12 | | 20 | ✨ [Other tools](docs/TOOLS.md#-other-tools) | 10 | | 10 | ? [Payload creation tools](docs/TOOLS.md#-payload-creation-tools) | 6 | | 21 | ? [Password / Hash Cracking](docs/TOOLS.md#-password--hash-cracking) | 7 | | 11 | ? [Exploit framework](docs/TOOLS.md#-exploit-framework) | 6 | | | | |59 further entries are archived (unmaintained or dead upstream) and hidden unless you set `show_archived true` via `/config`. The in-app header counts 22 categories / 217 tools because it also counts the built-in Update / Uninstall menu.---## Installation Requires **Python 3.10+** on **Linux or macOS** (Kali, Parrot, Debian/Ubuntu, Arch, …). Windows is not supported — the app tells you so and exits. No `curl | bash`: every path below is a standard, verifiable install.### From source with pipx (recommended)[pipx](https://pipx.pypa.io) installs hackingtool into its own isolated environment and puts the `hackingtool` command on your PATH, so you can launch it from any directory. bash # 1 — get the code git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool # 2 — install it onto your PATH (isolated venv, no system Python touched) pipx install . # 3 — run it from anywhere hackingtool No pipx yet? bash # macOS brew install pipx && pipx ensurepath # Debian / Ubuntu / Kali sudo apt install pipx && pipx ensurepath Open a new shell after `pipx ensurepath` so the PATH change takes effect. To update later: `git pull && pipx install . --force`. To remove it: `pipx uninstall hackingtool`. Alternative: uv tool install . (same result, uses uv instead of pipx) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv tool install . # installs the `hackingtool` executable on your PATH hackingtool Alternative: plain venv + pip (no PATH changes) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool python3 -m venv .venv && . .venv/bin/activate pip install . # or: pip install -e . for an editable dev install hackingtool The command is only on your PATH while that venv is activated. ### For development[uv](https://docs.astral.sh/uv/) creates the virtualenv and installs everything from `pyproject.toml` / `uv.lock` in one step: bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv sync uv run hackingtool No uv yet? `pipx install uv` (or see the [uv install docs](https://docs.astral.sh/uv/getting-started/installation/)).**Contributing?** `make setup` wires the pre-push hook and `make check` runs the full gate (lint + tests + catalog validation). See [CONTRIBUTING.md](CONTRIBUTING.md).### Docker Pull and run the published : bash docker run -it --rm hardikzinzu/hackingtool:latest Or build it locally from a checkout: bash git clone https://github.com/Z4nzu/hackingtool.git && cd hackingtool docker build -t hackingtool . docker run -it --rm hackingtool ### Optional runtimesSome individual tools need a language runtime to install/run; the core app doesn't.| Dependency | Version | Needed for | |---|---|---| | Go | 1.21+ | nuclei, ffuf, amass, httpx, katana, dalfox, gobuster, subfinder | | Ruby | any | haiti, evil-winrm | | tmux | any | background panes (`/run … &`, `/panes`, `/attach`) | | Docker | any | Mythic, MobSF (optional) |---## Quick CommandsLaunch `hackingtool` and type. There are only three kinds of input:| You type | It means | Example | |---|---|---| | `/…` | a command you run | `/search subdomain` | | `@…` | a thing you name | `@nmap`, `@tag:osint` | | anything else | plain English "what I want to do" | `crack a wifi handshake` |@ completes tool names — @tag: completes tags, / completes commands. ### Command reference| Command | Aliases | What it does | |---|---|---| | `/run [args] [&]` | `/open` | open a tool's menu; with a trailing `&` it runs in a background tmux pane instead (that's where `args` are used) | | `/search ` | | search tools by name, description or tag | | `/tags` | | list every tag with its tool count | | `/ai ` | `/recommend`, `/r` | recommend tools for a goal | | `/goal ` | | AI-plan an objective and run it step by step, with per-step confirmation | | `/find ` | `/discover` | find tools for a need — your catalog first, then GitHub (suggest-only) | | `/panes` | `/jobs` | list background panes | | `/attach` | | attach to the background session (`Ctrl-b` `d` to return) | | `/kill ` | | kill one background pane, or all of them | | `/config [key value]` | | view/change settings; `/config test` checks the AI connection, `/config github` checks the GitHub token | | `/skill` | | show the operator playbook | | `/update` · `/uninstall` | `/remove` | update system packages or hackingtool · remove hackingtool and its tools | | `/clear` | `/cls` | clear the screen | | `/back` | `/b` | leave the current tool and go back | | `/help` | `/?`, `/h` | quick reference card | | `/quit` | `/q`, `/exit` | exit (also `q`, `Ctrl-C`, `Ctrl-D`) | | `@` | | open a tool (case-insensitive, fuzzy fallback) | | `@tag:` | | list and k from the tools carrying that tag |Inside a category: `1–N` k a tool · `97` install everything not yet installed · `98` archived tools · `99` back. Inside a tool: `1` install · `2` run · `c` ask for the exact command for your goal · `98` project page · `99` back./help — the same card, in the app. On a non-interactive terminal (or without `prompt_toolkit`) hackingtool falls back to the classic numbered menu, where `/` or `s` searches, `t` filters by tag, `r` or `a` recommends, `?` helps and `q` quits. Force it with `hackingtool --classic`.> **New here?** [docs/HOW-TO-USE.md](docs/HOW-TO-USE.md) walks through each of these > start to finish with numbered steps.---## Features ### ? `/find` — a tool for a need you don't have yetSearches the 215 curated tools first, then the GitHub search API, and ranks the results explainably. **Suggest-only** — it never clones, installs or runs anything — and it makes **zero model calls**./find crack a wpa handshakeIn your toolbox (vetted) • aircrack-ng (WiFi security suite) • Kismet (wireless detector / WIDS) • Reaver (WPS PIN attack) • WiGLE (wardriving map & API) • hashcat example hashes (WPA mode 22000)Found on GitHub — NOT vetted by uswifiphisher/wifiphisher 14713★ GPL-3.0 The Rogue Access Point Framework 14713★ · trusted author (ships in our catalog) · active · matches: security, wifi git clone https://github.com/wifiphisher/wifiphisher … Press `a` to keep a result: it is saved to `~/.hackingtool/found.yaml` as a "Discovered tools" entry — title, tags, description, link, and **no install or run command**, so a discovered entry can never execute anything. It shows up in your menu and in `/search` next launch.Out-of-scope asks (jamming, DoS, mass-targeting, malware) are refused **before any network call**, with an authorized alternative where one exists. Defensive/DFIR phrasing is never refused.Works anonymously at 10 GitHub searches/minute; a **no-scope, no-permission** token raises that to 30 — see [`/config github`](docs/HOW-TO-USE.md#7-add-a-github-token-for-find-config-github).### ? `/goal` — plan an objective, run it one step at a time /goal find live subdomains of example.com hackingtool drafts a short plan of real commands (with the reason for each step and an install hint for tools you don't have), asks you to confirm you are **authorized** to test the target, then walks the steps: `[y]` run · `[s]` skip · `[e]` edit · `[q]` abort. Every step runs list-form — never through a shell — and each goal gets a timestamped workspace under `~/.hackingtool/goals/` holding `plan.json`, a UTC-stamped `run.log`, and the raw output of each step.The model is called **once**, for planning; tool output is never fed back to it. With no model configured, `/goal` degrades to tool recommendations for the same objective.### ? Recommendations — say what you want in plain EnglishBare text (or `/ai`) maps intent to tools. The model may only return tags from the fixed taxonomy, and the catalog resolves tags → tools, so a tool can never be invented; with no model reachable a stdlib keyword matcher answers instead./ai — k one of the common tasks, or type the job in your own words. ### ? Tags and search`/tags` prints every tag in use with its live tool count; `@tag:` opens the tools carrying it; `/search ` matches names, descriptions and tags. /tags — 63 tags in use, with the number of tools behind each. ### ▶ Background panes (tmux)Long scans shouldn't block your console. With tmux installed, `/run … &` opens a labeled window in one detached `hackingtool` session: /run nmap -sV -oA scan 10.0.0.5 & ▶ started 'nmap' in background — /attach to view ` /panes` lists them, `/attach` watches one (`Ctrl-b` `d` to come back), `/kill ` or `/kill all` stops them, and the status line under the prompt shows `▶ N running`. No tmux? It says so and opens the tool inline instead; disable it entirely with `/config background_runner off`.### ⚙ Settings and the AI layer`/config` opens a full-screen settings editor (`↑↓` move, `←→` change, `Enter` edit, `t` test the connection, `Esc` close); `/config ` sets one key from the prompt. Settings live in `~/.hackingtool/config.json`.The AI layer is **opt-in and bring-your-own-key**: an OpenAI-compatible endpoint when `ai_base_url` + an API key are set, else a local [Ollama](https://ollama.com), else nothing — every feature degrades to a deterministic offline behaviour instead of guessing. Your API key is written only to `~/.hackingtool/.env` (mode 600), never to `config.json`, and never printed back. `/config test` reports the real failure if a probe fails.### ? Headless engagementsThe same catalog drives a non-interactive orchestrator that normalizes tool output into one `findings.json`: bash hackingtool --engagement acme --targets example.com --pipeline recon hackingtool --engagement acme --report # deterministic Markdown report hackingtool --engagement acme --ai-summary # opt-in triage of the REAL findings hackingtool --engagement acme --ai-report # opt-in narrative draft (report.draft.md) Out-of-scope targets are flagged and logged before anything runs, and the AI passes only ever summarize findings that exist.---## Documentation... {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/Z4nzu/hackingtool](https://github.com/Z4nzu/hackingtool) ⭐ Star数:79344 ? 开发语言:Python ? 项目描述:面向黑客的一体化黑客工具 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool"}总的来说,**hackingtool**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
2026年值得收藏的开源项目:NIUSHOP开源商城 V5 DEV全开源 源码分享 今天给大家分享一款基于PHP开发的开源项目——**NIUSHOP开源商城 V5 DEV全开源**。这个项目在Gitee上获得了2553个Star,669次Fork,说明还是有不少开发者在使用和关注的。项目主要特点是Niushop开源商城,本源码是稳定版源码,免费商用。,适合需要快速搭建网站的开发者和站长使用。 # # 项目功能介绍  ### Niushop开源商城开发版 - 前后端全部100%开源 # ## 马上加入Niushop开发者,共同构建新零售电商应用开发生态!!! **开源啦** !!!**商城后端开源** !!!**前端Uniapp代码开源** !!!**100%开源** !!! **无任何加密** !!! **简单而又暴力** !!!技术亮点 - 标准API接口,前后端分离,二次开发更方便 - 内置消息队列,全面支持redis缓存机制,支持大数据、高并发、大流量 - 钩子 + 插件,组件化开发,可复用,开发便捷 - 结构化的商城模板设计,制作加入NiuShop商城开发者生态您将可以获得 1. 加入官方每周一场的商城开发互动直播 2. 学习商城架构,表设计,插件设计,模块化开发思路 3. 官方提供免费而有价值的专业二次开发教程 4. 商城二开项目的接单 5. 开发者开发插件,商城模板,与官方共同销售分成... # ## 产品介绍 **快速搭建专属店铺,迅速展开线上业务** 默默耕耘,是为了在明天硕果累累;沉淀积累,是为了在未来厚积薄发!!自Niushop单商户于2016年上线以来,历时几年时间的迭代更新,应广大用户的要求,Niushop单商户V5时代终于来啦~ V5是一个全新的开始,升级重构多门店、收银一体化、软硬件物联、商品线上线下营销完全打通;前后端代码重组优化80%以上; 更加强大的DIY自定义装修;完全内置消息队列、Redis缓存服务,是大型商城运营的首选,抓紧下载体验起来吧~# ## 操作指南 :fa-th-list: [ | [服务市场]() | [系统功能]() | [系统演示](https://uniapp.v5.niuteam.cn/) | [使用手册](https://www.kancloud.cn/niucloud/niushop_b2c_v5/3037616) | [二开手册](https://www.kancloud.cn/niucloud/niushop_b2c_v4_develop/1839354) | [论坛地址](https://www.niushop.com/web/community/index.html) | [留言评论](https://www.niushop.com/web/community/index.html)# ## 演示站后台[ 查看 ] https://uniapp.v5.niuteam.cn/shop 账号:test 密码:niushoptest ### 演示 ### 推荐阿里云服务器配置  # ## 环境要求 Nignx/Apache PHP 7.4 MySQL 5.6~8.0 Redis 支持# ## Niushop官方群 [ ThinkPhp6 + LayUi + ElementUi,学习维护成本低 2. 前端由UNI-APP框架编写,支持多端,易于维护 3. 钩子 + 插件,组件化开发,可复用,开发便捷 4. 标准API接口,前后端分离,二次开发更方便 5. 内置消息队列,全面支持redis缓存机制,支持大数据、高并发、大流量 6. 代码全部开源,方便企业扩展自身业务需求# ## 亮点 1.框架采用全新thinkphp6+事件开发设计+layui+uniapp进行设计,代码完全重构,支持百万级! 2.前端以layui + uniapp模块化开发; 3.数据导出采用phpExcel,使数据更加直观,更方便于管理统计; 4.插件钩子机制,功能模块独立,更有助于二次开发; 5.后台采用ECharts,直观体现关系数据可视化的图,支持图与图之间的混搭。实现完善的数据统计和分析; 6.Easy 7.内置强大灵活的权限管理体系,有利于专人专项运营; 8.内置组合数据统计,系统配置,管理碎片化数据统计; 9.客户端完善的交互效果和动画,提升用户端视觉体验; 10.可以完美对接公众号和小程序,并且数据同步,实现真正意义上的一端开发,多端使用; 11.内置客服系统,可以对接企微客服、腾讯客服、小程序客服以及Niushop客服,客服在线实时聊天; 12.高频数据redis缓存,数据库读写分离,很大程度减轻服务器压力,提升访问速度; 13.后台设置菜单中可以一键数据备份和恢复,完全傻瓜式操作就可以轻松升级备份; 14.在线一键升级,轻松跨越到最新版本; 15.标准Api接口、前后端分离,二次开发更方便快捷; 16.支持数据库结构、数据、模板在线缓存清除,提升用户体验; 17.可视化DIY店铺装修,方便、快捷、直观,可以随心所欲装扮自己的店铺; 18.无缝事件机制行为扩展更方便,方便二次开发; 19.支持队列降低流量高峰,解除代码耦合性,高可用性; 20.在线一键安装部署,自动检测系统环境一键安装,省时省力快捷部署;# ## 前端部分界面展示 # ## 后端部分界面展示 # ### 好啦!话不多说,相信你早已跃跃欲试了,那就行动起来通过下方链接赶紧下载体验吧! git clone https://gitee.com/niushop-team/niushop_b2c_v5.git # ## 开源版使用须知 1.允许用于个人学习、毕业设计、教学案例、公益事业、商业使用; 2.如果商用必须保留版权信息,请自觉遵守; 3.禁止将本开源的代码和资源进行任何形式任何名义的出售,否则产生的一切任何后果责任由侵权者自负; 4.本版本源码全部开源;包括前端,后端,无任何加密; 5.商用请仔细审查代码和漏洞,不得用于任一国家许可范围之外的商业应用,产生的一切任何后果责任自负; 6.马上加入NiuShop开发者,构建新零售电商应用开发生态; 7.一切事物有个人喜好的标准,本开源代码意在分享,不喜勿喷。 # ## 合作伙伴  # ## 版权信息 版权所有Copyright © 2015-2024 NiuShop开源商城 版权所有 All rights reserved。 牛之云科技有限公司 提供技术支持 以上就是关于**NIUSHOP开源商城 V5 DEV全开源**的简单介绍。这个项目的代码结构清晰,文档也比较完善,对于PHP初学者来说也是一个不错的学习资源。有兴趣的朋友可以通过下方链接下载源码体验一下。 {card-default label="? 项目信息" /} ? 项目名称:NIUSHOP开源商城 V5 DEV全开源 ? 开发作者:niushop](https://qm.# ## V5商城特色 强大的营销功能模块,丰富的行业模板和装修组件,快速搭建最适合自己的电商平台,轻松获客、裂变。开启电商运营之路。 1.
-
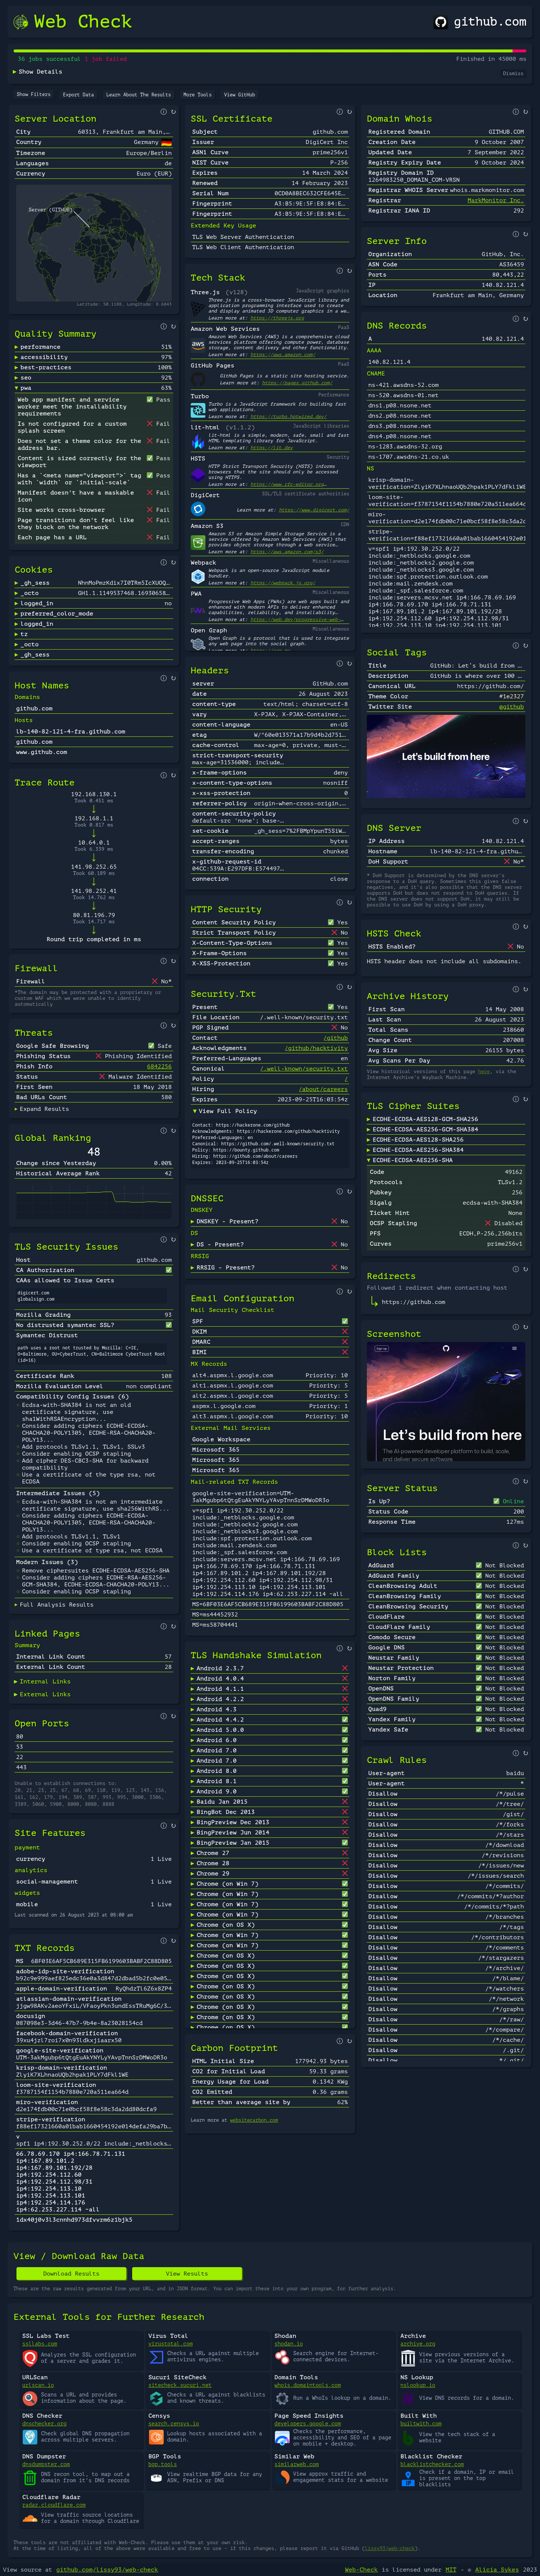
深度评测:web-check 这款工具到底怎么样 推荐一个实用的开源工具——web-check。项目由lissy93开发维护,GitHub上获得了 34690 个Star。简单来说,它是一款用于分析任何网站的一?️♂️体化OSINT工具,对于站长和开发者来说是个不错的工具。 工具功能介绍 Web-Check Comprehensive, on-demand open source intelligence for any website ? web-check.xyz---Kindly supported by: NinjaPear API to get a full B2B profiles from any URL Terminal Trove The $HOME of all things in the terminal Warp Built for coding with multiple AI agents About Screenshot Live Demo Mirror Features Usage Deployment Option#1: Netlify Option#2: Vercel Option#3: Docker Option#4: Render Option#5: Source Configuration Options Developer Setup Community Contributing Bugs Support License--- About Get an insight into the inner-workings of a given website: uncover potential attack vectors, analyse server architecture, view security configurations, and learn what technologies a site is using.Currently the dashboard will show: IP info, SSL chain, DNS records, cookies, headers, domain info, search crawl rules, page map, server location, redirect ledger, open ports, traceroute, DNS security extensions, site performance, trackers, associated hostnames, carbon footprint. Stay tuned, as I'll add more soon!The aim is to help you easily understand, optimize and secure your website. Screenshot Expand ScreenshotScreenshotScreenshot Live DemoA hosted version can be accessed at: web-check.as93.net Mirror The source for this repo is mirrored to CodeBerg, available at: codeberg.org/alicia/web-check Status Build & Deploys: Repo Management & Miscellaneous: Features Click to expand / collapse sectionNote _this list needs updating, many more jobs have been added since..._The following section outlines the core features, and briefly explains why this data might be useful for you to know, as well as linking to further resources for learning more. IP Info Description An IP address (Internet Protocol address) is a numerical label assigned to each device connected to a network / the internet. The IP associated with a given domain can be found by querying the Domain Name System (DNS) for the domain's A (address) record. Use CasesFinding the IP of a given server is the first step to conducting further investigations, as it allows us to probe the server for additional info. Including creating a detailed map of a target's network infrastructure, pinpointing the physical location of a server, identifying the hosting service, and even discovering other domains that are hosted on the same IP address. Useful Links- Understanding IP Addresses IP Addresses - Wiki RFC-791 Internet Protocol whatismyipaddress.com SSL Chain DescriptionSSL certificates are digital certificates that authenticate the identity of a website or server, enable secure encrypted communication (HTTPS), and establish trust between clients and servers. A valid SSL certificate is required for a website to be able to use the HTTPS protocol, and encrypt user + site data in transit. SSL certificates are issued by Certificate Authorities (CAs), which are trusted third parties that verify the identity and legitimacy of the certificate holder. Use CasesSSL certificates not only provide the assurance that data transmission to and from the website is secure, but they also provide valuable OSINT data. Information from an SSL certificate can include the issuing authority, the domain name, its validity period, and sometimes even organization details. This can be useful for verifying the authenticity of a website, understanding its security setup, or even for discovering associated subdomains or other services. Useful Links- TLS - Wiki What is SSL (via Cloudflare learning) RFC-8446 - TLS SSL Checker DNS Records Description This task involves looking up the DNS records associated with a specific domain. DNS is a system that translates human-readable domain names into IP addresses that computers use to communicate. Various types of DNS records exist, including A (address), MX (mail exchange), NS (name server), CNAME (canonical name), and TXT (text), among others. Use CasesExtracting DNS records can provide a wealth of information in an OSINT investigation. For example, A and AAAA records can disclose IP addresses associated with a domain, potentially revealing the location of servers. MX records can give clues about a domain's email provider. TXT records are often used for various administrative purposes and can sometimes inadvertently leak internal information. Understanding a domain's DNS setup can also be useful in understanding how its online infrastructure is built and managed. Useful Links- What are DNS records? (via Cloudflare learning) DNS Record Types RFC-1035 - DNS DNS Lookup (via MxToolbox) Cookies Description The Cookies task involves examining the HTTP cookies set by the target website. Cookies are small pieces of data stored on the user's computer by the web browser while browsing a website. They hold a modest amount of data specific to a particular client and website, such as site preferences, the state of the user's session, or tracking information. Use CasesCookies can disclose information about how the website tracks and interacts with its users. For instance, session cookies can reveal how user sessions are managed, and tracking cookies can hint at what kind of tracking or analytics frameworks are being used. Additionally, examining cookie policies and practices can offer insights into the site's security settings and compliance with privacy regulations. Useful Links- HTTP Cookie Docs (Mozilla) What are Cookies (via Cloudflare Learning) Testing for Cookie Attributes (OWASP) RFC-6265 - Cookies Crawl Rules Description Robots.txt is a file found (usually) at the root of a domain, and is used to implement the Robots Exclusion Protocol (REP) to indicate which pages should be ignored by which crawlers and bots. It's good practice to avoid search engine crawlers from over-loading your site, but should not be used to keep pages out of search results (use the noindex meta tag or header instead). Use CasesIt's often useful to check the robots.txt file during an investigation, as it can sometimes disclose the directories and pages that the site owner doesn't want to be indexed, potentially because they contain sensitive information, or reveal the existence of otherwise hidden or unlinked directories. Additionally, understanding crawl rules may offer insights into a website's SEO strategies. Useful Links- Google Search Docs - Robots.txt Learn about robots.txt (via Moz.com) RFC-9309 - Robots Exclusion Protocol Robots.txt - wiki Headers Description The Headers task involves extracting and interpreting the HTTP headers sent by the target website during the request-response cycle. HTTP headers are key-value pairs sent at the start of an HTTP response, or before the actual data. Headers contain important directives for how to handle the data being transferred, including cache policies, content types, encoding, server information, security policies, and more. Use CasesAnalyzing HTTP headers can provide significant insights in an OSINT investigation. Headers can reveal specific server configurations, chosen technologies, caching directives, and various security settings. This information can help to determine a website's underlying technology stack, server-side security measures, potential vulnerabilities, and general operational practices. Useful Links- HTTP Headers - Docs RFC-7231 Section 7 - Headers List of header response fields OWASP Secure Headers Project Quality Metrics Description Using Lighthouse, the Quality Metrics task measures the performance, accessibility, best practices, and SEO of the target website. This returns a simple checklist of 100 core metrics, along with a score for each category, to gauge the overall quality of a given site. Use CasesUseful for assessing a site's technical health, SEO issues, identify vulnerabilities, and ensure compliance with standards. Useful Links- Lighthouse Docs Google Page Speed Tools W3 Accessibility Tools Google Search Console SEO Checker PWA Builder Server Location Description The Server Location task determines the physical location of the server hosting a given website based on its IP address. This is done by looking up the IP in a location database, which maps the IP to a lat + long of known data centers and ISPs. From the latitude and longitude, it's then possible to show additional contextual info, like a pin on the map, along with address, flag, time zone, currency, etc. Use CasesKnowing the server location is a good first step in better understanding a website. For site owners this aids in optimizing content delivery, ensuring compliance with data residency requirements, and identifying potential latency issues that may impact user experience in specific geographical regions. And for security researchers, it helps assess the risk posed by specific regions or jurisdictions regarding cyber threats and regulations. Useful Links- IP Locator Internet Geolocation - Wiki Associated Hosts Description This task involves identifying and listing all domains and subdomains (hostnames) that are associated with the website's primary domain. This process often involves DNS enumeration to discover any linked domains and hostnames, as well as looking at known DNS records. Use CasesDuring an investigation, understanding the full scope of a target's web presence is critical. Associated domains could lead to uncovering related projects, backup sites, development/test sites, or services linked to the main site. These can sometimes provide additional information or potential security vulnerabilities. A comprehensive list of associated domains and hostnames can also give an overview of the organization's structure and online footprint. Useful Links- DNS Enumeration - Wiki OWASP - Enumerate Applications on Webserver DNS Enumeration - DNS Dumpster Subdomain Finder Redirect Chain Description This task traces the sequence of HTTP redirects that occur from the original URL to the final destination URL. An HTTP redirect is a response with a status code that advises the client to go to another URL. Redirects can occur for several reasons, such as URL normalization (directing to the www version of the site), enforcing HTTPS, URL shorteners, or forwarding users to a new site location. Use CasesUnderstanding the redirect chain can be useful for several reasons. From a security perspective, long or complicated redirect chains can be a sign of potential security risks, such as unencrypted redirects in the chain. Additionally, redirects can impact website performance and SEO, as each redirect introduces additional round-trip-time (RTT). For OSINT, understanding the redirect chain can help identify relationships between different domains or reveal the use of certain technologies or hosting providers. Useful Links- HTTP Redirects - MDN URL Redirection - Wiki 301 Redirects explained TXT Records DescriptionTXT records are a type of DNS record that provides text information to sources outside your domain. They can be used for a variety of purposes, such as verifying domain ownership, ensuring email security, and even preventing unauthorized changes to your website. Use CasesThe TXT records often reveal which external services and technologies are being used with a given domain. They may reveal details about the domain's email configuration, the use of specific services like Google Workspace or Microsoft 365, or security measures in place such as SPF and DKIM. Understanding these details can give an insight into the technologies used by the organization, their email security practices, and potential vulnerabilities. Useful Links- TXT Records (via Cloudflare Learning) TXT Records - Wiki RFC-1464 - TXT Records TXT Record Lookup (via MxToolbox) Server Status Description Checks if a server is online and responding to requests... {card-default label="? 工具信息" /} ? 项目地址:https://github.com/lissy93/web-check ⭐ Star数:34690 ? 开发语言:TypeScript ? 项目描述:用于分析任何网站的一?️♂️体化OSINT工具 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/lissy93/web-check/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/lissy93/web-check"} 总的来说,web-check是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
安全圈热门工具 sqlmap 体验分享 推荐一个实用的开源工具——sqlmap。项目由sqlmapproject开发维护,GitHub上获得了 38375 个Star。简单来说,它是一款自动SQL注入和数据库接管工具,对于站长和开发者来说是个不错的工具。 工具功能介绍 sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester, and a broad range of switches including database fingerprinting, over data fetching from the database, accessing the underlying file system, and executing commands on the operating system via out-of-band connections.Screenshots ----ScreenshotYou can visit the collection of screenshots demonstrating some of the features on the wiki.Installation ----You can download the latest tarball by clicking here or latest zipball by clicking here.Preferably, you can download sqlmap by cloning the Git repository:git clone --depth 1 https://github.com/sqlmapproject/sqlmap.git sqlmap-devsqlmap works out of the box with Python version 2.7 and 3.x on any platform.Usage ----To get a list of basic options and switches use:python sqlmap.py -hTo get a list of all options and switches use:python sqlmap.py -hhYou can find a sample run here. To get an overview of sqlmap capabilities, a list of supported features, and a description of all options and switches, along with examples, you are advised to consult the user's manual.Links ----* Homepage: https://sqlmap.org Download: .tar.gz or .zip Commits RSS feed: https://github.com/sqlmapproject/sqlmap/commits/master.atom Issue tracker: https://github.com/sqlmapproject/sqlmap/issues User's manual: https://github.com/sqlmapproject/sqlmap/wiki Frequently Asked Questions (FAQ): https://github.com/sqlmapproject/sqlmap/wiki/FAQ X: @sqlmap Demos: https://www.youtube.com/user/inquisb/videos Playground: https://sekumart.sekuripy.hr Research: https://www.sekuripy.hr/labs/sqlmap/#research Screenshots: https://github.com/sqlmapproject/sqlmap/wiki/ScreenshotsTranslations ----* Arabic Bengali Bulgarian Chinese Croatian Dutch French Georgian German Greek Hindi Indonesian Italian Japanese Korean Kurdish (Central) Persian Polish Portuguese Russian Serbian Slovak Spanish Turkish Ukrainian Vietnamese {card-default label="? 工具信息" /} ? 项目地址:https://github.com/sqlmapproject/sqlmap ⭐ Star数:38375 ? 开发语言:Python ? 项目描述:自动SQL注入和数据库接管工具 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/sqlmapproject/sqlmap/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/sqlmapproject/sqlmap"} 总的来说,sqlmap是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
分享一个不错的建站源码:tpcms 完整源码 tpcms 推荐一个实用的PHP开源项目——tpcms。项目由ThinkPHP开发维护,采用未知开源协议发布。简单来说,它是一个ThinkPHP3.X 使用ThinkPHP3.X开发的基础系统,包含后台用户分组管理;后台用户组权限控制;根据用户权限,显示管理菜单;网站系统配置功能。可用他来衍生各种产品。,对于需要搭建网站的朋友来说是个不错的选择。 项目功能介绍 CMS管理系统 [ 介绍 ] 这是一套使用ThinkPHP3.X开发的基础系统,包含后台用户权限控制, 后台用户分组管理、网站系统配置功能,可用他来衍生各种产品。 [ 安装方法 ] 1 创建MYSQL数据库,导入 cms.sql 2 把根目录的config.php.bak文件名改成config.php 3 根据你的数据库,配置config.php “db_host db_name db_user db_pwd db_port” 4 后台入口 http://domain/admin 5 后台帐号密码 admin admin 6 后台菜单设置方法请参考已有的那些菜单 [ 目录结构 ] |-admin 后台入口跳转路径 |-Core 系统核心 | ├Common 项目公共函数文件目录 | ├Conf 项目配置目录 | | ├Admin/config.php 项目后台配置文件 | | └Home/config.php 项目前台配置文件 | | | ├Lang 项目多语言包目录 | | ├en-us 英文言包目录 | | └zh-cn 中文言包目录 | | | ├Lib 项目类库目录 | | ├Action 控制器 | | └Model 模型 | | | ├config.php 项目配置文件 | ├define.php 项目路径常量配置文件 | └tags.php 项目扩展行为调用配置文件 | |-Public 公共静态文件目录 | ├Admin 后台公共静态目录 | ├Home 前台公共静态目录 | ├js 公共JS目录 | └tips 信息提示跳转页面 | |-Temp 系统缓存目录 |-Template 项目模板目录 | ├Admin/default 后台模板目录 | └Home/default 前台模板目录 | |-config.php 网站配置文件 └-index.php 系统入口文件 [ 协议 ] 本系统除ThinkPHP框架外,遵循MIT开源许可协议发布 具体参考LICENSE.txt内容 综合来看,tpcms在同类项目中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。使用过程中如果遇到问题,也可以去项目主页提交Issue反馈。 {card-default label="? 项目信息" /} ? 项目名称:tpcms ? 开发作者:ThinkPHP ? 项目描述:ThinkPHP3.X 使用ThinkPHP3.X开发的基础系统,包含后台用户分组管理;后台用户组权限控制;根据用户权限,显示管理菜单;网站系统配置功能。可用他来衍生各种产品。 ? 开发语言:PHP ? 开源协议:未知开源协议 ⭐ Star数:69 | ? Fork数:49 ? 更新时间:2025年04月21日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/ThinkPHP/tpcms/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/ThinkPHP/tpcms.git"}
-
网络安全工具 dirsearch 实战分享 推荐一个实用的开源工具——**dirsearch**。项目由maurosoria开发维护,GitHub上获得了 **14697** 个Star。简单来说,它是一款Web路径扫描仪,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍   > An advanced web path brute-forcer**dirsearch** is being actively developed by [@maurosoria](https://twitter.com/_maurosoria) and [@shelld3v](https://twitter.com/shells3c_).Join the [Discord server](https://discord.gg/2N22ZdAJRj) to communicate with the team.## Quick Startdirsearch requires Python 3.11 or higher. sh git clone https://github.com/maurosoria/dirsearch.git --depth 1 cd dirsearch python3 dirsearch.py -u https://example.com -e php,html,js You can also install the latest Python stack directly from GitHub with pip: sh pip3 install git+https://github.com/maurosoria/dirsearch.git dirsearch -u https://example.com -e php,html,js The Rust native backend is opt-in for source installs; see [Installation](docs/installation.md) for the native build steps.Pre-built PyInstaller binaries and portable folder archives are available on the [Releases page](https://github.com/maurosoria/dirsearch/releases). ## Documentation The full documentation now lives in [`docs/`](docs/index.md):- [Installation](docs/installation.md): supported platforms, Python install, release artifacts, and Docker. - [Usage Guide](docs/usage.md): common scans, recursion, filters, proxies, raw requests, reports, and tips. - [Wordlists](docs/wordlists.md): `%EXT%`, categories, templates, prefixes, suffixes, and transformations. - [CLI Options](docs/options.md): complete command-line reference. - [Configuration](docs/configuration.md): `config.ini` reference. - [Sessions](docs/sessions.md): save, list, and resume scan sessions. - [Python API](docs/python-api.md): importable API examples. - [Building](docs/building.md): PyInstaller, portable builds, Docker s, and GitHub Actions. - [References](docs/references.md): external tutorials and articles.## Minimal Examples sh python3 dirsearch.py -u https://target python3 dirsearch.py -u https://target -e php,html,js python3 dirsearch.py -u https://target -e php,html,js -w /path/to/wordlist python3 dirsearch.py -u https://target -r --max-recursion-depth 3 Use `python3 dirsearch.py -h` for common options or `python3 dirsearch.py -hh` for the complete CLI help.## Python APIdirsearch can also be used from Python code for local automation, MCP servers, REST wrappers, and agent-controlled scans. The importable API keeps its configuration in `FuzzerConfig`, so callers do not need to parse CLI flags or mutate CLI globals.See [Python API](docs/python-api.md) for examples covering templates, custom wordlists, callbacks, authenticated sessions, and agent-oriented scan recipes.## Contributing Pull requests and feature requests are welcome. See [CONTRIBUTORS.md](CONTRIBUTORS.md) for the people who have helped improve dirsearch. ## License Copyright (C) Mauro Soria (maurosoria@gmail.com)License: GNU General Public License, version 2. {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/maurosoria/dirsearch](https://github.com/maurosoria/dirsearch) ⭐ Star数:14697 ? 开发语言:Python ? 项目描述:Web路径扫描仪 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/maurosoria/dirsearch/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/maurosoria/dirsearch"}总的来说,**dirsearch**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
免费开源绿色软件推荐:fuzzdb-collect 下载 推荐一个实用的开源工具——fuzzdb-collect。项目由euphratica开发维护,采用未知开源协议发布。简单来说,它是一个网络上安全资源的搜集,对于站长和开发者来说是个不错的工具。 工具功能介绍 项目简介 Scanners Box是一个集合github平台上的安全行业从业者自研开源扫描器的仓库,包括子域名枚举、数据库漏洞扫描、弱口令或信息泄漏扫描、端口扫描、指纹识别以及其他大型扫描器或模块化扫描器,同时该仓库只收录各位网友自己编写的一般性开源扫描器,类似awvs、nmap、w3af等知名扫描工具不收录。 恶意软件 https://github.com/deadPix3l/CryptSky/ (勒索软件) DDOS防护 https://github.com/ywjt/Dshield waf开源及规则 https://github.com/SpiderLabs/ModSecurity https://github.com/xsec-lab/x-waf https://github.com/loveshell/ngx_lua_waf https://github.com/SpiderLabs/owasp-modsecurity-crs/tree/master/base_rules 入门指南 https://wizardforcel.gitbooks.io/web-hacking-101/content/ Web Hacking 101 中文版 https://wizardforcel.gitbooks.io/asani/content/ 浅入浅出Android安全 中文版 https://wizardforcel.gitbooks.io/lpad/content/ Android 渗透测试学习手册 中文版 https://wizardforcel.gitbooks.io/kali-linux-web-pentest-cookbook/content/ Kali Linux Web渗透测试秘籍 中文版 https://github.com/hardenedlinux/linux-exploit-development-tutorial Linux exploit 开发入门 https://www.gitbook.com/book/t0data/burpsuite/details burpsuite实战指南 http://www.kanxue.com/?article-read-1108.htm=&winzoom=1 渗透测试Node.js应用 https://github.com/qazbnm456/awesome-web-security Web安全资料和资源列表 https://sec-wiki.com/ sec-wiki安全维基百科 fuzz工具收集 https://github.com/ivanfratric/winafl https://github.com/attekett/NodeFuzz https://github.com/google/oss-fuzz http://blog.topsec.com.cn/ad_lab/alphafuzzer/ http://llvm.org/docs/LibFuzzer.html 子域名枚举扫描器或爆破工具 https://github.com/n4xh4ck5/N4xD0rk (利用搜索引擎来搜集子域名,可以使用西班牙语搜集) https://github.com/jonluca/Anubis https://github.com/lijiejie/subDomainsBrute (lijiejie开发的一款使用广泛的子域名爆破枚举工具) https://github.com/ring04h/wydomain (猪猪侠开发的一款域名收集全面、精准的子域名枚举工具) https://github.com/le4f/dnsmaper (子域名枚举爆破工具以及地图位置标记) https://github.com/0xbug/orangescan (提供web界面的在线子域名信息收集工具) https://github.com/TheRook/subbrute (高效精准的子域名爆破工具,同时也是扫描器中最常用的子域名API库) https://github.com/We5ter/GSDF (基于谷歌SSL透明证书的子域名查询脚本) https://github.com/mandatoryprogrammer/cloudflare_enum (使用CloudFlare进行子域名枚举的脚本) https://github.com/guelfoweb/knock (Knock子域名获取,可用于查找子域名接管漏洞) https://github.com/exp-db/PythonPool/tree/master/Tools/DomainSeeker (多方式收集目标子域名信息) https://github.com/code-scan/BroDomain (兄弟域名查询) https://github.com/chuhades/dnsbrute (高效的子域名爆破工具) https://github.com/yanxiu0614/subdomain3 (一款高效的子域名爆破工具) https://github.com/michenriksen/aquatone (子域名枚举、探测工具。可用于子域名接管漏洞探测) https://github.com/evilsocket/dnssearch (一款子域名爆破工具) https://github.com/reconned/domained (可用于子域名收集的一款工具) https://github.com/bit4woo/Teemo (域名收集及枚举工具) https://github.com/laramies/theHarvester ( https://github.com/swisskyrepo/Subdomino (子域名枚举,端口扫描,服务存活确认) https://github.com/nmalcolm/Inventus (通过爬虫实现的子域名收集工具) https://github.com/aboul3la/Sublist3r (快速子域枚举工具) 数据库类漏洞扫描器或爆破工具 https://github.com/0xbug/SQLiScanner (一款基于SQLMAP和Charles的被动SQL注入漏洞扫描工具) https://github.com/sqlmapproject/sqlmap (注入工具之王sqlmap) https://github.com/stamparm/DSSS (99行代码实现的sql注入漏洞扫描器) https://github.com/LoRexxar/Feigong (针对各种情况自由变化的MySQL注入脚本) https://github.com/youngyangyang04/NoSQLAttack (一款针对mongoDB的攻击工具) https://github.com/Neohapsis/bbqsql (SQL盲注利用框架) https://github.com/NetSPI/PowerUpSQL (攻击SQLSERVER的Powershell脚本框架) https://github.com/WhitewidowScanner/whitewidow (一款数据库扫描器) https://github.com/stampery/mongoaudit (MongoDB审计及渗透工具) https://github.com/torque59/Nosql-Exploitation-Framework (NoSQL扫描/爆破工具) https://github.com/missDronio/blindy (MySQL盲注爆破工具) https://github.com/fengxuangit/Fox-scan (基于SQLMAP的主动和被动资源发现的漏洞扫描工具) https://github.com/NetSPI/PowerUpSQL (用于SQL Server审计的powershell脚本) https://github.com/JohnTroony/Blisqy (用于- http header中的时间盲注爆破工具,仅针对MySQL/MariaDB) https://github.com/ron190/jsql-injection (Java 编写的SQL注入工具) https://github.com/Hadesy2k/sqliv (基于搜索引擎的批量SQL注入漏洞扫描器) https://github.com/UltimateHackers/sqlmate (在sqlmap基础上增加了目录扫描、hash爆破等功能) 弱口令/弱用户名扫描器或爆破工具 https://github.com/lijiejie/htpwdScan (一个简单的- http暴力破解、撞库攻击脚本) https://github.com/ysrc/F-Scrack (对各类服务进行弱口令检测的脚本) https://github.com/Mebus/cupp (根据用户习惯生成弱口令探测字典脚本) https://github.com/netxfly/crack_ssh (Go写的协程版的ssh edis\mongodb弱口令破解工具) https://github.com/LandGrey/pydictor (暴力破解字典建立工具) https://github.com/shengqi158/weak_password_detect (多线程探测弱口令) https://github.com/UltimateHackers/Blazy (支持测试 CSRF, Clickjacking, Cloudflare and WAF的弱口令探测器) 物联网设备识别工具或扫描器 https://github.com/reverse-shell/routersploit (路由器漏洞利用框架) https://github.com/jh00nbr/Routerhunter-2.0 (路由器漏洞扫描利用) https://github.com/RUB-NDS/PRET (打印机攻击框架) https://github.com/rapid7/IoTSeeker (物联网设备默认密码扫描检测工具) https://github.com/shodan-labs/iotdb (使用nmap扫描IoT设备) https://github.com/googleinurl/RouterHunterBR (路由器设备漏洞扫描利用) https://github.com/scu-igroup/telnet-scanner (Telnet服务密码撞库) 反射型或DOM-Based XSS扫描器 https://github.com/shawarkhanethicalhacker/BruteXSS (一款XSS扫描器,可暴力注入参数) https://github.com/1N3/XSSTracer (小型XSS扫描器,也可检测CRLF、XSS、点击劫持的) https://github.com/0x584A/fuzzXssPHP (PHP版本的反射型xss扫描) https://github.com/chuhades/xss_scan (批量扫描XSS的python脚本) https://github.com/BlackHole1/autoFindXssAndCsrf (自动化检测页面是否存在XSS和CSRF漏洞的浏览器插件) https://github.com/shogunlab/shuriken (使用命令行进行XSS批量检测) https://github.com/UltimateHackers/XSStrike (可识别并绕过WAF的XSS扫描工具) https://github.com/stamparm/DSXS (支持GET、POST方式的高效XSS扫描器) 企业资产管理或信息泄露搜集工具 https://github.com/ysrc/xunfeng (网络资产识别引擎,漏洞检测引擎) https://github.com/laramies/theHarvester (企业被搜索引擎收录敏感资产信息监控脚本:员工 https://github.com/x0day/Multisearch-v2 (Bing、google、360、zoomeye等搜索引擎聚合搜索,可用于发现企业被搜索引擎收录的敏感资产信息) https://github.com/Ekultek/Zeus-Scanner (集成化的综合搜索引擎,能够抓取被搜索引擎隐藏的url,并交由sqlmap、nmap扫描) https://github.com/0xbug/Biu-framework (企业内网基础服务安全扫描框架) https://github.com/metac0rtex/GitHarvester (github Repo信息搜集工具) https://github.com/shengqi158/svnhack (.svn文件夹泄漏利用工具) https://github.com/repoog/GitPrey (GitHub敏感信息扫描工具) https://github.com/0xbug/Hawkeye (企业资产、敏感信息GitHub泄露监控系统) https://github.com/lianfeng30/githubscan (根据企业关键词进行项目检索以及相应敏感文件和文件内容扫描的工具) https://github.com/UnkL4b/GitMiner (github敏感信息搜索工具) https://github.com/lijiejie/GitHack (.git文件夹泄漏利用工具) https://github.com/dxa4481/truffleHog (GitHub敏感信息扫描工具,包括检测commit等) https://github.com/sowish/LNScan (详细的内部网络信息扫描器) https://github.com/SkyLined/LocalNetworkScanner (javascript实现的本地网络扫描器) https://github.com/x0day/Multisearch-v2 (搜索引擎聚合搜索,可用于发现企业被搜索引擎收录的敏感资产信息) webshell检测或病毒分析工具 https://github.com/ym2011/ScanBackdoor (一款简洁的Webshell扫描工具) https://github.com/yassineaddi/BackdoorMan (可对指定目录进行php webshell检测) https://github.com/he1m4n6a/findWebshell (一款简单的webshell检测工具) https://github.com/Tencent/HaboMalHunter (哈勃分析系统,linux系统病毒分析及安全检测) https://github.com/PlagueScanner/PlagueScanner (使用python实现的集成ClamAV、ESET、Bitdefender的反病毒引擎) https://github.com/nbs-system/php-malware-finder (一款高效率PHP-webshell扫描工具) https://github.com/emposha/PHP-Shell-Detector/ (测试效率高达99%的webshell检测工具) https://github.com/erevus-cn/scan_webshell (一款简洁的Webshell扫描工具) https://github.com/emposha/Shell-Detector (Webshell扫描工具,支持php/perl/asp/aspx webshell扫描) https://github.com/m4rco-/dorothy2 (一款木马、僵尸网络分析框架) 内网渗透或扫描工具 https://github.com/0xwindows/VulScritp (企业内网渗透脚本,包括banner扫描、端口扫描;phpmyadmin、jenkins等通用漏洞利用等) https://github.com/lcatro/network_backdoor_scanner (基于网络流量的内网探测框架) https://github.com/fdiskyou/hunter (调用 Windows API 枚举用户登录信息) https://github.com/BlackHole1/WebRtcXSS (自动化利用XSS入侵内网) https://github.com/0xwindows/VulScritp (企业内网渗透脚本,包括banner扫描、端口扫描;各种通用漏洞利用等) https://github.com/fdiskyou/hunter (调用 Windows API 枚举用户登录信息) https://github.com/AlessandroZ/LaZagne (本机密码查看提取工具) https://github.com/huntergregal/mimipenguin (linux密码抓取神器) 中间件扫描器或识别工具 https://nmap.org/download.html (Nmap端口扫描器之王,- https://svn.nmap.org/) https://github.com/ring04h/wyportmap (目标端口扫描+系统服务指纹识别) https://github.com/ring04h/weakfilescan (动态多线程敏感信息泄露检测工具) https://github.com/EnableSecurity/wafw00f (WAF产品指纹识别) https://github.com/rbsec/sslscan (ssl类型识别) https://github.com/urbanadventurer/whatweb (web指纹识别) https://github.com/tanjiti/FingerPrint (web应用指纹识别) https://github.com/nanshihui/Scan-T (网络爬虫式指纹识别) https://github.com/OffensivePython/Nscan (a fast Network scanner inspired by Masscan and Zmap) https://github.com/ywolf/F-NAScan (网络资产信息扫描, ICMP存活探测,端口扫描,端口指纹服务识别) https://github.com/ywolf/F-MiddlewareScan (中间件扫描) https://github.com/maurosoria/dirsearch (Web path scanner) https://github.com/x0day/bannerscan (C段Banner与路径扫描) https://github.com/RASSec/RASscan (端口服务扫描) https://github.com/3xp10it/bypass_waf (waf自动暴破) https://github.com/3xp10it/xcdn (尝试找出cdn背后的真实ip) https://github.com/Xyntax/BingC (基于Bing搜索引擎的C段/旁站查询,多线程,支持API) https://github.com/Xyntax/DirBrute (多线程WEB目录爆破工具) https://github.com/zer0h/- httpscan (一个爬虫式的网段Web主机发现小工具) https://github.com/lietdai/doom (thorn上实现的分布式任务分发的ip端口漏洞扫描器) https://github.com/chichou/grab.js (类似 zgrab 的快速 TCP 指纹抓取解析工具,支持更多协议) https://github.com/Nitr4x/whichCDN (CDN识别、检测) https://github.com/secfree/bcrpscan (基于爬虫的web路径扫描器) https://github.com/ring04h/wyportmap (目标端口扫描+系统服务指纹识别) https://github.com/rbsec/sslscan (SSL类型识别) https://github.com/urbanadventurer/whatweb (Web指纹识别) https://github.com/tanjiti/FingerPrint (Web应用指纹识别) https://github.com/OffensivePython/Nscan (基于Masscan和Zmap的网络扫描器) https://github.com/maurosoria/dirsearch (web路径收集与扫描) https://github.com/3xp10it/xcdn (尝试找出cdn背后的真实ip) https://github.com/lietdai/doom (Thorn上实现的分布式任务分发的ip端口漏洞扫描器) https://github.com/mozilla/ssh_scan (服务器ssh配置信息扫描) https://github.com/18F/domain-scan (针对域名及其子域名的资产数据检测/扫描,包括- http/- https检测等) https://github.com/ggusoft/inforfinder (域名资产收集及指纹识别工具) https://github.com/boy-hack/gwhatweb (CMS识别 python gevent实现) https://github.com/Mosuan/FileScan (敏感文件扫描 / 二次判断降低误报率 / 扫描内容规则化 / 多目录扫描) https://github.com/Xyntax/FileSensor (基于爬虫的动态敏感文件探测工具) https://github.com/deibit/cansina (web路径扫描工具) https://github.com/0xbug/Howl (网络设备 web 服务指纹扫描与检索) https://github.com/mozilla/cipherscan (目标主机服务ssl类型识别) https://github.com/xmendez/wfuzz (Web应用fuzz工具、框架,同时可用于web路径/服务扫描) https://github.com/UltimateHackers/Breacher (多线程的后台路径扫描器,也可用于发现Execution After Redirect漏洞) https://github.com/ztgrace/changeme (弱口令扫描器,不仅支持普通登录页,也支持ssh、mongodb等组件) https://github.com/medbenali/CyberScan (渗透测试辅助工具,支持分析数据包、解码、端口扫描、IP地址分析等) https://github.com/m0nad/HellRaiser (基于nmap的扫描器,与cve漏洞关联) https://github.com/scipag/vulscan (基于nmap的高级漏洞扫描器,命令行环境使用) https://github.com/jekyc/wig (web应用信息搜集工具) https://github.com/eldraco/domain_analyzer (围绕web服务的域名进行信息收集和"域传送"等漏洞扫描,也支持针对背后的服务器端口扫描等) https://github.com/cloudtracer/paskto (基于Nikto扫描规则的被动式路径扫描以及信息爬虫) https://github.com/zerokeeper/WebEye (快速识别WEB服务器类型、CMS类型、WAF类型、WHOIS信息、以及语言框架) https://github.com/m3liot/shcheck (用于检查web服务的- http header的安全性) https://github.com/aipengjie/sensitivefilescan (一款高效快捷的敏感文件扫描工具) https://github.com/fnk0c/cangibrina (通过字典穷举、google、robots.txt等途径的跨平台后台管理路径扫描器) https://github.com/n4xh4ck5/CMSsc4n (CMS指纹识别) 专用(即特定性针对某些组件)扫描器 https://github.com/brianwrf/hackUtils (java反序列化利用工具集) https://github.com/frohoff/ysoserial ( java反序列化利用工具) https://github.com/blackye/Jenkins (Jenkins漏洞探测、用户抓取爆破) https://github.com/code-scan/dzscan (discuz漏洞扫描) https://github.com/chuhades/CMS-Exploit-Framework (CMS攻击框架) https://github.com/lijiejie/IIS_shortname_Scanner (IIS短文件名漏洞扫描) https://github.com/riusksk/FlashScanner (flashxss扫描) https://github.com/coffeehb/SSTIF (服务器端模板注入漏洞的半自动化工具) https://github.com/epinna/tplmap (服务器端模板注入漏洞检测与利用工具) https://github.com/cr0hn/dockerscan (docker扫描工具) https://github.com/GoSecure/break-fast-serial (借助DNS解析来检测Java反序列化漏洞工具) https://github.com/dirtycow/dirtycow.github.io (脏牛提权漏洞exp) https://github.com/code-scan/dzscan (首款集成化的Discuz扫描工具) https://github.com/chuhades/CMS-Exploit-Framework (一款简洁优雅的CMS扫描利用框架) https://github.com/lijiejie/IIS_shortname_Scanner (IIS短文件名暴力枚举漏洞利用工具) https://github.com/coffeehb/SSTIF (一个Fuzzing服务器端模板注入漏洞的半自动化工具) https://github.com/cr0hn/dockerscan (Docker扫描工具) https://github.com/m4ll0k/WPSeku (一款精简的wordpress扫描工具) https://github.com/rastating/wordpress-exploit-framework (集成化wordpress漏洞利用框架) https://github.com/ilmila/J2EEScan (用于扫描J2EE应用的一款burpsuite插件) https://github.com/riusksk/StrutScan (一款基于perl的strut2的历史漏洞扫描器) https://github.com/D35m0nd142/LFISuite (本地文件包含漏洞利用及扫描工具,支持反弹shell) https://github.com/0x4D31/salt-scanner (基于Salt Open以及Vulners Linux Audit API的linux漏洞扫描器,支持与JIRA、slack平台结合使用) https://github.com/tijme/angularjs-csti-scanner (自动化探测客户端AngularJS模板注入漏洞工具) https://github.com/irsdl/IIS-ShortName-Scanner (Java编写的IIS短文件名暴力枚举漏洞利用工具) https://github.com/swisskyrepo/Wordpresscan (基于WPScan以及WPSeku的优化版wordpress扫描器) https://github.com/CHYbeta/cmsPoc (CMS渗透测试框架) https://github.com/rudSarkar/crlf-injector (CRLF注入漏洞批量扫描) https://github.com/3gstudent/Smbtouch-Scanner (自动化扫描内网中存在的由shadow brokers泄露的ETERNAL系列漏洞) https://github.com/utiso/dorkbot (通过定制化的谷歌搜索引擎进行漏洞页面搜寻及扫描) https://github.com/OsandaMalith/LFiFreak (本地文件包含漏洞利用及扫描工具,支持反弹shell) https://github.com/mak-/parameth (用于枚举脚本的GET/POST未知参数字段) https://github.com/Lucifer1993/struts-scan (struts2漏洞全版本检测和利用工具) https://github.com/hahwul/a2sv (SSL漏洞扫描,例如心脏滴血漏洞等) https://github.com/NullArray/DorkNet (基于搜索引擎的漏洞网页搜寻) https://github.com/NickstaDB/BaRMIe (用于攻击爆破Java Remote Method Invocation服务的工具) https://github.com/RetireJS/grunt-retire (扫描js扩展库的常见漏洞) https://github.com/kotobukki/BDA (针对hadoop/spark等大数据平台的的漏洞探测工具) https://github.com/jagracey/Regex-DoS (RegEx 拒绝服务扫描器) https://github.com/milesrichardson/docker-onion-nmap (使用nmap扫描Tor网络上隐藏的"onion"服务) https://github.com/Moham3dRiahi/XAttacker (Web CMS Exploit 工具,包含针对主流 CMS 的 66 个不同的 Exploits) https://github.com/lijiejie/BBScan (一个迷你的信息泄漏批量扫描脚本) 无线网络(审计)扫描器 https://github.com/savio-code/fern-wifi-cracker/ (无线安全审计工具) https://github.com/m4n3dw0lf/PytheM (Python网络/渗透测试工具) https://github.com/P0cL4bs/WiFi-Pumpkin (无线安全渗透测试套件) https://github.com/MisterBianco/BoopSuite (无线网络审计工具,支持2-5GHZ频段) https://github.com/DanMcInerney/LANs.py (ARP欺骗,无线网络劫持) https://github.com/besimaltnok/PiFinger (检查wifi是否是"大菠萝"所开放的热点,并给予网络评分) https://github.com/derv82/wifite2 (自动化无线网络攻击工具wifite的重构版本) 局域网络(本地网络)扫描器 https://github.com/sowish/LNScan (基于BBScan via.lijiejie的本地网络扫描) https://github.com/niloofarkheirkhah/nili (网络扫描,中间人攻击,协议检测与逆向) https://github.com/SkyLined/LocalNetworkScanner (基于javascript的本地网络扫描) 代码审计工具或扫描器 https://github.com/wufeifei/cobra (白盒代码安全审计系统) https://github.com/OneSourceCat/phpvulhunter (静态php代码审计) https://github.com/Qihoo360/phptrace (跟踪、分析PHP运行情况的工具) https://github.com/ajinabraham/NodeJsScan (NodeJS应用代码审计) https://github.com/shengqi158/pyvulhunter (Python应用审计) https://github.com/presidentbeef/brakeman ( Ruby on ... 综合来看,fuzzdb-collect在同类工具中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。 {card-default label="? 工具信息" /} ? 工具名称:fuzzdb-collect ? 开发作者:euphratica ? 工具描述:网络上安全资源的搜集 ? 开发语言:Python ? 开源协议:未知开源协议 ⭐ Star数:2 | ? Fork数:1 ? 更新时间:2026年08月06日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/euphratica/fuzzdb-collect/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/euphratica/fuzzdb-collect.git"}
-
2026年值得收藏的开源项目:UCenter 源码分享 UCenter 今天给大家分享一款基于PHP开发的开源项目——UCenter。这个项目在Gitee上获得了22个Star,8次Fork,说明还是有不少开发者在使用和关注的。项目主要特点是UCenter 2.0 官方开源版,简体中文 UTF8 编码,适合需要快速搭建网站的开发者和站长使用。 项目功能介绍 ========================================= UCenter 2.0 全新安装文档 安装前准备 PHP 7、MySQL 5.7、Redis(如果需要使用 API 接口) 将 upload 文件夹下所有的文件上传 设置如下文件夹权限为可写权限, Linux 系统设置 777 ./data ./data/avatar ./data/backup ./data/cache ./data/logs ./data/tmp ./data/view 通过浏览器访问 https://您的域名/UC目录/install/, 根据提示填写 MySQL 配置信息、管理员账号信息 完成安装 ========================================= UCenter 2.0 升级安装文档 1、确保 PHP 必须为 PHP 7,如不满足请先升级 2、备份旧 UCenter 目录 ./uc_server 和数据库 3、将 upload 文件夹下所有的文件上传覆盖到旧 UCenter 目录原文件 4、如果 UCenter 应用为 Discuz! X3.4 版本,请在 ./data/config.inc.php 结尾添加 define('UC_PASSWORD_WITH_SALT', true); 5、如果需要使用 API 接口,请先准备 Redis,然后在 ./data/config.inc.php 结尾添加 define('UC_REDIS_HOST', '127.0.0.1'); define('UC_REDIS_PORT', 6379); define('UC_REDIS_CONNECT', 1); define('UC_REDIS_TIMEOUT', 0); define('UC_REDIS_PASS', ''); define('UC_REDIS_DB', 0); define('UC_REDIS_KEYPREFIX', 'uc_'); 酌情修改相关配置 6、通过浏览器访问 https://您的域名/UC目录/ 登录管理中心 7、完成升级 以上就是关于UCenter的简单介绍。这个项目的代码结构清晰,文档也比较完善,对于PHP初学者来说也是一个不错的学习资源。有兴趣的朋友可以通过下方链接下载源码体验一下。 {card-default label="? 项目信息" /} ? 项目名称:UCenter ? 开发作者:Discuzx ? 项目描述:UCenter 2.0 官方开源版,简体中文 UTF8 编码 ? 开发语言:PHP ? 开源协议:未知开源协议 ⭐ Star数:22 | ? Fork数:8 ? 更新时间:2026年08月30日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/Discuz/UCenter/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/Discuz/UCenter.git"}
-
2026年值得收藏的开源项目:NIUSHOP 开源商城 V6 开源版 源码分享 今天给大家分享一款基于PHP开发的开源项目——NIUSHOP 开源商城 V6 开源版。这个项目在Gitee上获得了14676个Star,1348次Fork,说明还是有不少开发者在使用和关注的。项目主要特点是NIUSHOP开源商城 V6,优秀的架构设计!代码干净,高质量,为开发者而生!前后端API接口分离!前端采用最流行技术Vite+TypeScript+Vue3+ElementPlus,国内首例使用TP8 、PHP8、MYSQL8最新技术。 内置代码生成器,插件生成器,一键云编译、一键云部署、一键小程序发布。是一款快速搭建开发企业级应用的软件系统。100%开源无加密!,适合需要快速搭建网站的开发者和站长使用。 项目功能介绍 输入图片说明 niucloud-admin是什么? niucloud-admin是一款快速开发通用管理后台框架,前端采用最新的技术栈Vite+TypeScript+Vue3+ElementPlus最流行技术架构,后台结合PHP8、Java SDK、Python等主流后端语言搭建,内置集成用户权限、代码生成器、表单设计、云存储、短信发送、素材中心、 niucloud-admin采用的技术亮点 后台php采用thinkphp8+php8+mysql,支持composer快速安装扩展,支持redis缓存以及消息队列,支持多语言设计开发,同时开发采用严格的restful的api设计开发。 后台前后端分离采用element-plus、vue3.0、typescript、vite、pina等前端技术,同时使用i18n支持国际化多语言开发。 - 操作指南 [ | 服务市场 | 使用手册 | 二开手册 | API接口手册 | 论坛地址 演示地址 管理后台演示网址:[ 查看 ] http://v6.site.niucloud.com 账号:admin 密码:123456 H5前端演示网址:[ 查看 ] https://v6.site.niucloud.com/wap/ 账号:admin 密码:123456 开源使用须知 1.允许用于个人学习、毕业设计、教学案例、公益事业、商业使用; 2.本框架应用源代码所有权和著作权归niucloud官方所有,基于niucloud-admin框架开发的应用,所有权和著作权归应用开发商所有。但必须明确声明是基于niucloud-admin框架开发,请自觉遵守,否则产生的一切任何后果责任由侵权者自负; 3.禁止修改框架代码并再次发布框架衍生版等与niucloud-admin框架产生恶意竞争或对抗的行为; 4.本框架源码全部开源;包括前端,后端,无任何加密; 5.商用请仔细审查代码和漏洞,不得用于任一国家许可范围之外的商业应用,产生的一切任何后果责任自负; 6.一切事物有个人喜好的标准,本开源代码意在分享,不喜勿喷。 版权信息 版权所有Copyright © 2015-2030 niucloud-admin 版权所有 All rights reserved。 杭州数字云动科技有限公司 杭州牛之云科技有限公司 提供技术支持 以上就是关于NIUSHOP 开源商城 V6 开源版的简单介绍。这个项目的代码结构清晰,文档也比较完善,对于PHP初学者来说也是一个不错的学习资源。有兴趣的朋友可以通过下方链接下载源码体验一下。 {card-default label="? 项目信息" /} ? 项目名称:NIUSHOP 开源商城 V6 开源版 ? 开发作者:niushop ? 项目描述:NIUSHOP开源商城 V6,优秀的架构设计!代码干净,高质量,为开发者而生!前后端API接口分离!前端采用最流行技术Vite+TypeScript+Vue3+ElementPlus,国内首例使用TP8 、PHP8、MYSQL8最新技术。 内置代码生成器,插件生成器,一键云编译、一键云部署、一键小程序发布。是一款快速搭建开发企业级应用的软件系统。100%开源无加密! ? 开发语言:PHP ? 开源协议:未知开源协议 ⭐ Star数:14676 | ? Fork数:1348 ? 更新时间:2026年09月06日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/niushop-team/niushop/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/niushop-team/niushop.git"}
-
nmap 功能特性与应用场景 推荐一个实用的开源工具——nmap。项目由nmap开发维护,GitHub上获得了 13532 个Star。简单来说,它是一款Nmap -网络映射器。官方SVN存储库的Github镜像。,对于站长和开发者来说是个不错的工具。 工具功能介绍 Nmap ====Nmap is released under a custom license, which is based on (but not compatible with) GPLv2. The Nmap license allows free usage by end users, and we also offer a commercial license for companies that wish to redistribute Nmap technology with their products. See Nmap Copyright and Licensing for full details.The latest version of this software as well as binary installers for Windows, macOS, and Linux (RPM) are available from Nmap.orgFull documentation is also available on the Nmap.org website.Questions and suggestions may be sent to the Nmap-dev mailing list.Installing Ideally, you should be able to just type:./configure make make installFor far more in-depth compilation, installation, and removal notes, read the Nmap Install Guide on Nmap.org.Using Nmap Nmap has a lot of features, but getting started is as easy as running `nmap scanme.nmap.org. Running nmap` without any parameters will give a helpful list of the most common options, which are discussed in depth in [the man page](https://nmap.org/book/man.html). Users who prefer a graphical interface can use the included Zenmap front-end.Contributing Information about filing bug reports and contributing to the Nmap project can be found in the HACKING and CONTRIBUTING.md files. {card-default label="? 工具信息" /} ? 项目地址:https://github.com/nmap/nmap ⭐ Star数:13532 ? 开发语言:C ? 项目描述:Nmap -网络映射器。官方SVN存储库的Github镜像。 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/nmap/nmap/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/nmap/nmap"} 总的来说,nmap是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
beef 安装配置与使用指南 推荐一个实用的开源工具——**beef**。项目由beefproject开发维护,GitHub上获得了 **11003** 个Star。简单来说,它是一款Browser Exploitation Framework项目,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 ===============================================================================Copyright (c) 2006-2026 Wade Alcorn - wade@bindshell.net Browser Exploitation Framework (BeEF) - https://beefproject.com See the file 'doc/COPYING' for copying permission===============================================================================What is BeEF? -------------__BeEF__ is short for __The Browser Exploitation Framework__. It is a penetration testing tool that focuses on the web browser.Amid growing concerns about web-borne attacks against clients, including mobile clients, BeEF allows the professional penetration tester to assess the actual security posture of a target environment by using client-side attack vectors. Unlike other security frameworks, BeEF looks past the hardened network perimeter and client system, and examines exploitability within the context of the one open door: the web browser. BeEF will hook one or more web browsers and use them as beachheads for launching directed command modules and further attacks against the system from within the browser context.Get Involved ------------You can get in touch with the BeEF team. Just check out the following:__Please, send us pull requests!____Web:__ https://beefproject.com/__Bugs:__ https://github.com/beefproject/beef/issues__Security Bugs:__ security@beefproject.com__Twitter:__ [@beefproject](https://twitter.com/beefproject)__Discord:__ https://discord.gg/25wT2P8pwxRequirements ------------* Operating System: Mac OSX 10.5.0 or higher / modern Linux. Note: Windows is not supported. * [Ruby](https://www.ruby-lang.org): 3.0 or newer * [SQLite](http://sqlite.org): 3.x * [Node.js](https://nodejs.org): 10 or newer * The gems listed in the Gemfile: https://github.com/beefproject/beef/blob/master/Gemfile * Selenium is required on OSX: `brew install selenium-server-standalone` (See https://github.com/shvets/selenium)Quick Start -----------__The following is for the impatient.__The `install` script installs the required operating system packages and all the prerequisite Ruby gems:$ ./install For full installation details, please refer to [INSTALL.txt](https://github.com/beefproject/beef/blob/master/INSTALL.txt) or the [Installation](https://github.com/beefproject/beef/wiki/Installation) page on the wiki.Upon successful installation, be sure to read the [Configuration](https://github.com/beefproject/beef/wiki/Configuration) page on the wiki for important details on configuring and securing BeEF.Documentation ---* [User Guide](https://github.com/beefproject/beef/wiki#user-guide) * [Frequently Asked Questions](https://github.com/beefproject/beef/wiki/FAQ) * [JSdocs](https://beefproject.github.io/beef/index.html)Usage -----To get started, simply execute beef and follow the instructions:$ ./beef {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/beefproject/beef](https://github.com/beefproject/beef) ⭐ Star数:11003 ? 开发语言:JavaScript ? 项目描述:Browser Exploitation Framework项目 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/beefproject/beef/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/beefproject/beef"}总的来说,**beef**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
wpscan - 安全从业者的得力助手 推荐一个实用的开源工具——wpscan。项目由wpscanteam开发维护,GitHub上获得了 9759 个Star。简单来说,它是一款WPScan WordPress安全扫描仪。专为安全专业人员和博客维护人员编写,以测试其WordPress网站的安全性。通过,对于站长和开发者来说是个不错的工具。 工具功能介绍 WPScan WordPress Security Scanner WPScan WordPress Vulnerability Database - WordPress Security Plugin Prerequisites- (Optional but highly recommended: rbenv) Ruby >= 3.3 - Recommended: latest stable Curl >= 7.72 - Recommended: latest stable The 7.29 has a segfault The {card-default label="? 工具信息" /} ? 项目地址:https://github.com/wpscanteam/wpscan ⭐ Star数:9759 ? 开发语言:Ruby ? 项目描述:WPScan WordPress安全扫描仪。专为安全专业人员和博客维护人员编写,以测试其WordPress网站的安全性。通过 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/wpscanteam/wpscan/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/wpscanteam/wpscan"} 总的来说,wpscan是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
分享一个不错的开源工具:osv-scanner 推荐一个实用的开源工具——**osv-scanner**。项目由google开发维护,GitHub上获得了 **10990** 个Star。简单来说,它是一款用Go编写的漏洞扫描程序,使用https://osv.dev提供的数据,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 ---Use OSV-Scanner to find existing vulnerabilities affecting your project's dependencies. OSV-Scanner provides an officially supported frontend to the [OSV database](https://osv.dev/) and CLI interface to [OSV-Scalibr](https://github.com/google/osv-scalibr) that connects a project’s list of dependencies with the vulnerabilities that affect them.OSV-Scanner supports a wide range of project types, package managers and features, including but not limited to:- **Languages:** C/C++, Dart, Elixir, Go, Java, Javascript, PHP, Python, R, Ruby, Rust. - **Package Managers:** npm, pip, yarn, maven, go modules, cargo, gem, composer, nuget and others. - **Operating Systems:** Detects vulnerabilities in OS packages on Linux systems. - **Containers:** Scans container s for vulnerabilities in their base s and included packages. - **Guided Remediation:** Provides recommendations for package version upgrades based on criteria such as dependency depth, minimum severity, fix strategy, and return on investment.OSV-Scanner uses the extensible [OSV-Scalibr](https://github.com/google/osv-scalibr) library under the hood to provide this functionality. If a language or package manager is not supported currently, please file a [feature request.](https://github.com/google/osv-scanner/issues)The underlying database, [OSV.dev](https://osv.dev/) has several benefits in comparison with closed source advisory databases and scanners:- Covering most open source language and OS ecosystems (including [Git](https://osv.dev/list?q=&ecosystem=GIT)), it’s comprehensive. - Each advisory comes from an open and authoritative source (e.g. [GitHub Security Advisories](https://github.com/github/advisory-database), [RustSec Advisory Database](https://github.com/rustsec/advisory-db), [Ubuntu security notices](https://github.com/canonical/ubuntu-security-notices/tree/main/osv)) - Anyone can suggest improvements to advisories, resulting in a very high quality database. - The OSV format unambiguously stores information about affected versions in a machine-readable format that precisely maps onto a developer’s list of packagesThe above all results in accurate and actionable vulnerability notifications, which reduces the time needed to resolve them. Check out [OSV.dev](https://osv.dev/) for more details!## Basic installationTo install OSV-Scanner, please refer to the [installation section](https://google.github.io/osv-scanner/installation) of our documentation. OSV-Scanner releases can be found on the [releases page](https://github.com/google/osv-scanner/releases) of the GitHub repository. The recommended method is to download a prebuilt binary for your platform. Alternatively, you can use `go install github.com/google/osv-scanner/v2/cmd/osv-scanner@latest` to build it from source. ## Key FeaturesFor more information, please read our [detailed documentation](https://google.github.io/osv-scanner) to learn how to use OSV-Scanner. For detailed information about each feature, click their titles in this README.Please note: These are the instructions for the latest OSV-Scanner V2 beta. If you are using V1, checkout the V1 [README](https://github.com/google/osv-scanner-v1) and [documentation](https://google.github.io/osv-scanner-v1/) instead. ### [Scanning a source directory](https://google.github.io/osv-scanner/usage) bash $ osv-scanner scan source -r /path/to/your/dir This command will recursively scan the specified directory for any supported package files, such as `package.json`, `go.mod`, `pom.xml`, etc. and output any discovered vulnerabilities.OSV-Scanner has the option of using call analysis to determine if a vulnerable function is actually being used in the project, resulting in fewer false positives, and actionable alerts.OSV-Scanner can also detect vendored C/C++ code for vulnerability scanning. See [here](https://google.github.io/osv-scanner/usage/#cc-scanning) for details. #### Supported LockfilesOSV-Scanner supports 11+ language ecosystems and 19+ lockfile types. To check if your ecosystem is covered, please check out our [detailed documentation](https://google.github.io/osv-scanner/supported-languages-and-lockfiles/#supported-lockfiles). ### [Container Scanning](https://google.github.io/osv-scanner/usage/scan-)OSV-Scanner also supports comprehensive, layer-aware scanning for container s to detect vulnerabilities in the following operating system packages and language-specific dependencies.| Distro Support | Language Artifacts Support | | -------------- | -------------------------- | | Alpine OS | Go | | Debian | Java | | Ubuntu | Node | | | Python |See the [full documentation](https://google.github.io/osv-scanner/supported-languages-and-lockfiles/#supported-artifacts) for details on support.**Usage**: bash $ osv-scanner scan my--name:tag  ### [License Scanning](https://google.github.io/osv-scanner/usage/license-scanning/)Check your dependencies' licenses using deps.dev data. For a summary: bash osv-scanner --licenses path/to/repository To check against an allowed license list (SPDX format): bash osv-scanner --licenses="MIT,Apache-2.0" path/to/directory ### [Offline Scanning](https://google.github.io/osv-scanner/usage/offline-mode/)Scan your project against a local OSV database. No network connection is required after the initial database download. The database can also be manually downloaded. bash osv-scanner --offline --download-offline-databases ./path/to/your/dir ### [Guided Remediation](https://google.github.io/osv-scanner/experimental/guided-remediation/) (Experimental)> [!WARNING] > Guided remediation (the `fix` command) can be risky when run on untrusted projects. It may trigger the package manager to execute scripts or follow external registries specified in the project. Please ensure you trust the source code and artifacts before proceeding.OSV-Scanner provides guided remediation, a feature that suggests package version upgrades based on criteria such as dependency depth, minimum severity, fix strategy, and return on investment. We currently support remediating vulnerabilities in the following files:| Ecosystem | File Format (Type) | Supported Remediation Strategies | | :-------- | :----------------------------- | :--------------------------------------------------------------------------------------------------------------------- | | npm | `package-lock.json` (lockfile) | [`in-place`](https://google.github.io/osv-scanner/experimental/guided-remediation/#in-place-lockfile-changes) | | npm | `package.json` (manifest) | [`relock`](https://google.github.io/osv-scanner/experimental/guided-remediation/#relock-and-relax-direct-dependencies) | | Maven | `pom.xml` (manifest) | [`override`](https://google.github.io/osv-scanner/experimental/guided-remediation/#override-dependency-versions) |This is available as a headless CLI command, as well as an interactive mode.#### Example (for npm) bash $ osv-scanner fix \ --max-depth=3 \ --min-severity=5 \ --ignore-dev \ --strategy=in-place \ -L path/to/package-lock.json #### Interactive mode (for npm) bash $ osv-scanner fix \ -M path/to/package.json \ -L path/to/package-lock.json ## Data Sources and PrivacyOSV-Scanner communicates with the following external services during operation: ### [OSV.dev API](https://osv.dev/)The primary data source for vulnerability information. OSV-Scanner queries this API to check packages for known vulnerabilities and to identify vendored C/C++ dependencies. Data sent includes package names, versions, ecosystems, and file hashes. Use [`--offline` mode](https://google.github.io/osv-scanner/usage/offline-mode/) to disable network requests and scan against a local database instead. ### [deps.dev API](https://docs.deps.dev/api/)Used for supplementary package information:- **Dependency resolution**: Resolves dependency graphs for vulnerability scanning and remediation - **Container scanning**: Queries container metadata for vulnerability detection - **License scanning** (`--licenses` flag): Retrieves license information for packages - **Package deprecation**: Checks if packages are deprecatedData sent includes package names, versions, and ecosystems. No source code is transmitted.### Package RegistriesWhen using native registry for dependency resolution (instead of deps.dev), OSV-Scanner may query:| Registry | URL | Used For | | ------------- | ------------------------------ | ------------------------------------ | | Maven Central | `repo.maven.apache.org/maven2` | Maven package metadata and POM files | | npm Registry | `registry.npmjs.org` | npm package metadata | | PyPI | `pypi.org` | Python package metadata |## Contribute ### Report ProblemsIf you have what looks like a bug, please use the [GitHub issue tracking system](https://github.com/google/osv-scanner/issues). Before you file an issue, please search existing issues to see if your issue is already covered. ### Contributing code to `osv-scanner`See [CONTRIBUTING.md](CONTRIBUTING.md) for documentation on how to contribute code. ## Star History {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/google/osv-scanner](https://github.com/google/osv-scanner) ⭐ Star数:10990 ? 开发语言:Go ? 项目描述:用Go编写的漏洞扫描程序,使用https://osv.dev提供的数据 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/google/osv-scanner/archive/refs/heads/main.zip"} {cloud type="default" title="网盘下载" url="https://github.com/google/osv-scanner"}总的来说,**osv-scanner**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。